
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

A still unpatched zero-day RCE impacts more than 3.5M Exim servers

Experts warn of a critical zero-day vulnerability, tracked as CVE-2023-42115, in all versions of Exim mail transfer agent (MTA) software. A critical zero-day vulnerability, tracked as CVE-2023-42115 (CVSS score 9.8), affects all versions of Exim mail transfer agent (MTA) software. A remote, unauthenticated attacker, can exploit the vulnerability to gain remote code execution (RCE) on Internet-exposed […]

exim

Experts warn of a critical zero-day vulnerability, tracked as CVE-2023-42115, in all versions of Exim mail transfer agent (MTA) software.

A critical zero-day vulnerability, tracked as CVE-2023-42115 (CVSS score 9.8), affects all versions of Exim mail transfer agent (MTA) software. A remote, unauthenticated attacker, can exploit the vulnerability to gain remote code execution (RCE) on Internet-exposed servers.

The flaw is due to an Out-of-bounds Write issue that resides in the SMTP service, it is caused by the lack of proper validation of user-supplied data.

“This vulnerability allows remote attackers to execute arbitrary code on affected installations of Exim. Authentication is not required to exploit this vulnerability.” reads the advisory published by Trend Micro’s Zero Day Initiative (ZDI). “The specific flaw exists within the smtp service, which listens on TCP port 25 by default. The issue results from the lack of proper validation of user-supplied data, which can result in a write past the end of a buffer. An attacker can leverage this vulnerability to execute code in the context of the service account.”

An anonymous researcher disclosed the flaw through the ZDI on June 6, 2022, and ZDI reported the vulnerability to the vendor on June 14, 2022.

On September 25, 2023, ZDI asked for an update and informed the vendor that they intend to publicly disclose the zero-day on September 27, 2023.

The vulnerability has yet to be addressed by the development team, and more than one year has passed.

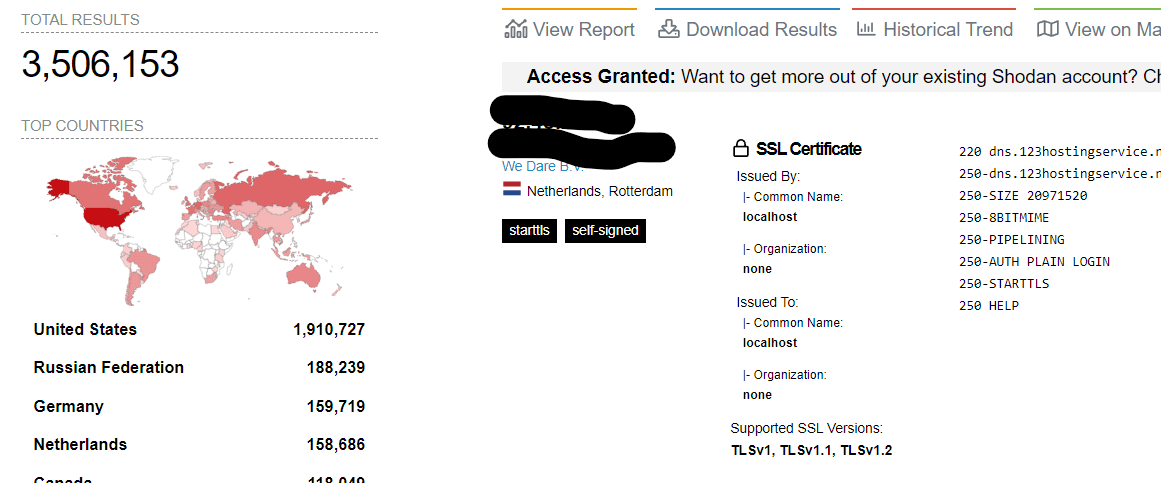
Bleeping Computer reported that more than 3.5 million Exim servers are exposed online.

exim

The only way to mitigate the risk of exploitation for the above issue, is to restrict interaction with the application.

“Given the nature of the vulnerability, the only salient mitigation strategy is to restrict interaction with the application,” concludes ZDI.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Exim mail transfer)


