
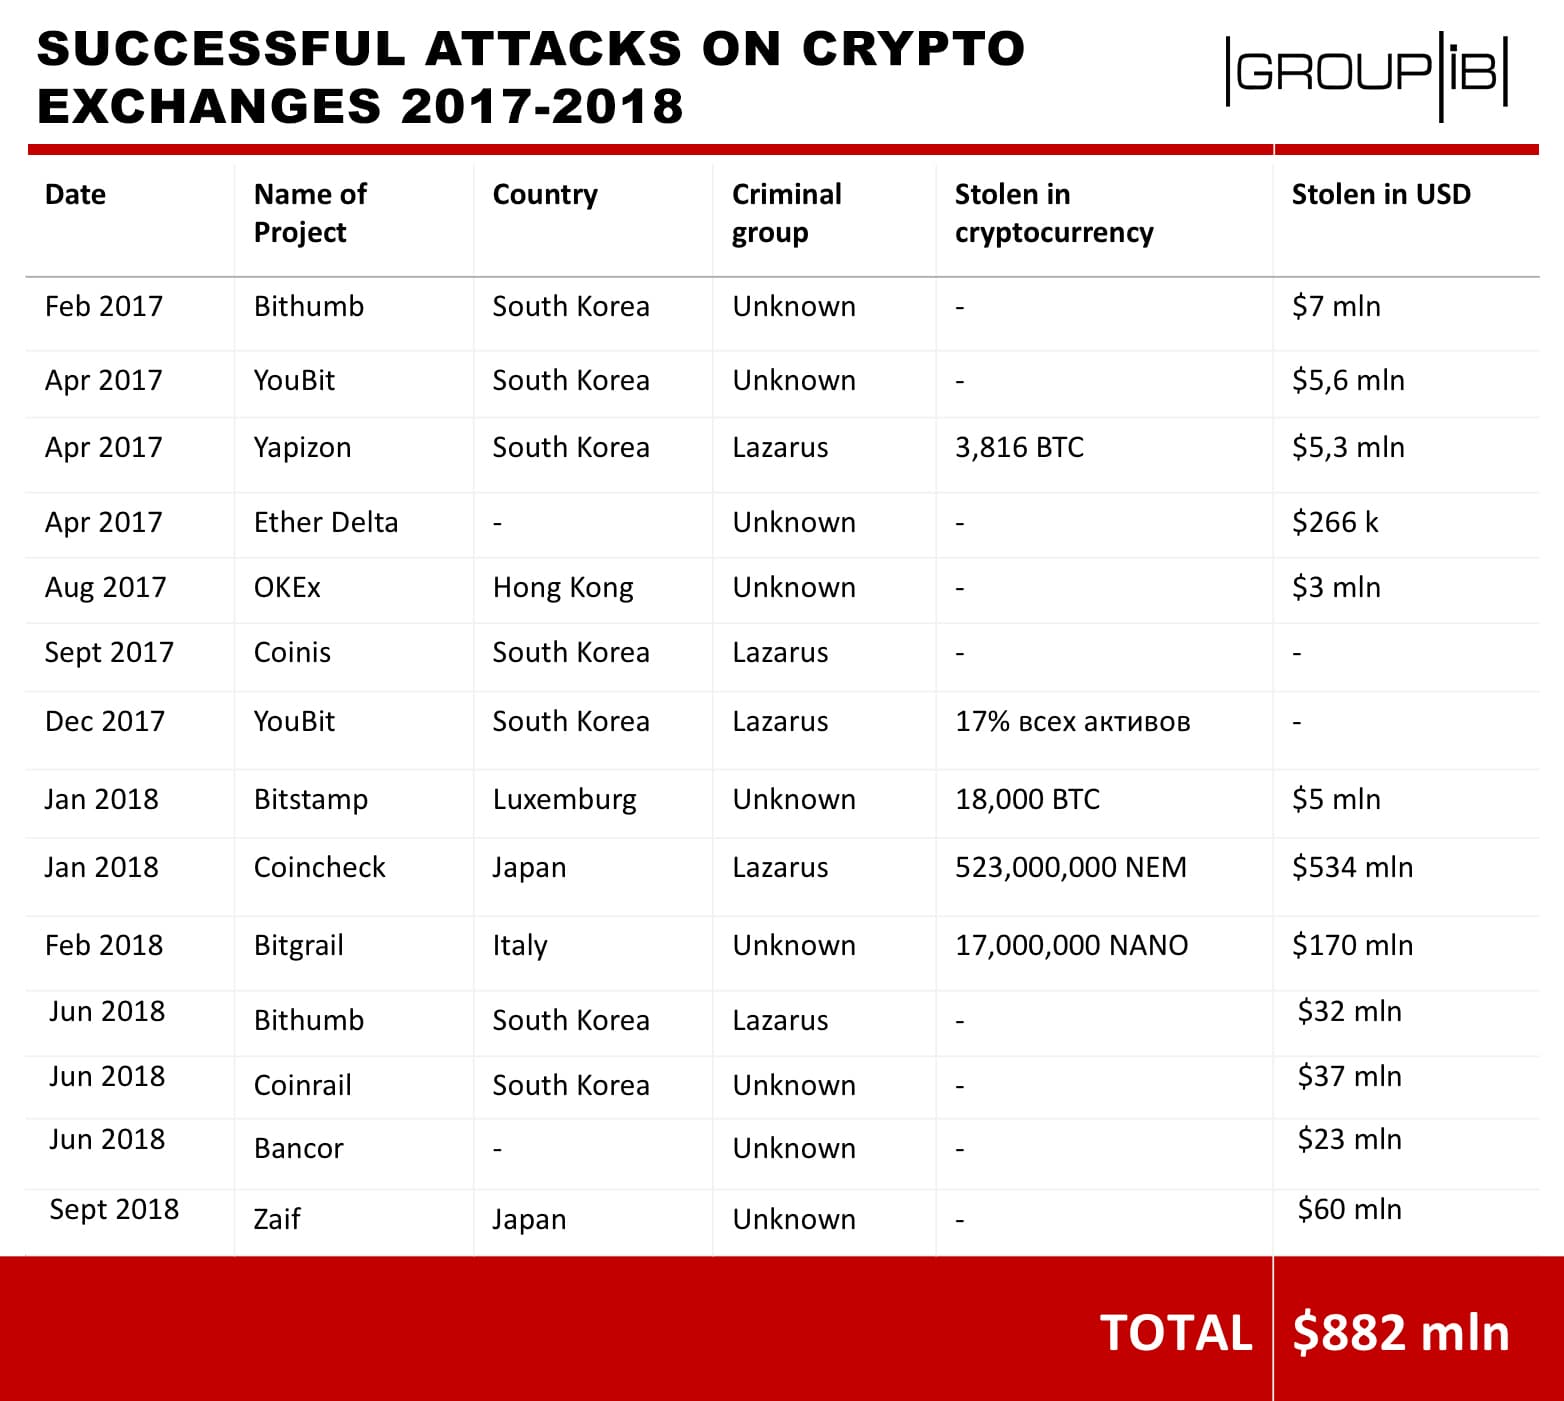
Group-IB has estimated that crypto exchanges suffered a total loss of $882 million due to targeted attacks between 2017 and 2018.
Group-IB, an international company that specializes in preventing cyber attacks,has estimated that cryptocurrency exchanges suffered a total loss of $882 million due to targeted attacks in 2017 and in the first three quarters of 2018. According to Group-IB experts, at least 14 crypto exchanges were hacked. Five attacks have been linked to North Korean hackers from Lazarus state-sponsored group, including the infamous attack on Japanese crypto exchange Coincheck, when $534million in crypto was stolen.
This data was included in the annual Hi-Tech Crime Trends 2018 report, presented by Group-IB CTO, Dmitry Volkov, at the sixth international CyberСrimeCon conference. A separate report chapter is dedicated to the analysis of hackers’ and fraudsters’ activity in crypto industry.
Crypto exchanges: in the footsteps of Lazarus
In most cases, cybercriminals, while attacking cryptocurrency exchanges, use traditional tools and methods, such as spear phishing, social engineering, distribution of malware, and website defacement. One successful attack could bring hackers tens of millions of dollars in crypto funds, whilst reducing the risks of being caught to a minimum: the anonymity of transactions allows cybercriminals to withdraw stolen funds without putting themselves at greater risk.
Spear phishing remains the major vector of attack on corporate networks. For instance, fraudsters deliver malware under the cover of CV spam: they send an email containing a fake CV with the subject line “Engineering Manager for Crypto Currency job” or the file «Investment Proposal.doc» in attachment, that has a malware embedded in the document.
In the last year and a half, the North-Korean state-sponsored Lazarus group attacked at least five cryptocurrency exchanges: Yapizon, Coins, YouBit, Bithumb, Coinckeck. After the local network is successfully compromised, the hackers browse the local network to find workstations and servers used working with private cryptocurrency wallets.

“Last year we warned that hackers competent enough to carry out a targeted attack might have a new target – cryptocurrency exchanges,” — reminded Dmitry Volkov, Group-IB CTO.
“In the last couple of years, crypto exchanges suffered many attacks. Some of the exchanges went bankrupt after the hacks, i.e. Bitcurex, YouBit, Bitgrail. At the beginning of 2018 hackers’ interest in cryptocurrency exchanges ramped up. The most likely cryptocurrency exchange attackers now are Silence, MoneyTaker, and Cobalt.”
ICO: more than 56% of funds were stolen through phishing attacks
Hackers cause serious damage to ICOs: they attack founders, community members, and platforms. In 2017 more than 10% of funds raised through ICOs were stolen, while 80% of projects disappeared with the money without fulfilling any obligations towards their investors.
Yet despite the pessimistic forecasts, the number of funds invested in ICOs increased significantly. In H1 of 2018 alone, ICO projects raised almost $14 billion, which is twice as much as during the entire 2017 ($5,5 billion) — according to CVA and PwC studies. Therefore, cybercriminals can steal more funds in one successful attack.
In 2018, hackers attacked ICOs conducting private funding rounds. For instance, cyber criminals targeted TON project, founded by Pavel Durov, through phishing and managed to steal $35,000 in Ethereum. The worst generally happens on the first day of token sales: a set of DDoS attacks simultaneous with an influx of users, the eruption of Telegram and Slack messages, mailing list spamming.
Phishing remains one of the major vectors of attacks on ICOs: approximately 56% of all funds stolen from ICOs were siphoned off as a result of phishing attacks. On the rise of “the crypto-fever” everyone is striving to purchase tokens, often sold at a significant discount, as fast as possible without paying attention to fine details such as fake domain names. One beg phishing group is capable of stealing roughly $1 million a month.
Phishing attacks against ICO projects are not always aimed at stealing money. This year, there were several cases of investor database theft. This information can be later re-sold on the darknet or used for blackmail.
A relatively new method of fraud on the ICO market was stealing a White Paper of an ICO project and presenting an identical idea under a new brand name. Fraudsters build a website to feature a new brand and a new team using the stolen project description and announce an ICO.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – crypto exchanges, hacking)
[adrotate banner=”5″]
[adrotate banner=”13″]


