Security Affairs
CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

A cyberattack hits Ukraine’s national railway operator Ukrzaliznytsia

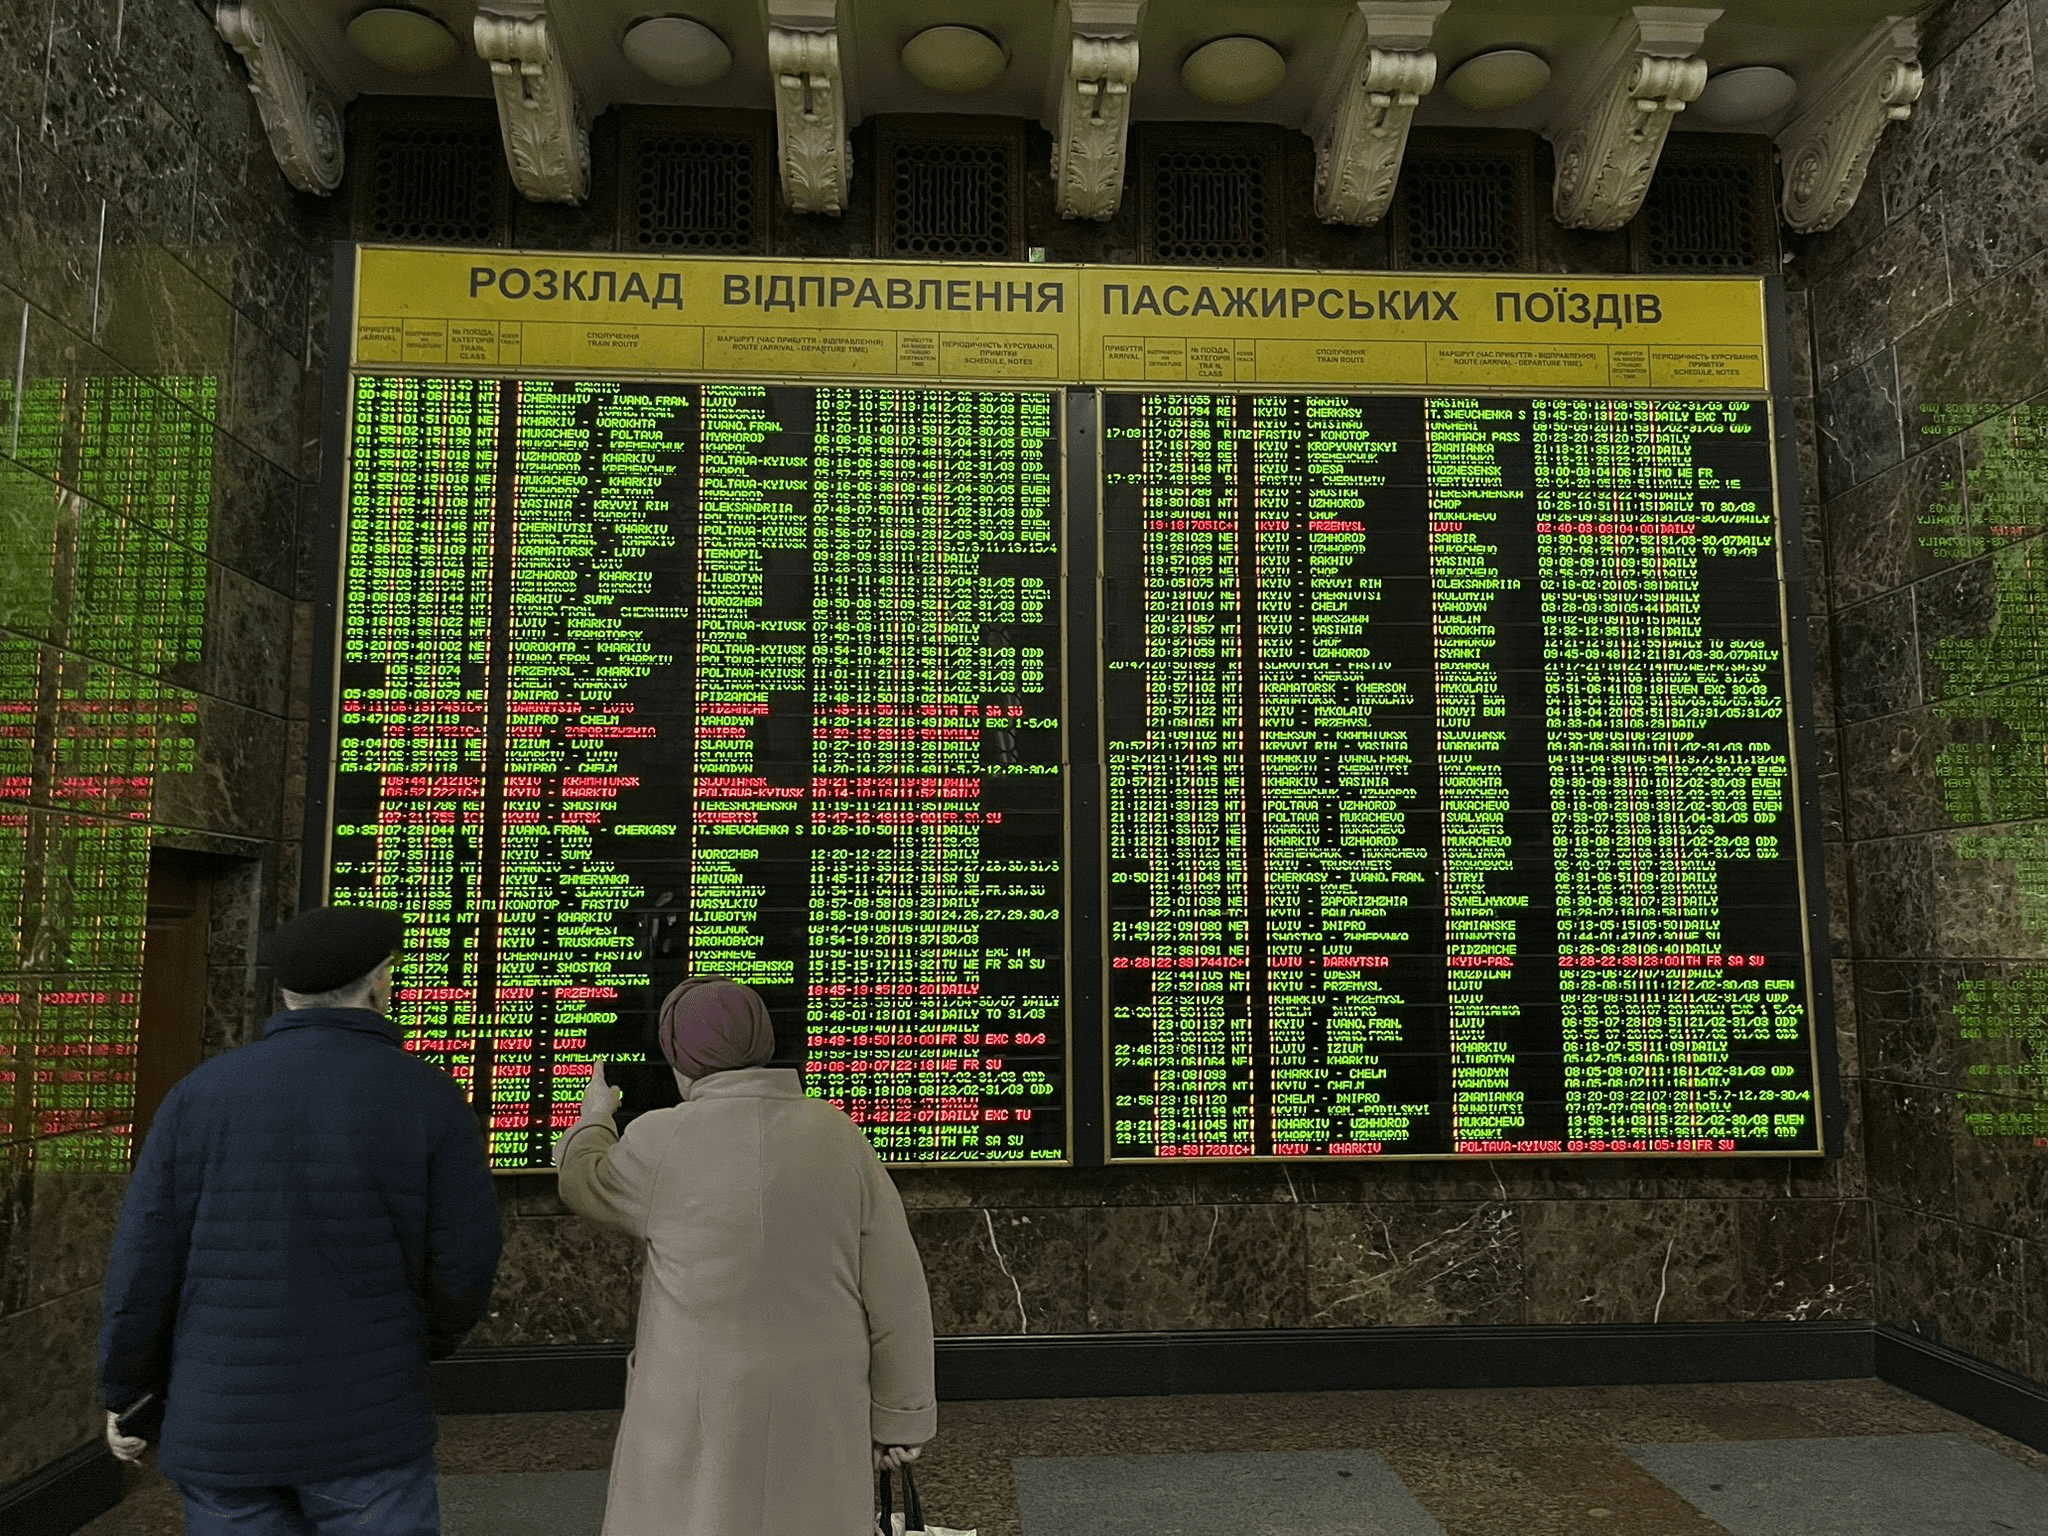
A cyberattack on Ukraine’s national railway operator Ukrzaliznytsia disrupted online ticket services, causing long lines at Kyiv’s station. The Record Media first reported the news of a cyber attack on Ukraine’s national railway operator Ukrzaliznytsia that disrupted online ticket services, causing long lines at Kyiv’s station. The incident led to overcrowding and long delays as […]

Ukraine’s national railway operator

Source: Daryna Antoniuk’s X account

A cyberattack on Ukraine’s national railway operator Ukrzaliznytsia disrupted online ticket services, causing long lines at Kyiv’s station.

The Record Media first reported the news of a cyber attack on Ukraine’s national railway operator Ukrzaliznytsia that disrupted online ticket services, causing long lines at Kyiv’s station.

The incident led to overcrowding and long delays as people were forced to buy physical tickets.

The attack did not impact train operations. Ukrzaliznytsia is investigating the attack and restoring the affected systems with the help of the Cyber Department of the Security Service of Ukraine.

Ukraine’s national railway operator
Source: Daryna Antoniuk’s X account

“The online systems of Ukrzaliznytsia suffered a large-scale targeted cyberattack. The restoration of all systems took the entire past day and continues now.” reads the statement published by the company.

“The key objective of the enemy was not achieved: train movement is stable, running on time without delays, and all operational processes are running in backup mode. The railway continues to operate despite physical attacks on infrastructure, and it cannot be stopped even by the most insidious cyberattacks.”

Railways are essential for Ukraine’s transportation, evacuation, and supply chains amid the ongoing war. With airports closed, Ukrzaliznytsia plays a crucial role in moving people, delivering aid, and exporting goods, underscoring the need to protect critical infrastructure.

“Since Ukrzaliznytsia has been a target of cyberattacks before, the company has implemented backup protocols.” continues the company. “The latest attack was highly systematic, non-trivial, and multi-layered. Therefore, before full restoration from backups, Ukrzaliznytsia specialists, involved partners, the Cyber Department of the SBU, and the Government Computer Emergency Response Team (CERT-UA) under the State Special Communications Service must thoroughly test services for potential vulnerabilities.”

Travelers at Kyiv’s railway station expressed frustration over ticketing delays, as they could no longer purchase tickets online. Authorities did not attribute the attack to a specific threat actor, however, past attacks on Ukraine’s critical infrastructure have been linked to Russian nation-state actors.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Ukraine’s national railway operator)