
Recently I wrote an article related the link between the soar of Bicoin value and expected increased interest of cybercrime to the virtual currency. In the post I anticipated the we will assist to the increase of DDoS attacks and data breach against principal Bitcoin exchanges and services providers, I also introduced the possibility to assist to the rise of malware that could be used to compose botnets dedicated to mining activities.
Recent attacks against Bitcoin exchange Mt. Gox and Instawallet are the demonstration of high interest of cybercrime in the popular virtual currency scheme.
Dmitry Bestuzhev Kaspersky Lab Expert published an interesting article that confirmed my fears, he described a malware in circulation that is using Skype as a vector to spread its code to infect machines with a primary purpose to mine Bitcoins.
The malicious campaign is really recent, the researcher at Kaspersky Lab isolated a new variant of malware that used the popular Skype VOIP client to send messages to the users suggesting them to click on a malicious link to see a picture of themselves online.

Despite the campaign started a few days ago thousands of victims have been already infected clicking on the malicious link proposed through Skype, Kaspersky estimated around 2000 clicks per hour. It’s not the first time that Skype is used to spread malware, in the last week the same research Bestuzhev detected another malware from Venezuela using the same techniques for different purpose.

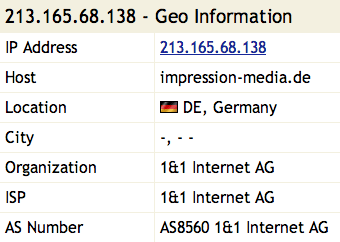
The investigation revealed that the malware hit mainly victims located in Italy then Russia, Poland, Costa Rica, Spain, Germany, Ukraine, the initial dropper is downloaded from a server located in India meanwhile downloads come from the Hotfile.com service. Once infected the victim, the agent drops to the system different pieces of malware, the malicious code connects to its C2 server, with IP address of 213.165.68.138:9000, located in Germany has shown in the following picture:
The researches sustains that we are facing with a multi-purpose malware, but the feature that most attracted the experts is the capability to use the computational resources of victims to mine Bitcoin.
This feature is not new, in the past other security firm such as TrenMicro observed malware able to use victims to generate Bitcoins, in this case the malicious code appears very invasive and noisy because it saturate CPU use for its activities.

Following an excerpt from original post
“The mentioned process runs with the command “bitcoin-miner.exe -a 60 -l no -o http://suppp.cantvenlinea.biz:1942/ -u XXXXXX0000001@gmail.com -p XXXXXXXX” (sensitive data was replaced by XXXXXX) It abuses the CPU of infected machine to mine Bitcoins for the criminal.
As I said the campaign is quite active. If you see your machine is working hard, using all available CPU resources, you may be infected.
The initial dropper is detected by Kaspersky as Trojan.Win32.Jorik.IRCbot.xkt.”
As announced at the beginning of this article it is to predict a rapid increase of cyber criminal operation involving Bitcoins, crime follows the money and the virtual currency in this moment offers many opportunities.
Pierluigi Paganini
(Security Affairs – Bitcoin , malware)


