
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Cylance confirms the legitimacy of data offered for sale in the dark web

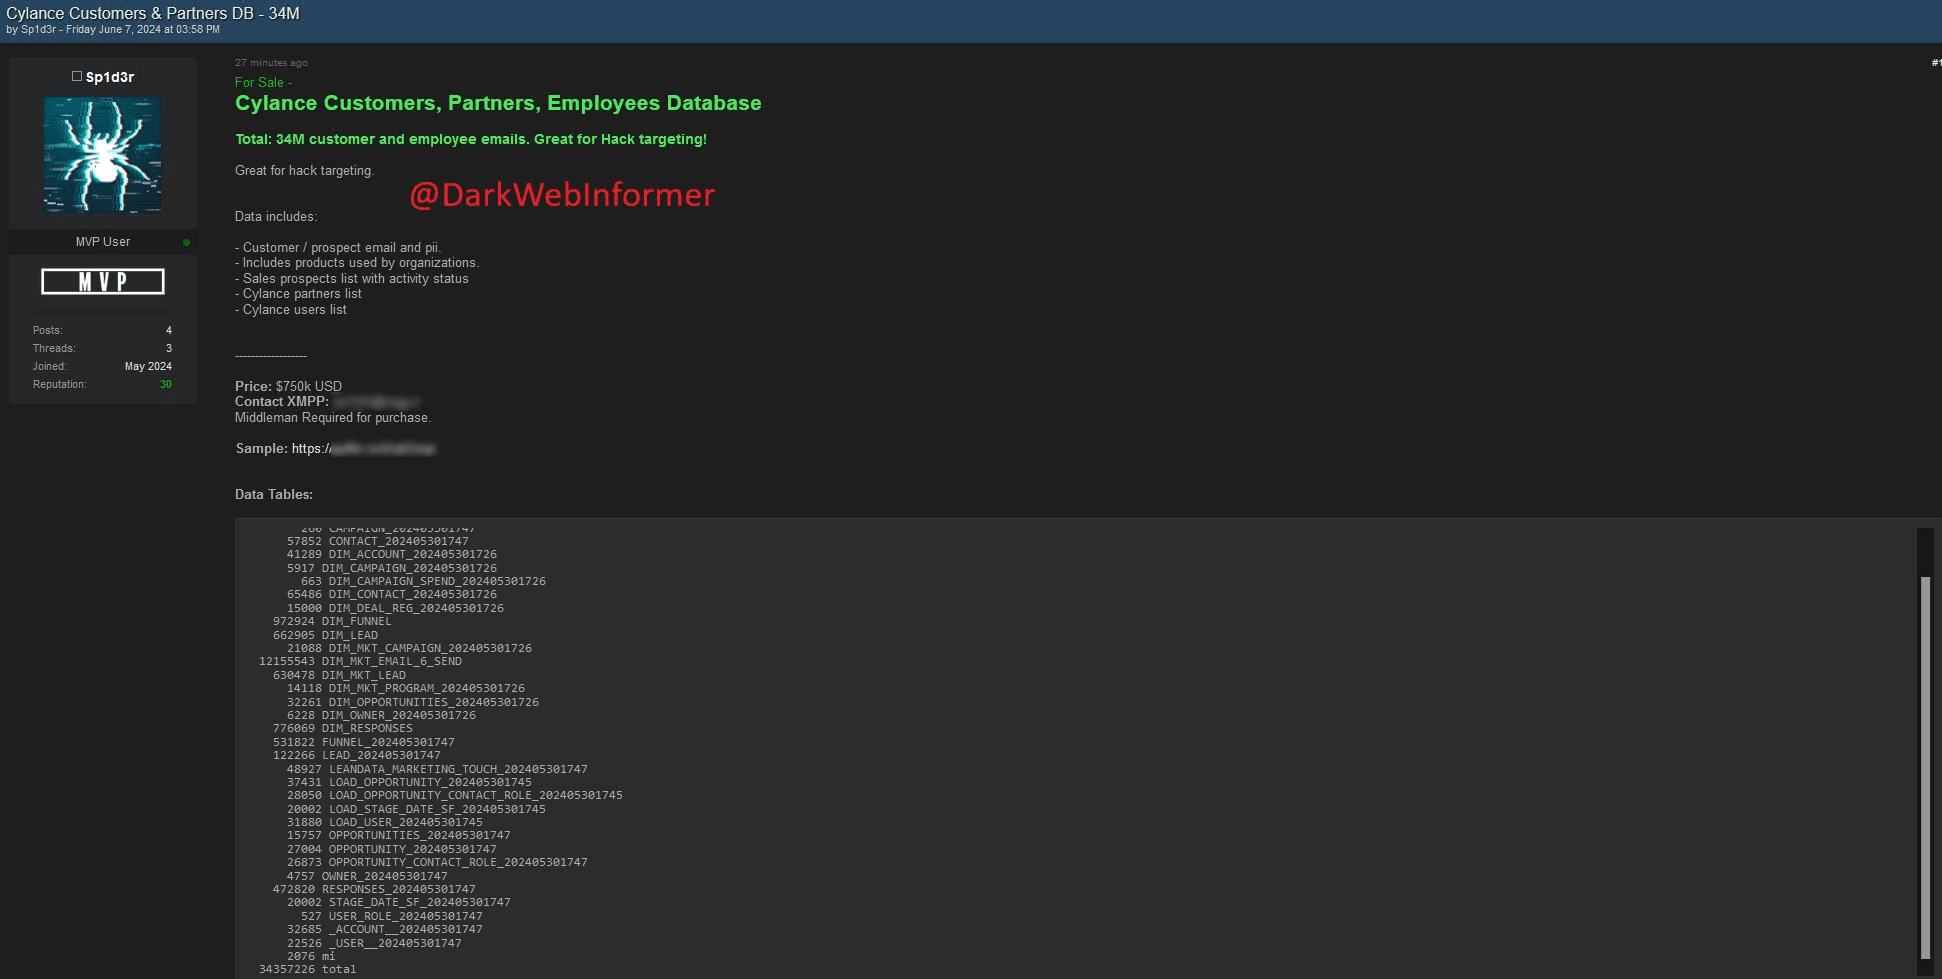
A threat actor is selling the data belonging to BlackBerry’s Cylance cybersecurity unit, he demanded $750,000. A threat actor, that goes online with the moniker Sp1d3r, is selling the stolen data for $750,000. The data includes 34 million customer and employee emails, customer / prospect email and PII, products used by organizations, sales prospect list […]

Cylance

A threat actor is selling the data belonging to BlackBerry’s Cylance cybersecurity unit, he demanded $750,000.

A threat actor, that goes online with the moniker Sp1d3r, is selling the stolen data for $750,000. The data includes 34 million customer and employee emails, customer / prospect email and PII, products used by organizations, sales prospect list with activity status, Cylance partners list and users list.

BlackBerry told several media outlets that it’s aware of the potential data breach and is investigating the alleged incident.

The company states that data was stolen from a third-party platform and appears to be old.

“Based on our initial reviews of the data in question, no current Cylance customers are impacted, and no sensitive information is involved,” BlackBerry told SecurityWeek. “The data in question was accessed from a third-party platform unrelated to BlackBerry and appears to be from 2015-2018, predating BlackBerry’s acquisition of the Cylance product portfolio.”

“We continue to monitor this situation closely and will take all necessary precautions to maintain the integrity of our products and systems and the trust of our customers,” it added

While several experts believe attackers may have obtained the data from the cloud data platform Snowflake, Cylance pointed out that it is currently not a Snowflake customer.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, data breach)


