
A researcher disclosed an arbitrary command injection and hardcoded backdoor issue in multiple end-of-life D-Link NAS models.
A researcher who goes online with the moniker ‘Netsecfish’ disclosed a new arbitrary command injection and hardcoded backdoor flaw, tracked as , tracked as CVE-2024-3273, that impacts multiple end-of-life D-Link Network Attached Storage (NAS) device models.
The flaw affects multiple D-Link NAS devices, including models DNS-340L, DNS-320L, DNS-327L, and DNS-325.
The vulnerability resides in the nas_sharing.cgi uri, the researcher discovered a backdoor facilitated by hardcoded credentials and a command injection vulnerability via the system parameter. An attacker can exploit the flaw to achieve command execution on the affected D-Link NAS devices, gain access to potential access to sensitive information, system configuration alteration, or denial of service.
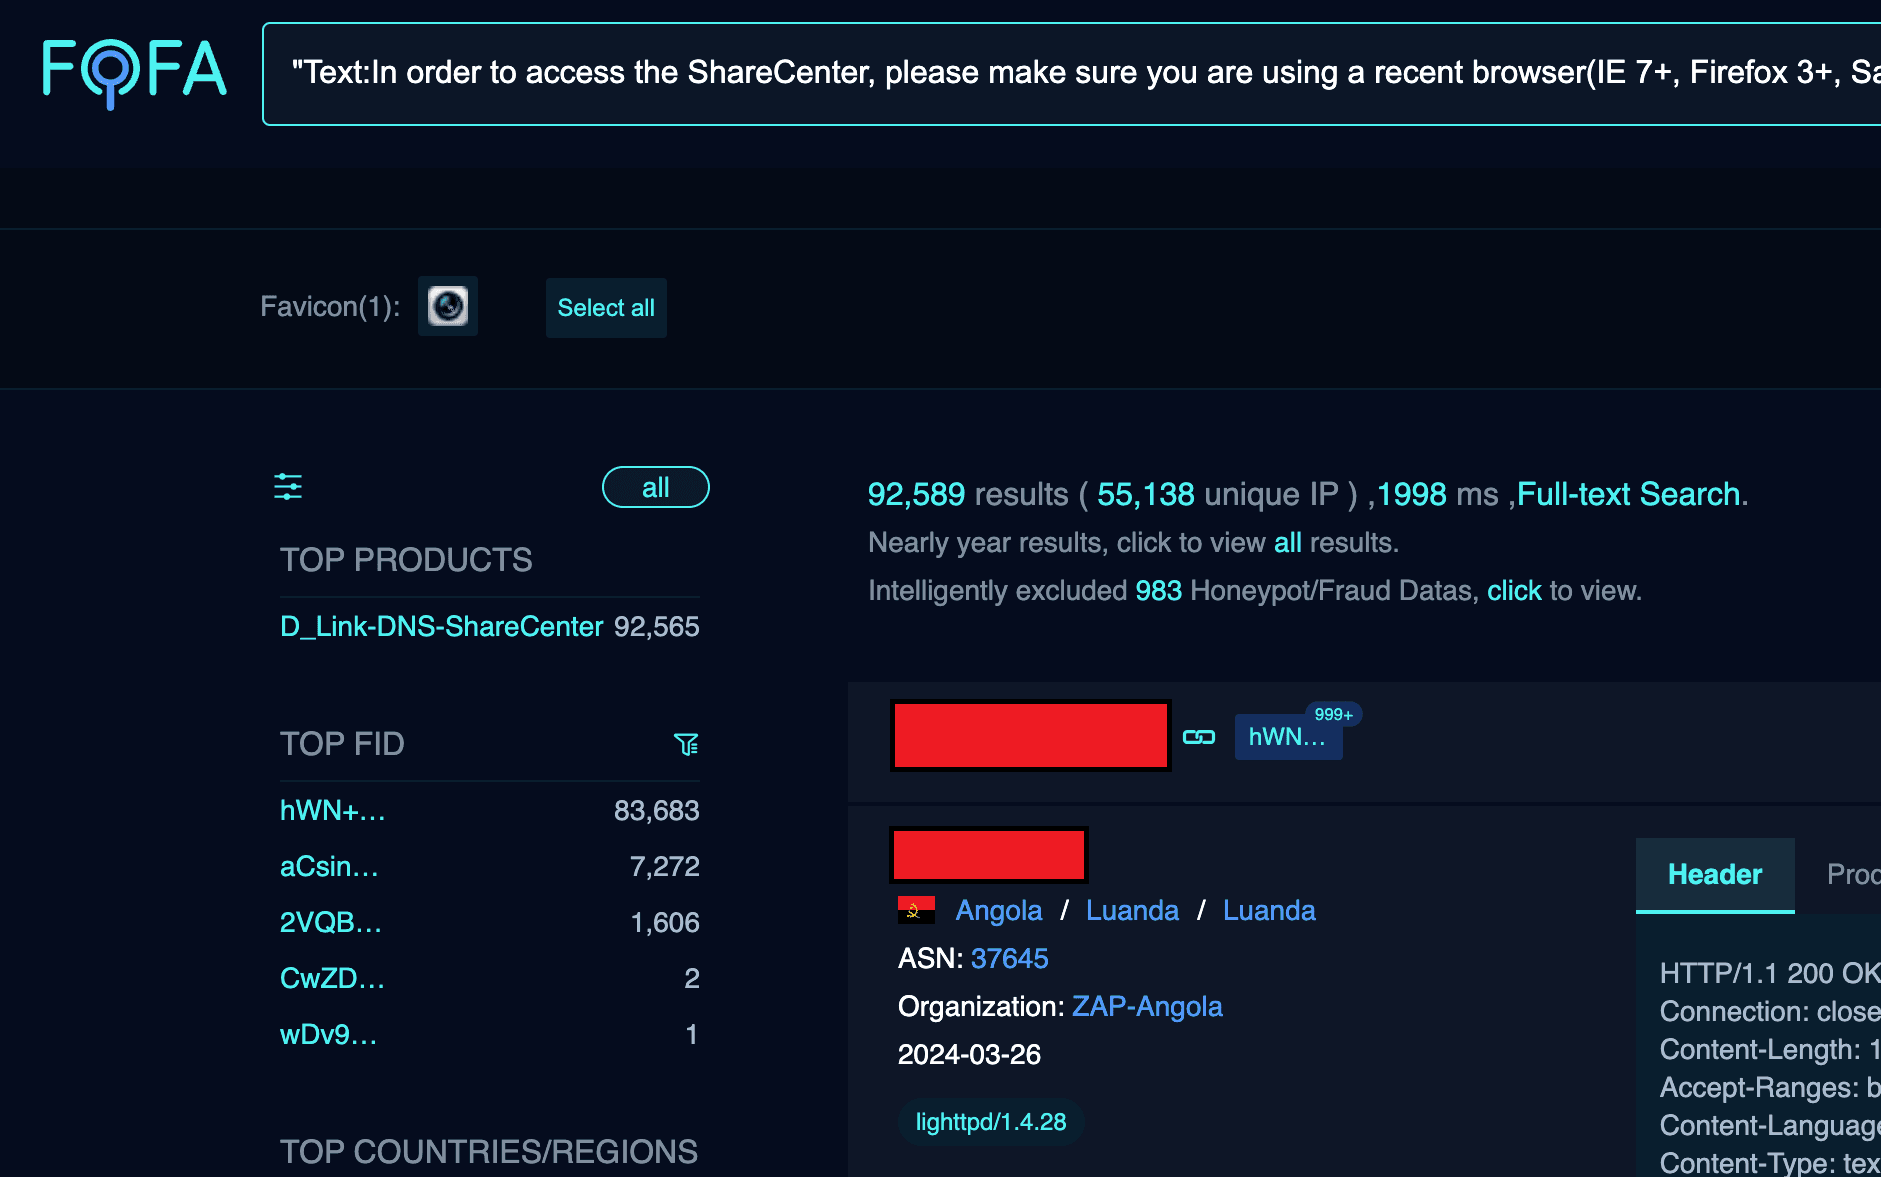
Netsecfish reported that over 92,000 Internet-facing devices are vulnerable.

The request includes parameters for a username (user=messagebus) and an empty field for the password (passwd=). This trick allows attackers to obtain bypass authentication. The command Injection issue is achieved by adding a base64 encoded command to the system parameter in an HTTP GET request. The command is decoded and executed.

“Successful exploitation of this vulnerability could allow an attacker to execute arbitrary commands on the system, potentially leading to unauthorized access to sensitive information, modification of system configurations, or denial of service conditions.” wrote Netsecfish.
The flaw impacts the following devices:
- DNS-320L Version 1.11, Version 1.03.0904.2013, Version 1.01.0702.2013
- DNS-325 Version 1.01
- DNS-327L Version 1.09, Version 1.00.0409.2013
- DNS-340L Version 1.08
The bad news is that owners of the device models have to replace them because the vendor will not release security updates for these NASs because they have reached the end of life (EOL).
“This exploit affects a legacy D-Link products and all hardware revisions, which have reached their End of Life (“EOL”)/End of Service Life (“EOS”) Life-Cycle. Products that have reached their EOL/EOS no longer receive device software updates and security patches and are no longer supported by D-Link.” reads the advisory published by the vendor. “D-Link US recommends that D-Link devices that have reached EOL/EOS be retired and replaced.“
Furthermore, NAS devices should never be exposed to the internet as they are commonly targeted to steal data or encrypt in ransomware attacks.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, NAS)


