
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

D-Link router models affected by remote code execution issue that will not be fixed

Researchers at Fortinet’s FortiGuard Labs have publicly disclosed a critical remote code execution vulnerability affecting some models of D-Link routers.  Security experts at Fortinet’s FortiGuard Labs disclosed a remote code execution vulnerability tracked as CVE-2019-16920. The vulnerability is an unauthenticated command injection issue that was discovered on September 2019. The flaw has received a CVSS v31 base […]

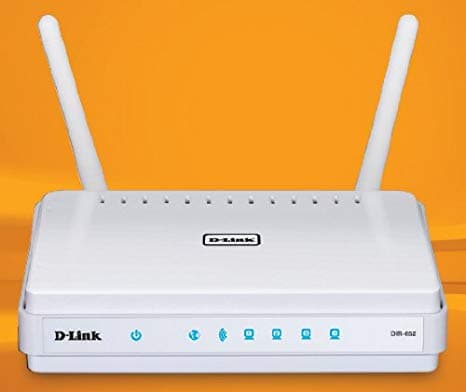
D-Link router

Researchers at Fortinet’s FortiGuard Labs have publicly disclosed a critical remote code execution vulnerability affecting some models of D-Link routers. 

Security experts at Fortinet’s FortiGuard Labs disclosed a remote code execution vulnerability tracked as CVE-2019-16920. The vulnerability is an unauthenticated command injection issue that was discovered on September 2019. The flaw has received a CVSS v31 base score of 9.8 and a CVSS v20 base score of 10.0. 

The bad news for the users is that the vendor will not address it because it affects discontinued products.  

According to the Fortinet, the vulnerability impacts D-Link firmware in the DIR-655, DIR-866L, DIR-652, and DHP-1565 router families.

D-Link router

“In September 2019, Fortinet’s FortiGuard Labs discovered and reported an unauthenticated command injection vulnerability (FG-VD-19-117/CVE-2019-16920) in D-Link products that could lead to Remote Code Execution (RCE) upon successful exploitation. We rated this as a critical issue since the vulnerability can be triggered remotely without authentication.” reads the security advisory published by Fortinet.

The vulnerability could be exploited by an attacker sending arbitrary input to a “PingTest” gateway interface to achieve command injection.

“The vulnerability begins with a bad authentication check. To see the problem in action, we start at the admin page and then perform a login action.” continues the advisory. “Here, we implement the POST HTTP Request to “apply_sec.cgi” with the action ping_test. We then perform the command injection in ping_ipaddr. Even if it returns the login page, the action ping_test is still performed – the value of ping_ipaddr will execute the “echo 1234” command in the router server and then send the result back to our server. “

The experts discovered that it is possible to execute code remotely, even without the necessary privileges, due to bad authentication check.

The researchers reported the vulnerability to D-Link on September 22, the vendor the day after acknowledged the issue, but three days later confirmed that no patch will be released because the products are at End of Life (EOL),

Below the disclosure timeline:

  • 22 September, 2019: FortiGuard Labs reported the vulnerability to D-Link.
  • 23 September, 2019: D-Link confirmed the vulnerability
  • 25 September, 2019: D-Link confirmed these products are EOL
  • 3 October 2019: Public disclosure of the issue and released advisory
[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – routers, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


