
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Chaining three critical vulnerabilities allows takeover of D-Link routers

Researchers from the Silesian University of Technology in Poland discovered several flaws that could be exploited to take over some D-Link routers. A group of researchers from the Silesian University of Technology in Poland has discovered three vulnerabilities in some models of D-Link routers that could be chained to take full control over the devices. The […]

Chaining three critical vulnerabilities allows takeover of D-Link routers

Researchers from the Silesian University of Technology in Poland discovered several flaws that could be exploited to take over some D-Link routers.

A group of researchers from the Silesian University of Technology in Poland has discovered three vulnerabilities in some models of D-Link routers that could be chained to take full control over the devices.

The flaws are a Directory Traversal (CVE-2018-10822), Password stored in plaintext (CVE-2018-10824), and a Shell command injection (CVE-2018-10823).

“I have found multiple vulnerabilities in D-Link router httpd server. These vulnerabilities are present in multiple D-Link types of routers. All three taken together allow to take a full control over the router including code execution.” reads the security advisory.

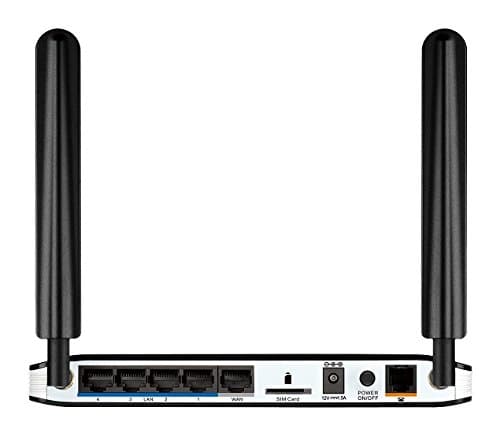
The vulnerabilities reside in the httpd server of some D-Link routers, including DWR-116, DWR-111, DIR-140L, DIR-640L, DWR-512, DWR-712, DWR-912, and DWR-921.

Researchers found a directory traversal vulnerability, tracked as CVE-2018-10822, that could be exploited by remote attackers to read arbitrary files using an HTTP request.

The issue was initially reported to D-Link as CVE-2017-6190, but the vendor did not correctly fix the flaw.

This flaw could be exploited to gain access to a file that stores the admin password for the device in clear text.

The storage of password in clear text is tracked as CVE-2018-10824, to avoid abuses the experts did not reveal the path of the files

Researchers also reported another flaw, tracked as CVE-2018-10823, that could be exploited by an authenticated attacker to execute arbitrary commands and take over the device.

Below a video that shows how the flaws could be chained to takeover a device:

The experts reported the flaws to D-Link in May but the vendor still hasn’t addressed them, then the experts publicly disclosed the vulnerabilities.

Waiting for a patch to address the vulnerabilities, users can make their devices not accessible from the Internet.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – D-Link, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


