
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Dailymotion forces password reset in response to credential stuffing Attack

The popular video sharing website Dailymotion announced that some accounts were accessed by hackers as result of a massive credential stuffing attack. On Friday, the popular video sharing website Dailymotion announced that some accounts were hit by hackers. The company discovered unauthorized access attempts resulting from credential stuffing activity. The company blocked the attempts of intrusions […]

Dailymotion

The popular video sharing website Dailymotion announced that some accounts were accessed by hackers as result of a massive credential stuffing attack.

On Friday, the popular video sharing website Dailymotion announced that some accounts were hit by hackers. The company discovered unauthorized access attempts resulting from credential stuffing activity. The company blocked the attempts of intrusions and notified them to potentially affect users.

“Dailymotion announces being subject to a large-scale computer attack aimed at compromising the data of its users.” reads the press release published by the firm.

“The attack, which was discovered by Dailymotion technical teams and is still ongoing, was successfully contained following the implementation of measures to limit its scope. Potentially impacted users have been contacted directly by dailymotion to inform them and provide them with personalized support.”

The attempts were observed on January 19 and lasted for at least seven days, the company also notified of the attack to the CNIL (French Data Protection Authority).

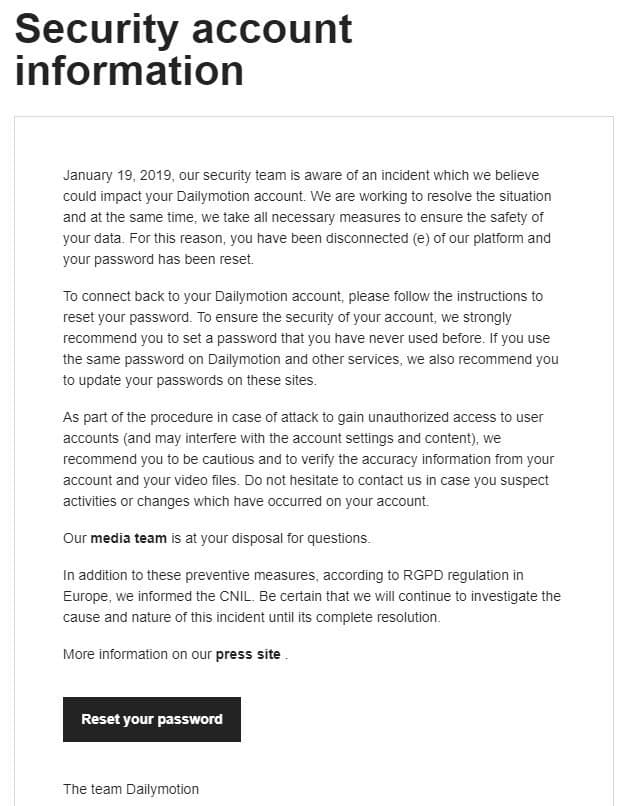
After the discovery of hacking attempts, the French firm logged users out and forced a password reset procedure by including in the notification a link to change the password and re-gain access to the account.

Dailymotion

The company has also informed the French Data Protection Authority (CNIL) of the attack, as required by the European Union General Data Protection Regulation (GDPR).

Dailymotion reported that attackers were trying attempting to take over the accounts via brute force attacks or by using stolen credentials obtained from third-party data breaches.

“The attack consists in “guessing” the passwords of some dailymotion accounts by automatically trying a large number of combinations, or by using passwords that have been previously stolen from web sites unrelated to dailymotion.” continues the company.

The security team announced that it is working to improve the protection of its user data.

Unfortunately, it is quite easy to find huge archives available for sale on the Dark Web and use data they contain to carry out credential stuffing attacks.

Recently the popular cyber security expert Troy Hunt revealed the discovery of Collection #1 archive containing 773 million credentials, the huge dump was offered for just $45.

To prevent credential stuffing attacks, users have to choose a unique password for every online service they use and enable two-factor authentication for the account if possible.

In 2016, Dailymotion suffered a massive data breach that exposed 87 million accounts.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini


Dailymotin (SecurityAffairs – hacking, credential stuffing attacks)

[adrotate banner=”5″] [adrotate banner=”13″]


