
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Dark web Empire Market still down after 3 days. DDoS attack or exit scam?

The dark web marketplace Empire Market has been down for at least 3 days, two of the possible reasons, an exit scam or a prolonged DDoS attack. The popular dark web site Empire Market has been down for at least 60 hours, it hasn’t been down for so long since 2019. The cause is still […]

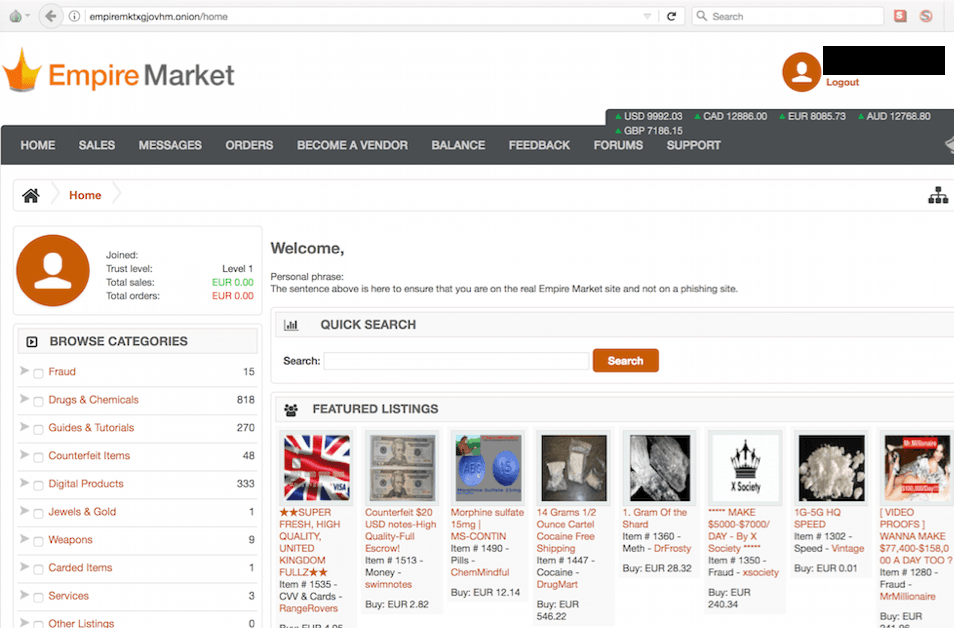
Empire Market

The dark web marketplace Empire Market has been down for at least 3 days, two of the possible reasons, an exit scam or a prolonged DDoS attack.

The popular dark web site Empire Market has been down for at least 60 hours, it hasn’t been down for so long since 2019.

The cause is still unclear, someone blames a prolonged denial-of-service (DDoS) attack, while some users suspect an exit scam.

Empire Market features multiple categories of illicit goods such as illegal drugs, counterfeit items, ftware & Malware, and credit card numbers, it allows its users to pay using Bitcoin (BTC), Monero (XMR), and Litecoin (LTC).

Since August 23, 2020, numerous threads related to the Empire Market outage were posted on the Reddit forum r/darknet and on the deep web discussion forum Dread. According to the website darknetstats.com, the Marketplace was still “down, not working,” on August 25, 2020 (00:26 CET).

A user on Twitter claims the operators of the Empire Market have already transferred tens of millions of dollars in #Bitcoin to #offline wallets in the last few days.

https://twitter.com/PHIL4ACES/status/1297596061666684928

Many users believe that the marketplace was down due to exit scams, this means that all the funds managed by the platform will disappear and that operators will shut down their business.

At the same time, other users exclude this thesis and confirmed that the site is still up intermittently due to a massive DDoS attack.

This isn’t the first time that the Empire Market has been targeted with DDoS attacks, earlier this year it was down due to a series of prolonged DDoS attacks.

The Twitter user DarkDotFail also belives that the root cause of the outage is a massive DDoS attack that made it “very slow to access” the platform.

On Sunday, Dark.fail shared multiple screenshots of a PGP signed message from the moderators of Empire.

One of the top moderators of the Empire Market confirmed the DDoS attack in a threat on the Dread forum.

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, Empire)

[adrotate banner=”5″]

[adrotate banner=”13″]


