
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Darwin kernel, just an IP packet to cause the crash of Apple devices

A serious flaw affecting the Darwin kernel in the Apple OS X 10.10 and iOS 8 could be exploited to cause DoS attack just sending a specific IP packet. At the end of 2014, security experts at Kaspersky Lab discovered a serious vulnerability in the Darwin kernel. The name “Darvin kernel” is unknown to the […]

Darwin kernel, just an IP packet to cause the crash of Apple devices

A serious flaw affecting the Darwin kernel in the Apple OS X 10.10 and iOS 8 could be exploited to cause DoS attack just sending a specific IP packet.

At the end of 2014, security experts at Kaspersky Lab discovered a serious vulnerability in the Darwin kernel. The name “Darvin kernel” is unknown to the majority of the user, but represents an important component for their machines considering that it is an open source component of Apple OS X and iOS.

Every Apple users with OS X 10.10 and iOS 8 is exposed at risk. The Darwin kernel flaw could be exploited to run a DoS (denial of service) attack on vulnerable devices by sending just one incorrect network packet.

“This vulnerability is connected with the processing of an IP packet that has a specific size and invalid IP options. As a result, remote attackers can cause DoS (denial of service) of a device with OS X 10.10 or iOS 8 installed.” is reported by the experts at Kaspersky in a blog post.

The experts explained that there is a flaw in the process of the Darwin kernel that examines IP packet having a specific size and invalid IP options.

Further investigations allowed the researcher to discover that the following devices with 64-bit processors and iOS 8 installed are affected by the Darwin kernel flaw:

  • iPhone 5s and later models
  • iPad Air and later models
  • iPad mini 2 and later models

In presence of the specifically crafted packed the system tries to handle it and generate a new ICMP packet that could not be contained in the new buffer size allocate by the kernel causing the system shut down in emergency mode.

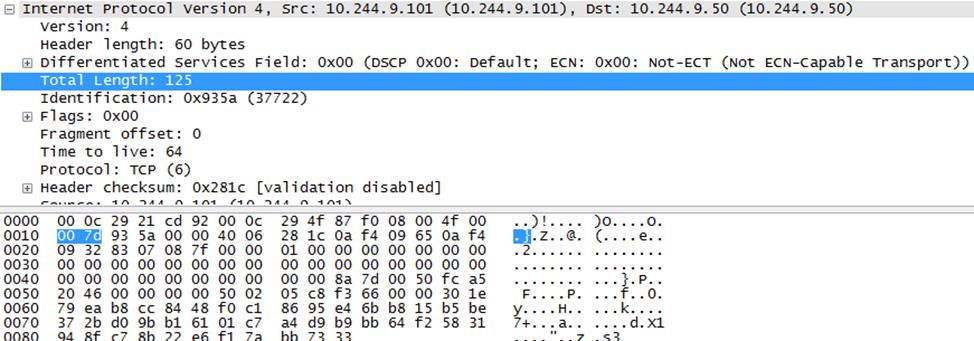
“This happens because the internal kernel structures have been changed and the new buffer size is insufficient to store a newly-generated ICMP packet. To cause this, the IP packet must satisfy the following criteria:

  • The size of the IP header should be 60 bytes.
  • The size of the  IP payload should be at least 65 bytes
  • There should be errors in the IP options (invalid size of option, class, etc.)”

Below an example of packet that can exploit the flaw in the Darwin kernel component:
Darwin Nuke

How to protect your systems?

Simply update the OS of your devices to the last versions OS X 10.10.3 and iOS 8.3.

Pierluigi Paganini

(Security Affairs –  Darwin kernel, hacking)


