
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

inSicurezzaDigitale launches the Dashboard Ransomware Monitor

The cybersecurity blog inSicurezzaDigitale has launched the Italian Dashboard Ransomware Monitor to analyze the principal RaaSs’ activities. Here it comes, inSicurezzaDigitale announced the Dashboard Ransomware Monitor, it is the second project after the recent presentation of the project Mastodon. The Dashboard is very easy to use and it is available via this link: ransom.insicurezzadigitale.com The […]

Ransomware

The cybersecurity blog inSicurezzaDigitale has launched the Italian Dashboard Ransomware Monitor to analyze the principal RaaSs’ activities.

Here it comes, inSicurezzaDigitale announced the Dashboard Ransomware Monitor, it is the second project after the recent presentation of the project Mastodon.

The Dashboard is very easy to use and it is available via this link: ransom.insicurezzadigitale.com

Ransomware

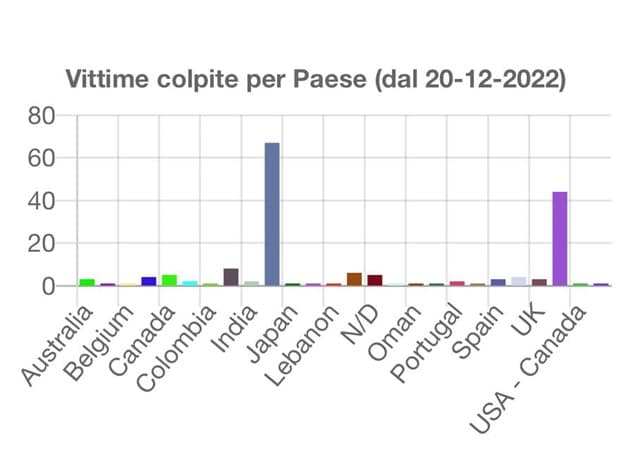
The dashboard is available for free and without any sign-in, it provides an easy-to-query tool that monitors ransomware attacks on a global scale and on a daily bases.

Ransomware

“The strength of this OSINT Italian project, quite unique in its kind, is the chance of following it with a standard, worldwide and easy RSS feed.” explained the development team.

All data collected by the dashboard can be exported in different formats and can be analyzed using useful graphics.

You’ll find more details about the project here (Italian language):

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, ransomware)

[adrotate banner=”5″]

[adrotate banner=”13″]


