
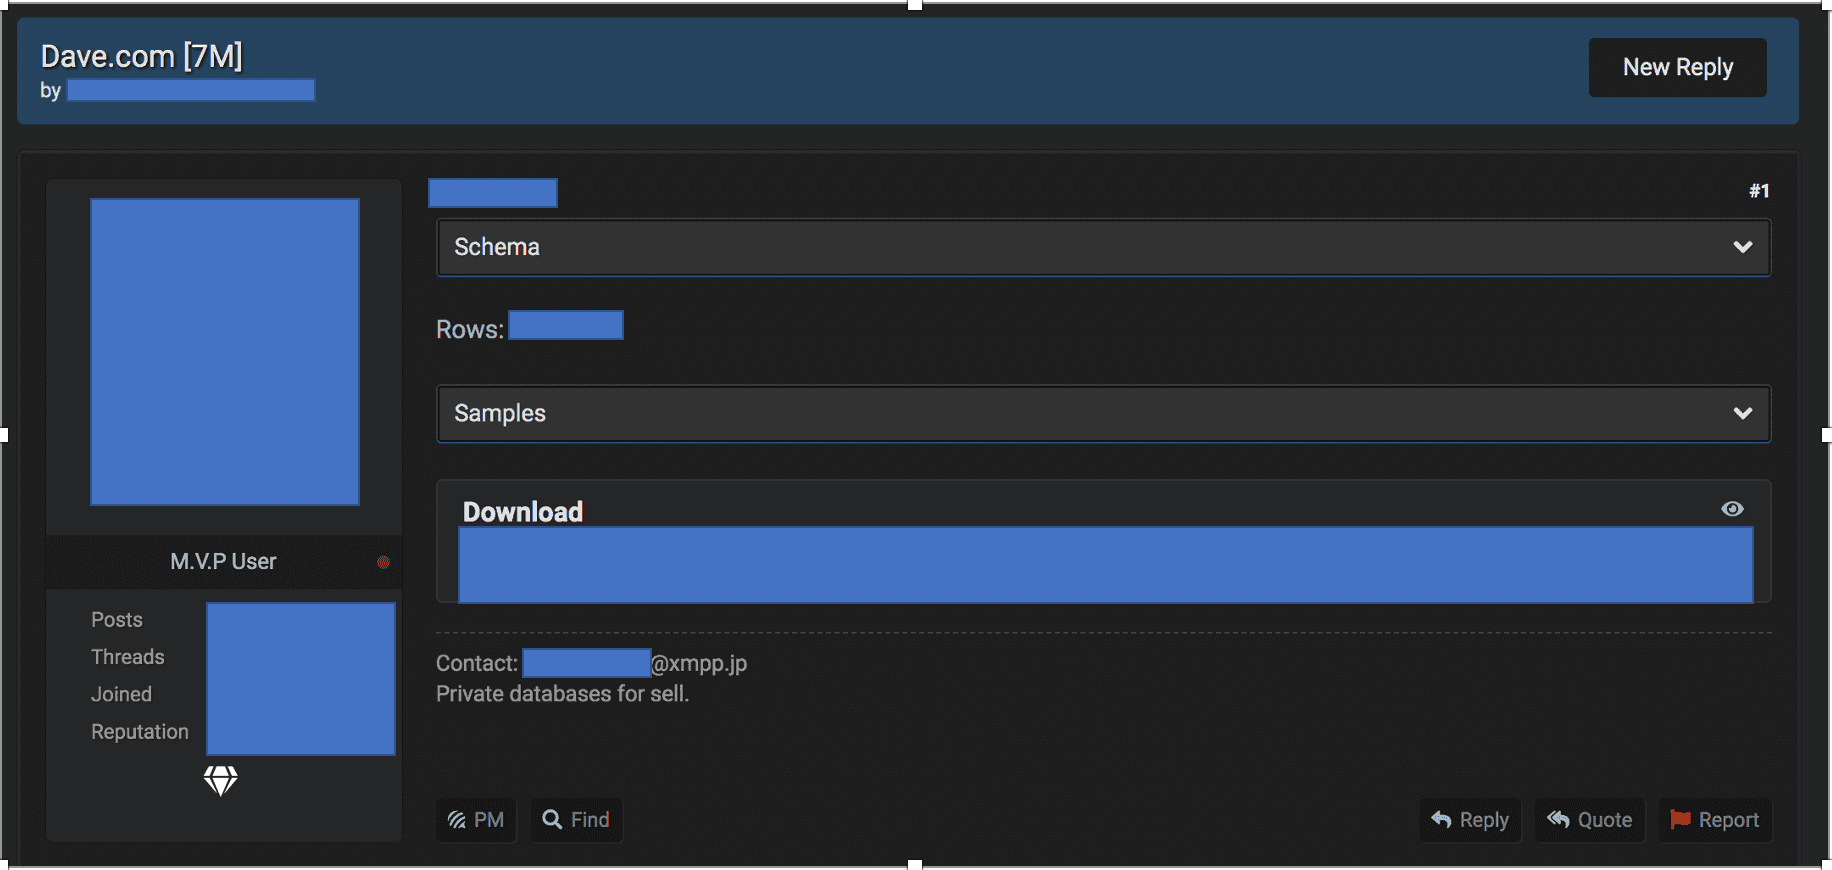
Digital banking app Dave.com discloses a security breach after the known threat actor ShinyHunters leaked 7 million user records on a crime forum.
The popular digital banking app Dave.com discloses a security breach after the known threat actor ShinyHunters leaked 7,516,625 user records on a crime forum.
According to ZDNet, the security breach originated on the network of a former business partner, Waydev.
Dave reported the incident to law enforcement and started an internal investigation of the breach. The company is also aware that a threat actor is attempting to sell the Dave user records in the cybercrime underground, it hired security firm CrowdStrike to investigate the security breach.
Dave is notifying customers of the security breach, it also forced a password reset in response to the incident.
As part of continuous darkweb and deepweb monitoring, researchers at Cyble Research Team identified the known threat actor “ShinyHunters” who leaked 7 million user records Dave.com. The actor initially attempted to sell the huge trove data on an auction, then released it for free,
Cyble became aware of the incident on June 28 and notified Dave on July 2.
“The database was initially on an auction, by the alias ‘hasway’ at the hacking forum exploit, and later was removed on auction. Cyble believes the alias belongs to ShinyHunters.” reported Cyble.
“On July 24, things took an interesting turn when ‘ShinyHunters’ leaked the database of Dave.com and others. The leaked user records have been put up for free.”

The leaked records include:
- User ID
- Phone Number
- Email Address
- Full Name
- Date of Birth
- Residential Address
- Risepay ID
- Synapsepay ID
Unfortunately for some users, leaked data also includes encrypted payment card data and Social Security numbers.
“This database seems to be have dumped through sending Github phishing emails to Dave.com employees. Threat actor appears to have found employee details by searching for developers in the organization on LinkedIn / Crunchbase / Angel online platforms.” continues Cyble.
ShinyHunters made the headlines for selling data of many other organizations, below the complete list published by BleepingComputer:
| Company | User Records | Price |
| Tokopedia | 91 million | $5,000 |
| Homechef | 8 million | $2,500 |
| Bhinneka | 1.2 million | $1,200 |
| Minted | 5 million | $2,500 |
| Styleshare | 6 million | $2,700 |
| Ggumim | 2 million | $1,300 |
| Mindful | 2 million | $1,300 |
| StarTribune | 1 million | $1,100 |
| ChatBooks | 15 million | $3,500 |
| The Chronicle Of Higher Education | 3 million | $1,500 |
| Zoosk | 30 million | $500 |
Dave declared that currently, it is not aware of attacks abusing the stolen data to access user accounts.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Dave)
[adrotate banner=”5″]
[adrotate banner=”13″]


