
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Emsisoft released a free Decrypter for the GetCrypt ransomware

For the second time in a few days, experts at Emsisoft released a free decrypter, this time to help victims of the GetCrypt ransomware. Security experts at Emsisoft released a new decrypted in a few days, it could be used for free by victims of the GetCrypt ransomware to decrypt their files encrypted by the malware. The […]

GetCrypt ransomware

For the second time in a few days, experts at Emsisoft released a free decrypter, this time to help victims of the GetCrypt ransomware.

Security experts at Emsisoft released a new decrypted in a few days, it could be used for free by victims of the GetCrypt ransomware to decrypt their files encrypted by the malware.

The GetCrypt ransomware is served through the RIG exploit kit, it leveragesSalsa20 and RSA-4096 to encrypt the victims’ files.

“GetCrypt is a ransomware spread by the RIG exploit kit, and encrypts victim’s files using Salsa20 and RSA-4096. It appends a random 4-character extension to files that is unique to the victim.” reads the post published by Emsisoft.

The ransomware drops on the infected systems the file “# DECRYPT MY FILES #.txt” containing the follwing ransom note:

“Attention! Your computer has been attacked by virus-encoder! All your files are now encrypted using cryptographycalli strong aslgorithm. Without the original key recovery is impossible.

TO GET YOUR DECODER AND THE ORIGINAL KEY TO DECRYPT YOUR FILES YOU NEED TO EMAIL US AT: GETCRYPT@COCK.LI It is in your interest to respond as soon as possible to ensure the restoration of your files. P.S only in case you do not recive a response from the first email address within 48 hours, [redacted]. It is in your interest to respond as soon as possible to ensure the restoration of your files. 

P.S only in case you do not recive a response from the first email address within 48 hours,
[redacted]
“

Victims can download the decrypter for free at the following URL:

https://www.emsisoft.com/decrypter/download/getcrypt

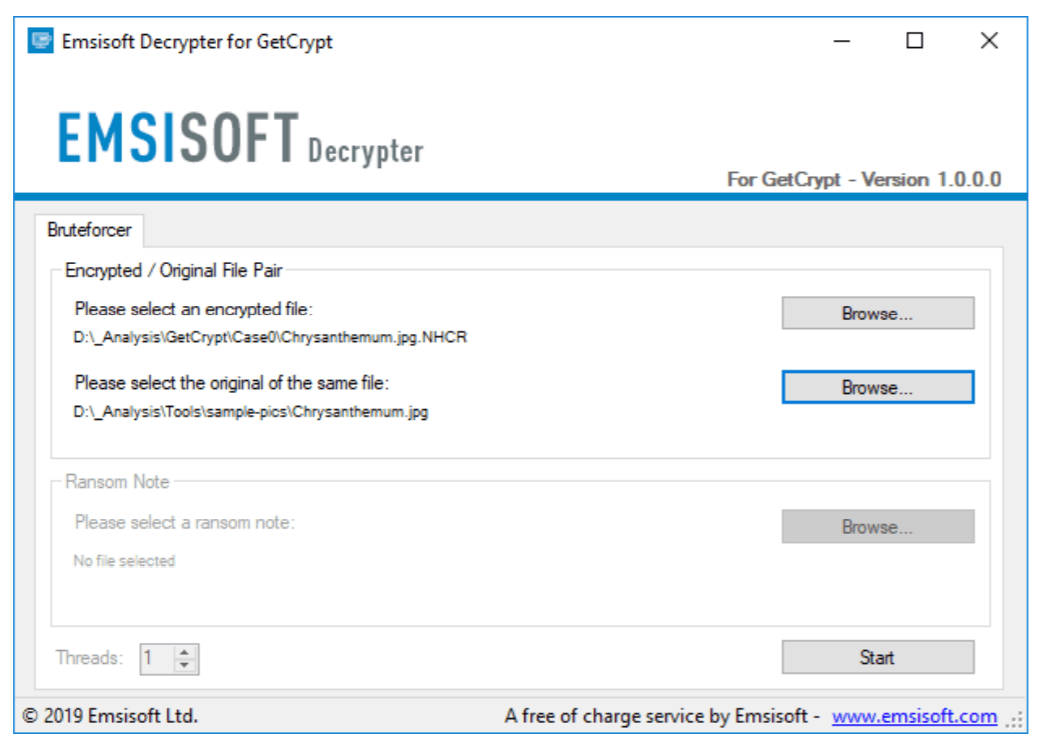
In order to decrypt the files, victims have to provide an encrypted version of a file and the original of the same file.

GetCrypt ransomware

A few days ago, Emsinsoft released a free Decrypter for JSWorm 2.0


If you appreciate my effort in spreading cybersecurity awareness, please vote for Security Affairs in the section “Your Vote for the Best EU Security Tweeter”

Thank you

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – GetCrypt ransomware, cybercrime)

[adrotate banner=”5″]

[adrotate banner=”13″]


