
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

DitM Dog In The Middle – New Hacking Technique to Eavesdropping

During Defcon 25 hacking conference held in Las Vegas on July, a new eavesdropping attack technique was introduced, it was dubbed DitM (Dog In The Middle). During Defcon 25 one of the biggest information security event that took place in Las Vegas on July 27-30 this year, a new eavesdropping attack technique was introduced. At […]

DitM Dog In The Middle – New Hacking Technique to Eavesdropping

During Defcon 25 hacking conference held in Las Vegas on July, a new eavesdropping attack technique was introduced, it was dubbed DitM (Dog In The Middle).

During Defcon 25 one of the biggest information security event that took place in Las Vegas on July 27-30 this year, a new eavesdropping attack technique was introduced.

At the BioHacking Village’s Pisa Room, the Brazilian information security researcher and senior security consultant at CIPHER, Rafael Fontes Souza presented a proof-of-concept demonstrating a new exploitation technique that can be used to hack user credentials and to intercept sensitive data.

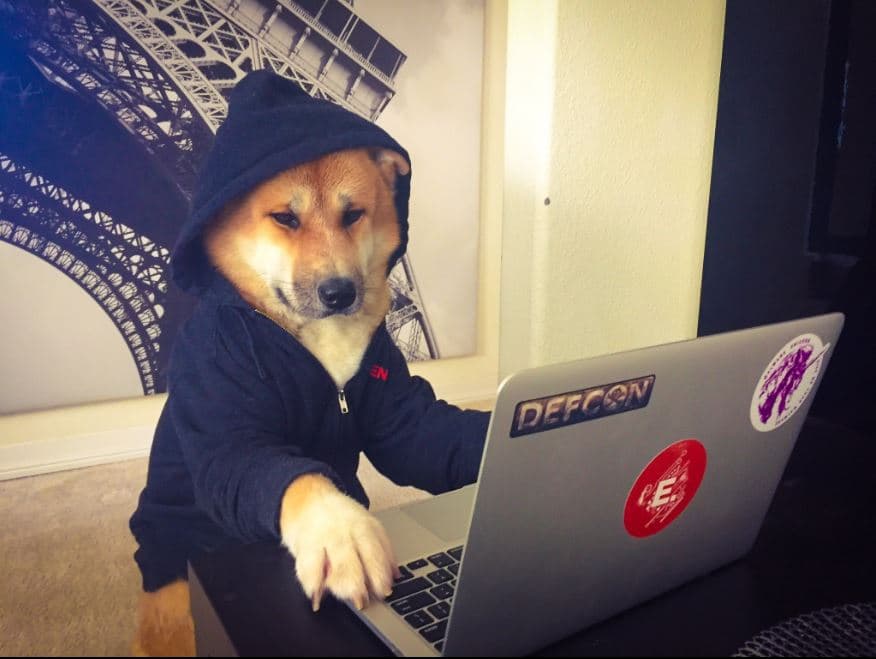
The ‘Dog in the Middle’ technique, aka DitM, used man’s best friend as an attack tool. Rafael adapted a chest collar to carry a mobile phone and wireless network adapter.

DitM

The most noticeable feature of this technique is that the attack vectors are triggered automatically without any human interaction and include near field attacks such as fake access point, cellular base stations or local user attacks on a network.

A comprehensive set of exploitations can be implemented using DitM, like DNS hijacking, packet injection, evil twin, rogue router or ISP, among others.

How that’s done?

The targeted device will connect to a rogue wi-fi access point generated by the dog collar and clever DHCP configurations can push rules to allow IP allocation by the fake AP and traffic forwarding to fake and/or malicious websites.

“Information and user data can be easily stored and malicious files can also be injected remotely to control the compromised device”, explain Rafael.

DitM


The video demonstrating how the chest collar was assembled can be seen at Vimeo through the following link https://vimeo.com/227596613

and Rafael’s presentation can also be accessed through Slideshare here https://pt.slideshare.net/rafa_el_souza/my-dog-is-a-hacker-and-will-still-your-data.

This technique is as very good example of how rather conventional technology can be used to social engineering to compromise users. Who’d think man’s best friend could be used as an attack tool?

Article by Pedro Silveira (Marketing Director at Cipher)

[adrotate banner=”9″] [adrotate banner=”12″]

Edited by Pierluigi Paganini

(Security Affairs – DiTM, hacking)

[adrotate banner=”13″]


