
Security Affairs
CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

DHS announces security measures for critical pipeline industry

The US Department of Homeland Security (DHS) has announced new cybersecurity requirements for critical pipeline owners and operators. The Colonial pipeline incident continues to have a serious impact on the critical infrastructure sector. The US Department of Homeland Security (DHS) has announced new cybersecurity requirements for owners and operators of critical pipelines. The new security directive requires critical […]

darkside US Colonial Pipeline

The US Department of Homeland Security (DHS) has announced new cybersecurity requirements for critical pipeline owners and operators.

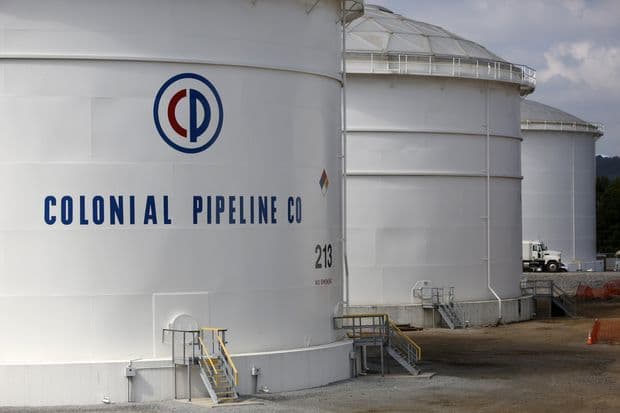
The Colonial pipeline incident continues to have a serious impact on the critical infrastructure sector. The US Department of Homeland Security (DHS) has announced new cybersecurity requirements for owners and operators of critical pipelines.

The new security directive requires critical pipeline owners and operators to report any confirmed and potential cybersecurity incidents to the Cybersecurity and Infrastructure Security Agency (CISA).

“The cybersecurity landscape is constantly evolving and we must adapt to address new and emerging threats,” said Secretary of Homeland Security Alejandro N. Mayorkas.  “The recent ransomware attack on a major petroleum pipeline demonstrates that the cybersecurity of pipeline systems is critical to our homeland security.” reads the announcement published by the “DHS will continue to work closely with our private sector partners to support their operations and increase the resilience of our nation’s critical infrastructure.”

The Security Directive will also require critical pipeline owners and operators to review their current practices, identify cyber-related risks and implement remediation measures. DHS also required them to report the results to Transportation Security Administration (TSA) and CISA within 30 days.

DHS urges infrastructure to designate a Cybersecurity Coordinator, who has to be available 24 hours a day.

TSA is also considering follow-on mandatory measures to enhance the level of cybersecurity of the industry and strengthen the partnership between public and private operators.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, pipeline)

[adrotate banner=”5″]

[adrotate banner=”13″]


