
Threat actors are targeting VoIP servers by exploiting a vulnerability in Digium’s software to install a web shell, Palo Alto Networks warns.
Recently, Unit 42 researchers spotted a campaign targeting the Elastix system used in Digium phones since December 2021. Threat actors exploited a vulnerability, tracked as CVE-2021-45461 (CVSS score 9.8), in the Rest Phone Apps (restapps) module to implant a web shell on VoIP servers. The attackers used the web shell to exfiltrate data by dropping additional payloads inside the target’s Digium phone software.
“As of this writing, we have witnessed more than 500,000 unique malware samples of this family over the period spanning from late December 2021 till the end of March 2022. The malware installs multilayer obfuscated PHP backdoors to the web server’s file system, downloads new payloads for execution and schedules recurring tasks to re-infect the host system.” reads the advisory published by Palo Alto Networks Unit 42. “Moreover, the malware implants a random junk string to each malware download in an attempt to evade signature defenses based on indicators of compromise (IoCs).”
The researchers observed a high volume of malicious traffic likely originating from more than 500,000 unique samples over the period spanning from mid-December 2021 till the end of March 2022. The traffic targets Digium open source Asterisk communication software for VoIP phone devices.
The malicious campaign has many similarities to the INJ3CTOR3 report detailed by Check Point Research in 2020 two years ago, experts speculate it could be a resurgence of this campaign
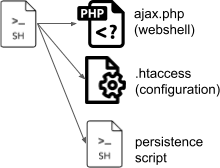
The attack chains start with a code retrieving a shell script dropper from a remote server, which, in turn, downloads and executes obfuscated PHP backdoor in multiple locations in the file system.

The PHP backdoor also creates several root user accounts and set up a scheduled task to maintain the persistence and re-infect the host system.
The malware supports arbitrary commands via the cmd request parameter along with built-in default commands that can allow operators to carry out malicious activities,
“The strategy of implanting web shells in vulnerable servers is not a new tactic for malicious actors. The only way to catch advanced intrusions is a defense-in-depth strategy. Only by orchestrating multiple security appliances and applications in a single pane can defenders detect these attacks.” concludes the report.
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Digium Phones)
[adrotate banner=”5″]
[adrotate banner=”13″]


