
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Satellite TV giant Dish admitted that the recent outage was caused by a ransomware attack

Satellite TV giant Dish Network has confirmed that the recent outage was caused by a ransomware attack, it also disclosed a data breach. Satellite TV giant Dish Network finally admitted that the recent outage was caused by a ransomware attack. The American satellite broadcast provider went offline on February 24, 2023, the outage impacted Dish.com, […]

Dish

Satellite TV giant Dish Network has confirmed that the recent outage was caused by a ransomware attack, it also disclosed a data breach.

Satellite TV giant Dish Network finally admitted that the recent outage was caused by a ransomware attack.

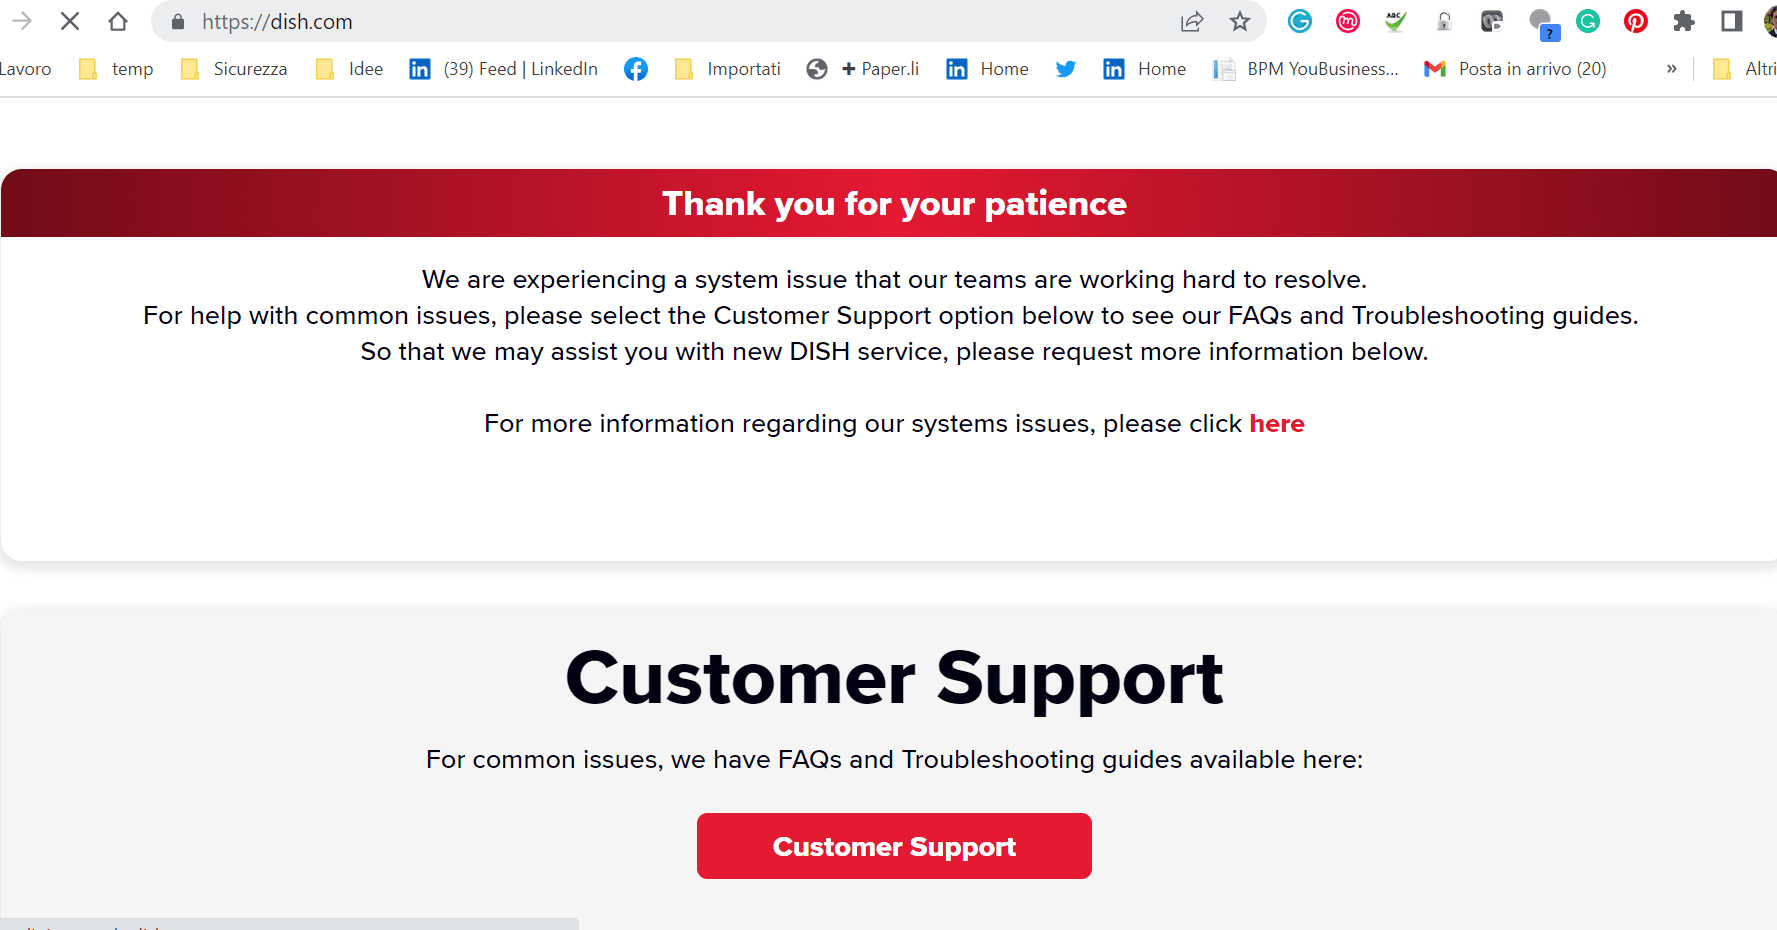
The American satellite broadcast provider went offline on February 24, 2023, the outage impacted Dish.com, Dish Anywhere app, and many other services owned by the company.

Dish

The company initially did not comment on rumors of a ransomware attack, but now it has confirmed the incident and disclosed a data breach.

According to a Form 8-K filed by the company with US Securities and Exchange Commission (SEC), the Corporation has determined that the outage was due to a ransomware attack.

The company immediately launched an investigation into the incident, which is still ongoing, and notified law enforcement authorities.

“On February 23, 2023, DISH Network Corporation (the “Corporation”) announced on its earnings call that the Corporation had experienced a network outage that affected internal servers and IT telephony. The Corporation immediately activated its incident response and business continuity plans designed to contain, assess and remediate the situation. The services of cyber-security experts and outside advisors were retained to assist in the evaluation of the situation. The Corporation has determined that the outage was due to a cyber-security incident and notified appropriate law enforcement authorities.” reads the Form 8-K. “On February 27, 2023, the Corporation became aware that certain data was extracted from the Corporation’s IT systems as part of this incident. It is possible the investigation will reveal that the extracted data includes personal information.”

At the time of this writing the company has yes to disclose the family of ransomware that infected its infrastructure.

According to BleepingComputer, the company was a victim of the Black Basta ransomware operation.

The threat actors initially compromised the company’s Windows domain controllers and then encrypted the VMware ESXi servers and backups.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Dish)


