
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Tens of thousands of misconfigured Django apps leak sensitive data

The security researcher Fábio Castro discovered tens of thousands of Django apps that expose sensitive data because developers forget to disable the debug mode. Security researchers have discovered misconfigured Django applications that are exposing sensitive information, including passwords, API keys, or AWS access tokens. Django is a very popular high-level Python Web framework that allows rapid development of Python-based web applications. The […]

Tens of thousands of misconfigured Django apps leak sensitive data

The security researcher Fábio Castro discovered tens of thousands of Django apps that expose sensitive data because developers forget to disable the debug mode.

Security researchers have discovered misconfigured Django applications that are exposing sensitive information, including passwords, API keys, or AWS access tokens.

Django is a very popular high-level Python Web framework that allows rapid development of Python-based web applications.

The researcher Fábio Castro explained that installs expose data because developers forget to disable the debug mode for the Django app.

https://twitter.com/6IX7ine/status/978598496658960384

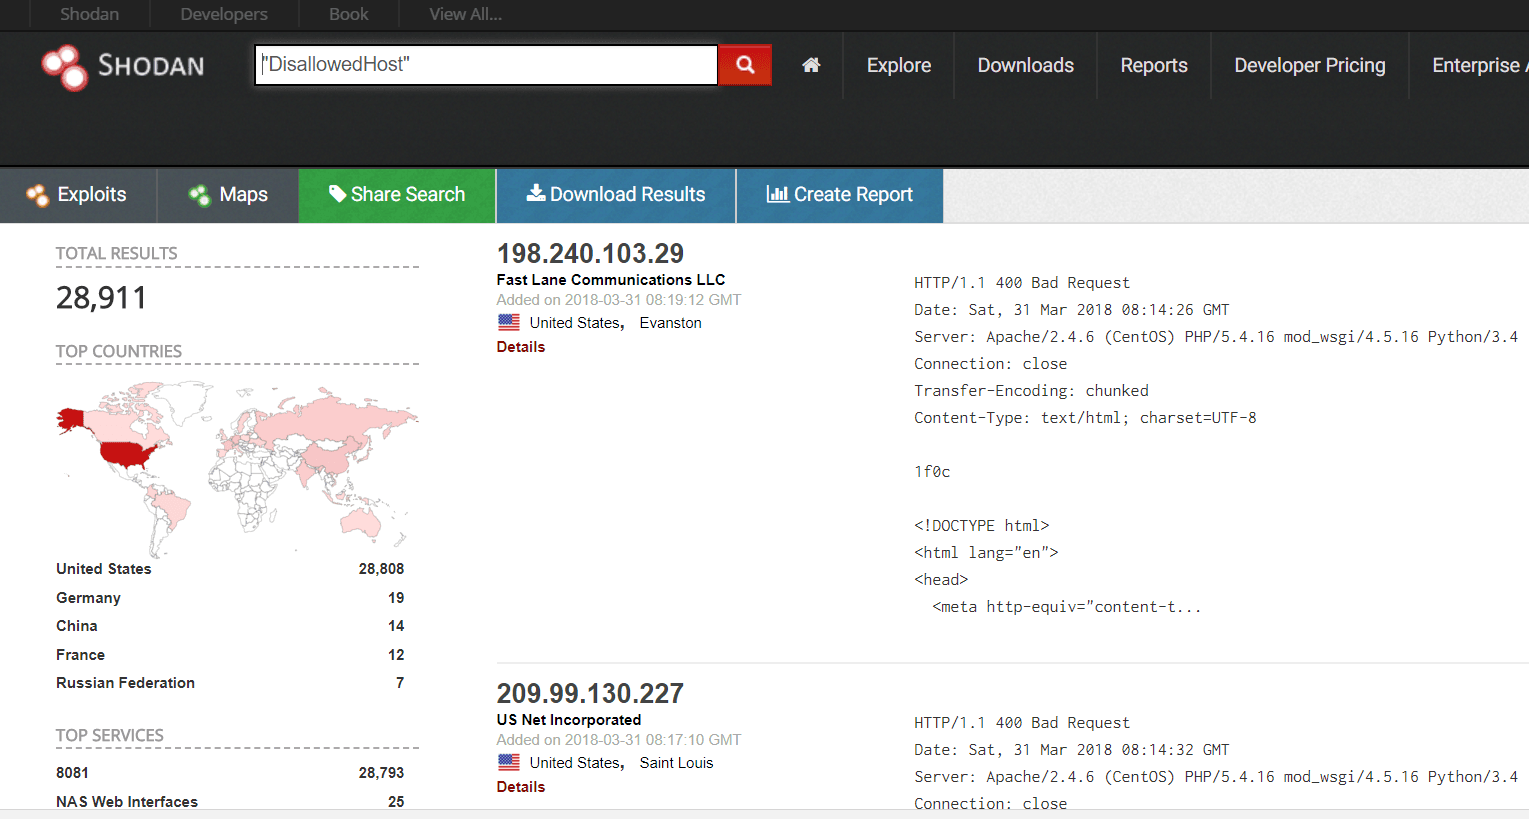
Castro found 28,165 apps querying Shodan for Django installs that have debug mode enabled.

I made the same query a few hours later and I obtained 28,911 results.

Django apps

Many servers with debug mode enabled expose very, the experts discovered server passwords and AWS access tokens that could be used by hackers to gain full control of the systems.

“I found this as I was working with the Django framework on a small project,” Castro told Bleeping Computer  “I noticed some error exception and then went searching on Shodan.”

“The main reason [for all the exposures] is the debug mode enabled,” Castro says. “This is not a failure from Django’s side. My recommendation is to disable debugging mode when deploying the application to production.”

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – Django framework, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


