
Qakbot malware operators are using the Windows Calculator to side-load the malicious payload on target systems.
Security expert ProxyLife and Cyble researchers recently uncovered a Qakbot campaign that was leveraging the Windows 7 Calculator app for DLL side-loading attacks. Dynamic-link library (DLL) side-loading is an attack method that takes advantage of how Microsoft Windows applications handle DLL files. In such attacks, malware places a spoofed malicious DLL file in a Windows’ WinSxS directory so that the operating system loads it instead of the legitimate file
According to the researcher, the operators are using this technique since at least July 11.
Qakbot, also known as QBot, QuackBot and Pinkslipbot, is an info-stealing malware that has been active since 2008. The malware spreads via malspam campaigns, it inserts replies in active email threads.
Cyble experts, who started their investigation from the IoCs shared by ProxyLife, analyzed the attack chain employed in the latest Qakbot attacks.
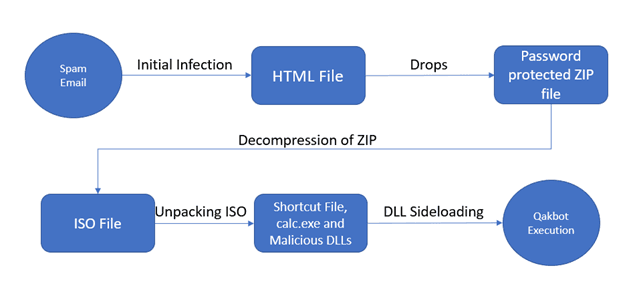
In this campaign, the spam message contains an HTML file that has base64 encoded images and a password-protected ZIP file. The password-protected zip file contains an ISO file (i.e. Report Jul 14 47787.iso), and the password for opening it is reported in the HTML file. The use of password-protected zip file is a common technique adopted by threat actors to evade detection.
Once clicked the image file, it is mounted and shows a .lnk file masquerading as a PDF file. If the victim opens the .lnk file, the Qakbot infection process starts.

The ISO file contains four different files:
- a .lnk file
- a legitimate calc .exe
- WindowsCodecs.dll
- 7533.dll.
The .LNK file appears as a PDF containing information of interest for the victims. The shortcut points to the Calculator app in Windows. Upon executing the Windows 7 Calculator, it will automatically attempt to load the legitimate WindowsCodecs DLL file. The code will load any DLL with the same name if placed in the same folder as the Calc.exe executable resulting in the execution of a malicious DLL.
“In this case, the application is calc.exe, and the malicious file named WindowsCodecs.dll masquerades as a support file for calc.exe.” reads the analysis published by Cyble. “Upon executing the calc.exe, it further loads WindowsCodec.dll and executes the final Qakbot payload using regsvr32.exe. The final payload injects its malicious code into explorer.exe and performs all the malicious activities.”
The threat actors bundle the Windows 7 version of the DLL because the attack doesn’t work against Windows 10 Calc.exe and later.
Cyber shared MITRE ATT&CK® Techniques and Indicators of Compromise (IoCs).
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, malware)
[adrotate banner=”5″]
[adrotate banner=”13″]


