
Researchers linked the threat actor DoNot Team to a new Android malware that was employed in highly targeted cyber attacks.
CYFIRMA researchers linked a recently discovered Android malware to the Indian APT group known as DoNot Team.
The Donot Team (aka APT-C-35 and Origami Elephant) has been active since 2016, it focuses on government and military organizations, ministries of foreign affairs, and embassies in India, Pakistan, Sri Lanka, Bangladesh, and other South Asian countries.
The malware was named “Tanzeem” and “Tanzeem Update” (meaning “organization” in Urdu), CYFIRMA spotted the malware in October and December 2024 respectively. The two artifacts share the same code, with minor differences in the user interface.
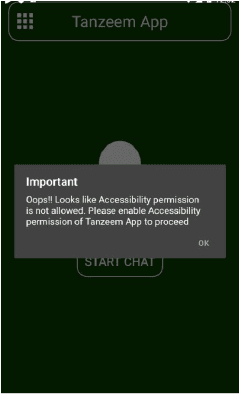
The Tanzeem App mimics chat functionality and prompts users to enable accessibility access. Variants show minor differences, like color changes.
The DoNot APT group has been observed misusing the OneSignal platform, which typically provides tools for sending push notifications, in-app messages, emails, and SMS widely used in mobile and web applications. In this case, the group is leveraging OneSignal to deliver phishing links through notifications. This tactic represents a new development in the group’s methods, as it’s the first time they’ve been seen utilizing OneSignal for such purposes.
The app shuts down after gaining permissions, its name implies targeting specific individuals or groups domestically and abroad.
Upon clicking “START CHAT”, a pop-up message asks the user to turn on accessibility access for the Tanzeem App.” reads the report published by CYFIRMA. “The user is then directed to the accessibility settings page.”

The app can gather call logs, contacts, SMS messages, precise locations, account information, and files stored in external storage. The malicious code can also record the screen.
The DONOT APT targets South Asian organizations for India’s strategic intelligence, using push notifications to install persistent Android malware, signifying evolving tactics and ongoing operations.
“The cybersecurity community is well aware that the DONOT group is actively targeting organizations and individuals across the South Asia region. The group persistently employs similar techniques in their Android malware.” concludes the report, which includes Indicators of Compromise (IoCs). “Recently, we observed the implementation of OneSignal in their latest attack, further demonstrating their efforts to maintain persistence. As the group continues to evolve, we can expect further modifications in their tactics, aiming to strengthen their ability to maintain persistence in future cyberattacks using Android malware.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, malware)


