
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

DoorDash data breach exposes personal info after social engineering attack

DoorDash says a social engineering attack led to a data breach exposing names, addresses, emails, and phone numbers of users, Dashers, and merchants. U.S.-based food delivery and logistics company DoorDash announced that a social engineering attack led to a data breach. “Our team recently identified and shut down a cybersecurity incident that involved an unauthorized […]

DoorDash data breach

DoorDash says a social engineering attack led to a data breach exposing names, addresses, emails, and phone numbers of users, Dashers, and merchants.

U.S.-based food delivery and logistics company DoorDash announced that a social engineering attack led to a data breach.

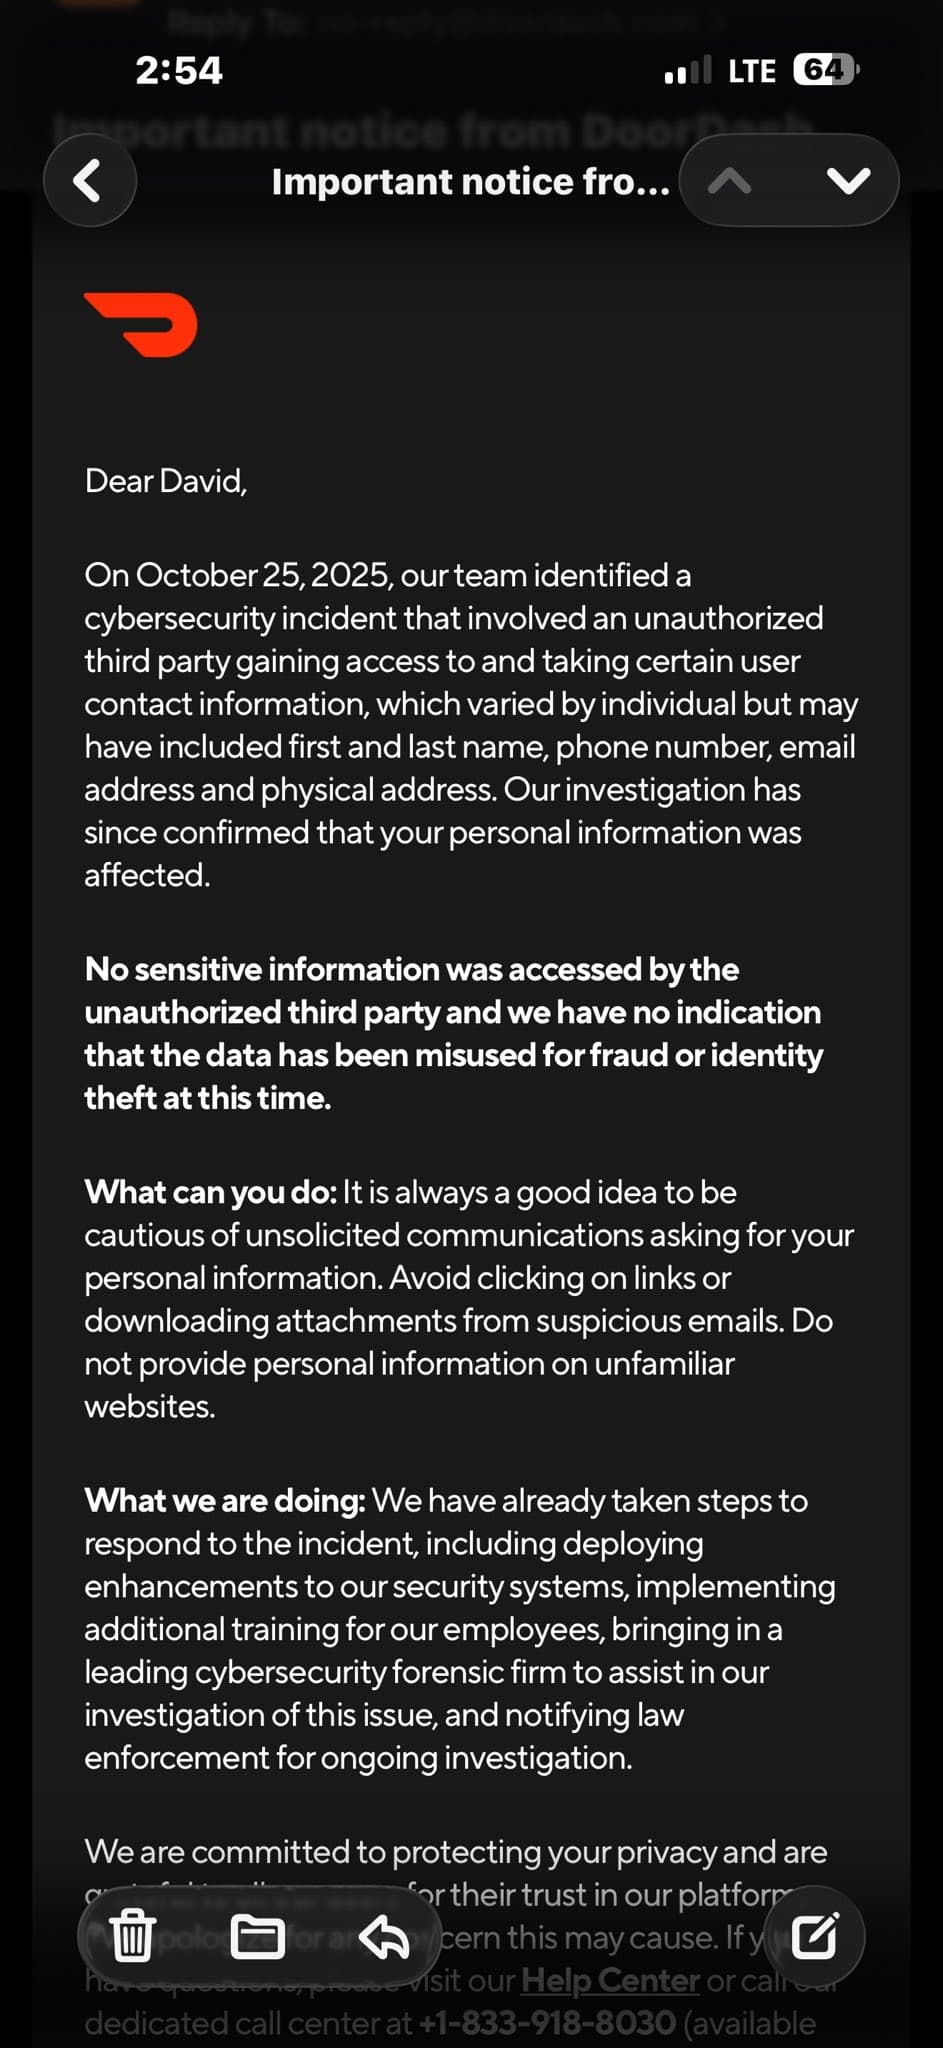
“Our team recently identified and shut down a cybersecurity incident that involved an unauthorized third party gaining access to and taking certain user information.” reads a statement published by the company on the cybersecurity incident. “Importantly, no sensitive information was accessed by the unauthorized third party and we have no indication the data has been misused for fraud or identity theft at this time.”

The company confirmed that one of its employees fell victim to a social engineering scam, but it cut off the intruder’s access and alerted law enforcement. Exposed data include names, addresses, emails, and phone numbers of users, Dashers, and merchants.

“DoorDash employee was recently targeted in a social engineering scam. The response team identified the incident, shut down the unauthorized party’s access, started an investigation, and referred the matter to law enforcement.” continues the statement.

The company pointed out that no sensitive data like SSNs, IDs, driver’s licenses, or bank/payment details was accessed.

DoorDash says there’s no evidence the stolen data has been misused, the company also confirmed that Wolt and Deliveroo customers were not affected.

The U.S.-based food delivery and logistics company notified impacted users.

DoorDash data breach

At this time it is unclear the scope of the data breach and the number of impacted individuals.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, DoorDash)


