
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Hackers compromised thousands of Windows boxes using leaked NSA hack tools DOUBLEPULSAR and ETERNALBLUE

Security researcher warn of hackers compromised thousands of Windows boxes using leaked NSA hack tools DOUBLEPULSAR and ETERNALBLUE Security expert Dan Tentler, the founder of security shop Phobos Group, has observed a significant increase in the number of Windows boxes exposed on the Internet that has been hacked with DOUBLEPULSAR backdoor. The compromised windows boxes have been used […]

DOUBLEPULSAR hack

Security researcher warn of hackers compromised thousands of Windows boxes using leaked NSA hack tools DOUBLEPULSAR and ETERNALBLUE

Security expert Dan Tentler, the founder of security shop Phobos Group, has observed a significant increase in the number of Windows boxes exposed on the Internet that has been hacked with DOUBLEPULSAR backdoor. The compromised windows boxes have been used for several criminal purposes such as delivering malware or used in spam campaigns.

The DOUBLEPULSAR backdoor allows attackers to inject and execute malicious code on a target system, it is installed by leveraging the ETERNALBLUE, an SMBv1 (Server Message Block 1.0) exploit that could trigger an RCE in older versions of Windows (Windows XP to Server 2008 R2).

Every Window machine running an old vulnerable version that exposes an SMB service is at risk of hack.

The DOUBLEPULSAR and ETERNALBLUE are now available for anyone after the archive of NSA tools was leaked online.

Recently Microsoft patched the SMB Server vulnerability (MS17-010) exploited by ETERNALBLUE, the security updates were released for Windows Vista SP2, Windows 7, Windows 8.1, Windows RT 8.1, Windows 10, Windows Server 2008 SP2, Windows Server 2008 R2 SP1, Windows Server 2012 and Windows Server 2012 R2, Windows Server 2016, and Server Core.

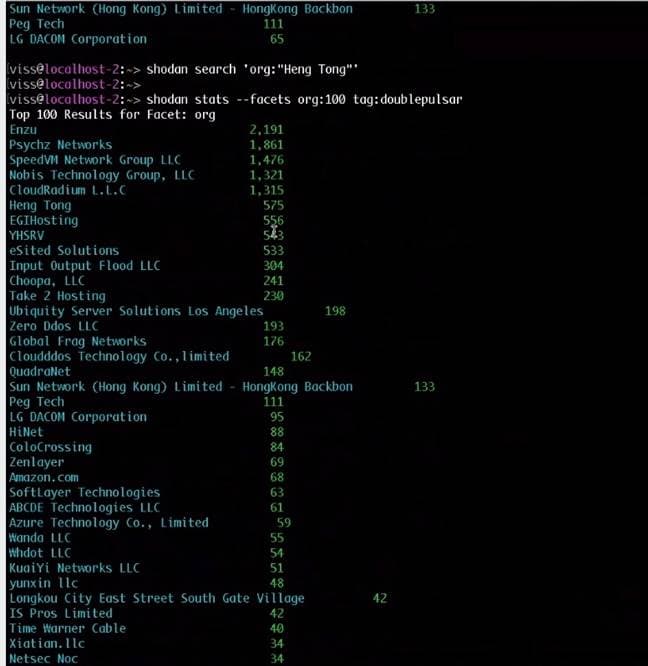
According to Tentler, who scanned the Internet for vulnerable Windows boxes, 15,196 systems have been already compromised, most of them in the US.

The expert also observed that the number of infections continues to increase.

Windows boxes compromised with the DOUBLEPULSAR implant could be easily identified observing the response to a special ping to port 445.

DOUBLEPULSAR hack

“I’m hopeful this is the wakeup moment for people over patching Windows machines.” said Tentler.

According to Tentler on Easter weekend, script kiddies worldwide launched a massive attack leveraging the DOUBLEPULSAR exploit.

The experts have no doubt, the number of DOUBLEPULSAR attacks could continue to increase in the coming week.

Patch your system now!

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – DOUBLEPULSAR , NSA)

[adrotate banner=”13″]


