Security Affairs
The School Bomb Threats Came From Accounts Already in Stolen Data|Microsoft Cloud Outage Hits Outlook, Teams, Copilot and AI Services|Predator, Pegasus and Graphite: Governments Accused of Spyware Abuse Face Little Accountability|Zoom Fixes Critical Windows Vulnerability Allowing Privilege Escalation|Poland takes its national e-government platform offline after a cyberattack|AI Pentest Tool AntiFox Abused To Steal AWS Credentials|WhiteArmor Demands $5 Million from Maersk, Claims Theft of 100GB of Data|Hackers Advertise a $1,000 Gmail Tool That Allegedly Survives Password Resets|Microsoft November Patch Tuesday: one exploited Outlook bug and 30 wormable flaws|U.S. CISA adds IBM, SignalWire FreeSwitch, OpenSSH, and GPUStack flaws to its Known Exploited Vulnerabilities catalog|Russia-Linked APT Turla Turned Exchange Servers Into Their Own Control Room|iOS Sandbox Escape Is Public, and Apple Hasn’t Confirmed a Fix|The School Bomb Threats Came From Accounts Already in Stolen Data|Microsoft Cloud Outage Hits Outlook, Teams, Copilot and AI Services|Predator, Pegasus and Graphite: Governments Accused of Spyware Abuse Face Little Accountability|Zoom Fixes Critical Windows Vulnerability Allowing Privilege Escalation|Poland takes its national e-government platform offline after a cyberattack|AI Pentest Tool AntiFox Abused To Steal AWS Credentials|WhiteArmor Demands $5 Million from Maersk, Claims Theft of 100GB of Data|Hackers Advertise a $1,000 Gmail Tool That Allegedly Survives Password Resets|Microsoft November Patch Tuesday: one exploited Outlook bug and 30 wormable flaws|U.S. CISA adds IBM, SignalWire FreeSwitch, OpenSSH, and GPUStack flaws to its Known Exploited Vulnerabilities catalog|Russia-Linked APT Turla Turned Exchange Servers Into Their Own Control Room|iOS Sandbox Escape Is Public, and Apple Hasn’t Confirmed a Fix|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Major Australian ports blocked after a cyber attack on DP World

A cyber attack on the logistics giant DP World caused significant disruptions in the operations of several major Australian ports. A cyberattack hit the international logistics firm DP World Australia and disrupted the operations in major Australian ports. DP World is a global leader in logistics, providing comprehensive supply chain solutions to the world’s largest shipping […]

port

Source: Porttechnology.org

A cyber attack on the logistics giant DP World caused significant disruptions in the operations of several major Australian ports.

A cyberattack hit the international logistics firm DP World Australia and disrupted the operations in major Australian ports.

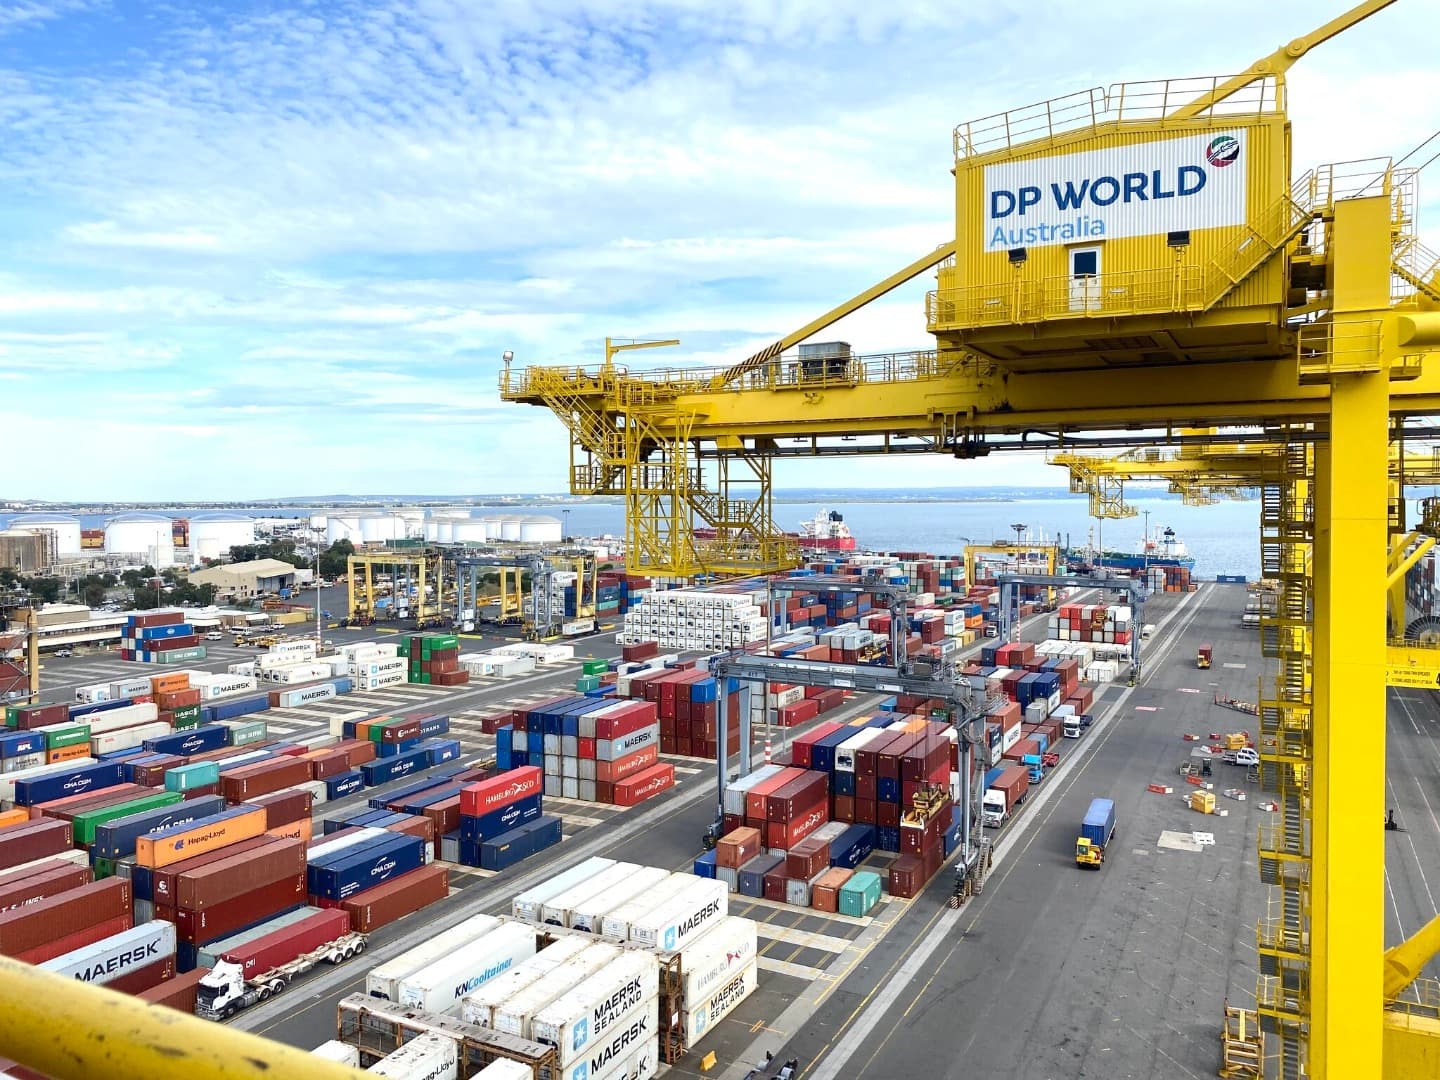
DP World is a global leader in logistics, providing comprehensive supply chain solutions to the world’s largest shipping lines, multinational companies and governments. The company’s core business is the operation of marine terminals, which it does through a network of over 80 terminals across 6 continents. DP World also provides a range of other logistics services, including freight forwarding, warehousing, and distribution.

DP World Australia
Source: Porttechnology.org

The company notified law enforcement and advised the Australian Government that the interruptions would impact the ports for a number of days, rather than weeks. The Australian Federal Police is investigating the security incident.

The company was forced to disconnect its systems from the internet and interrupted operations at ports in Sydney, Melbourne, Fremantle and Brisbane. 

According to the Sydney Morning Herald, the attack had blocked an estimated 30,000 shipping containers across DP World’s yards nationally.

“The ongoing investigation and response to protect networks and systems may cause some necessary, temporary disruptions to their services in the coming days,” a DP World spokesman told the newspaper.

“This is a part of an investigation process and resuming normal logistical operations at this scale.”

The procedure adopted in response to the incident suggests that DP World may have suffered a ransomware attack, but local media learned from people informed of the incident that it was not a ransomware attack. 

The company did not share details about the attack, rumors speculate the company was the victim of a ransomware group that exploited a recently disclosed Citrix Netscaler vulnerability codenamed ‘Citrix Bleed. According to some experts, including the popular cyber security researcher Kevin Beaumont, multiple threat actors are currently exploiting this vulnerability to gain initial access to the victims’ networks.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, DP World)