
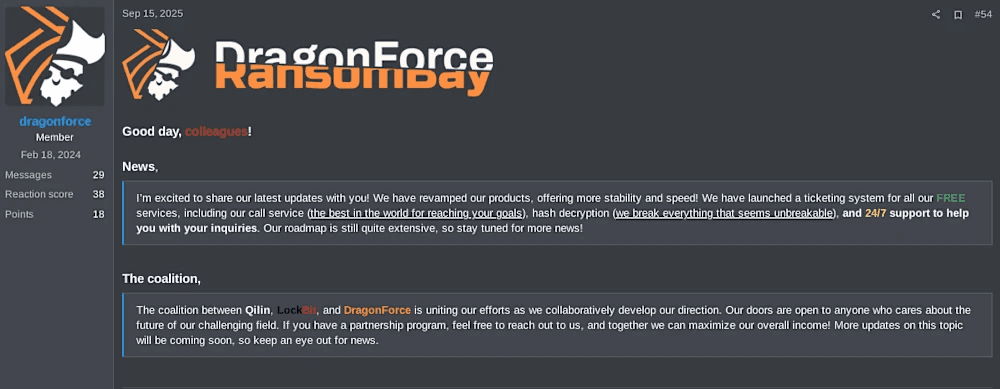
DragonForce, LockBit, and Qilin formed a ransomware alliance to boost attack effectiveness, marking a major shift in the cyber threat landscape.
Ransomware groups DragonForce, LockBit, and Qilin formed a strategic alliance to enhance their attack capabilities, signaling an evolving cyber threat landscape.
The alliance aims at sharing tools and infrastructure to enhance attack effectiveness. The coalition may restore LockBit’s reputation post-takedown and lead to more frequent ransomware attacks, including on critical infrastructure, echoing past collaborations like the 2020 Maze-LockBit partnership that popularized double extortion tactics.
“This quarter, the newly returned LockBit formed a coalition with prominent RaaS groups DragonForce and Qilin, a partnership poised to drive more frequent and effective ransomware attacks.” reads the report published ReliaQuest. “This alliance could help restore LockBit’s reputation among affiliates following last year’s takedown, potentially triggering a surge in attacks on critical infrastructure and expanding the threat to sectors previously considered low risk.”

In Q3 2025, Qilin hit a record number of victims, fueled by organized, business-like operations and dark web recruiting. The group partners with IABs for VPN access, enabling fast, stealthy attacks. Akira, Inc Ransom, and Play also remain major threats, exploiting unpatched software to breach networks quickly.
Experts recently spotted LockBit 5.0, a new version targeting Windows, Linux, and ESXi systems. It was first advertised on September 3, 2025, marking the gang’s sixth anniversary.
The researchers also reported that the active data-leak sites hit a record 81 in Q3 2025, reflecting the rise of smaller ransomware groups after major players like LockBit and RansomHub declined. The surge shows growing fragmentation in the ransomware ecosystem, with new groups likely to target SMBs that have weaker defenses despite lower potential profits.
“By Q3 2025, newly emerged groups like “Beast,” “The Gentlemen,” and “Cephalus” fueled a 31% surge in attacks on organizations in the health care sector, surpassing established names like Qilin and Inc Ransom and showcasing that smaller groups, collectively, can be just as destructive as their prominent counterparts.” continues the report. “This sharp increase follows the brief relief in Q2 2025, when health care listings dropped due to the absence of the previously dominant group RansomHub.”
In Q3, ransomware groups continued targeting professional, scientific, and technical services, manufacturing, and construction. PSTS attacks rose 17%, while manufacturing and construction declined by 5% and 19%, showing ransomware actors’ shifting, opportunistic focus.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, ransomware)


