
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

A new Drydex campaign targeted British businesses

Security experts at IBM X-Force team discovered a new hacking campaign based on the infamous Dridex trojan. Security experts at IBM X-Force team discovered a new wave of attacks based on the Dridex malware targeting British businesses. The malware has targeted rich UK bank accounts in a new campaign that is operated by threat actors well-resourced, a criminal […]

A new Drydex campaign targeted British businesses

Security experts at IBM X-Force team discovered a new hacking campaign based on the infamous Dridex trojan.

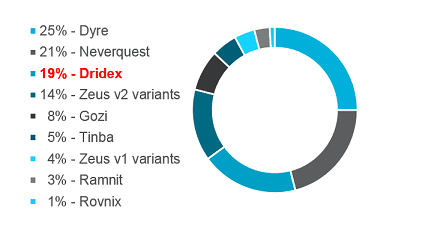
A detailed analysis of the redirection mechanism allowed X-Force researchers to link the new Dridex infection to the Dyre Trojan’s redirection attack scheme, the unique difference in redirection mechanism is that while Dyre redirects via a local proxy, the Dridex redirects via local DNS poisoning.

“X-Force researchers studied the attacks linked with the new Dridex infection campaigns and learned that the malware’s operators have made considerable investments in a new attack methodology. The new scheme is not entirely novel; it copies the concept of the Dyre Trojan’s redirection attack scheme. The difference between Dyre and Dridex is the way in which the redirection takes place: Dyre redirects via a local proxy, while Dridex redirects via local DNS poisoning.” states the post.

By implementing this attack scheme, the attackers aim to deceive victims into divulging authentication codes,

“When Dyre started using this scheme, it was targeting over a dozen banks; a rather resource-intensive operation that eventually drove Dyre’s operators to switch back to using web injections and page replacements.”

According to the experts, Dridex operators are scaling up on quantity and quality, the number of banks targeted by the cyber criminals behind this threat is increasing and the code is even more sophisticated and continuously updated.

“Dridex also continues to scale up in victim quality. The bank URLs on the target list are, for the most part, the dedicated subdomains for business and corporate account access. By targeting the higher-value customers in each bank, Dridex’s operators are clearly planning to make large fraudulent transfers out of business accounts and are less enticed by personal banking.”

Pierluigi Paganini

(Security Affairs – Dridex Trojan, cybercrime)


