
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Omicron-themed phishing attacks spread Dridex and taunt with funeral helpline

A gang behind a recent Dridex Omicron campaign is moking the victims taunting them with a COVID-19 funeral assistance helpline number. Crooks behind a recent Dridex campaign is moking the researchers and victims taunting them with a COVID-19 funeral assistance helpline number The phishing messages use weaponized Word or Excel attachments to install the Dridex […]

Dridex COVID-19 Omicron 2

A gang behind a recent Dridex Omicron campaign is moking the victims taunting them with a COVID-19 funeral assistance helpline number.

Crooks behind a recent Dridex campaign is moking the researchers and victims taunting them with a COVID-19 funeral assistance helpline number

The phishing messages use weaponized Word or Excel attachments to install the Dridex banking Trojan.

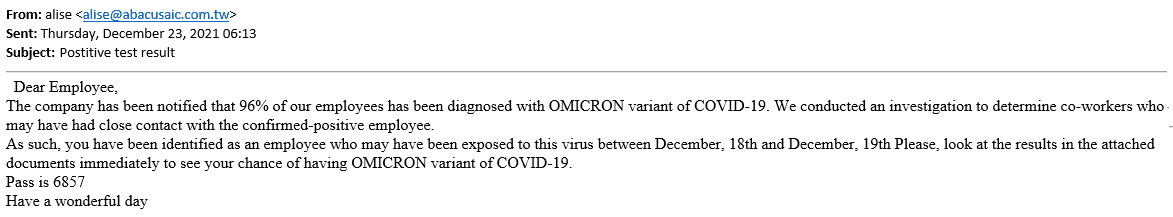
Researchers from MalwareHunterTeam and 604Kuzushi first spotted this campaign, the spam messages have the subject “COVID-19 testing result” and claim the recipient was exposed to a coworker who tested positive to the new Omicron COVID-19 variant.

The threat actors behind this campaign attempt to benefit from the rapid diffusion of the COVID-19 Omicron variant.

“This letter is to inform you that you have been exposed to a coworker who tested positive for OMICRON variant of COVID-19 sometime between December 18th and 20th,” reads a phishing message shared by Bleeping Computer. “Please take a look at the details in the attached document.”

Dridex COVID-19 Omicron 2

The message attempts to trick the victims into enabling the macros to correctly view the content of the attachments.

The messages use a password-protected Excel attachment, the password is provided in the content of the message. Upon entering the password, the recipient is shown a blurred COVID-19 document and is prompted to ‘Enable Content’ to correctly view it.

Once the system is infected, the malware taunts the victims by displaying an alert containing the phone number for the “COVID-19 Funeral Assistance Helpline.”

If you receive a suspicious email like the ones described in this post do not open the attachment.

Follow me on Twitter: @securityaffairs and Facebook

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, COVID-19 Omicron)

[adrotate banner=”5″]

[adrotate banner=”13″]


