
Boffins developed a tool dubbed DroidMorph that provides morphing of Android applications (APKs) and allows to create Android apps (malware/benign) clones.
A group of researchers from Adana Science and Technology University (Turkey) and the National University of Science and Technology (Islamabad, Pakistan) has developed a tool dubbed DroidMorph that provides morphing of Android applications (APKs) and allows to create Android apps (malware/benign) clones. The experts demonstrated that using the tool it is possible to bypass the Android anti-malware solutions performing permutations of the malware.
The study conducted by the academics aims at developing new techniques to detect and analyze the increasing number of Android malware variants (clones) and stop attacks employing them.
“Malware writers use stealthy mutations (morphing/obfuscations) to continuously develop malware clones, thwarting detection by signature based detectors. This attack of clones seriously threatens all the mobile platforms, especially Android” reads the paper published by the experts.
Then the researchers used the Android APK morphing tool that developed to evaluate the resilience of the current commercial antimalware solutions against attacks employing Android malware clones.
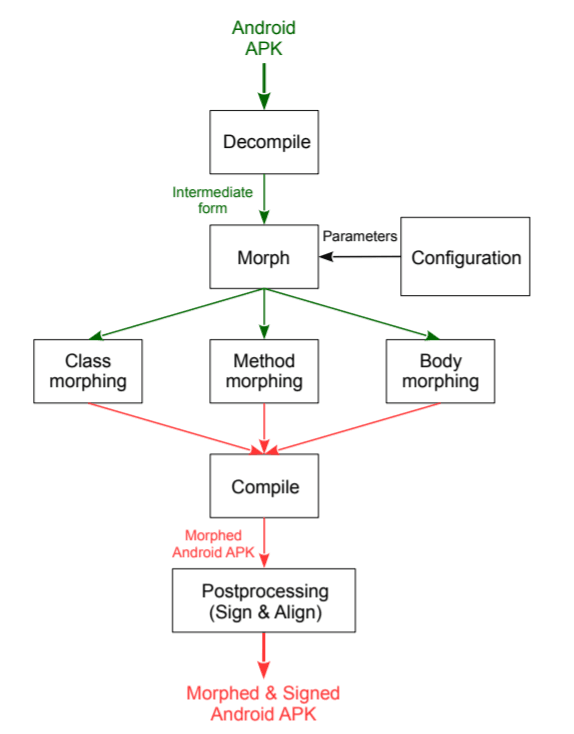
DroidMorph first decompiles an Android APK to an intermediate form, then it carries out morphing at different levels of abstractions (Class, Method, and Body) on it. The morphed intermediate form is then compiled to morphed Android APK. The APK is then signed to generate the final morphed and signed Android APK that is could be executed on the Android devices.
The following images show the architectural overview of DroidMorph:

Experts tested anti-malware products against a combination of trivial and non-trivial obfuscations, the former by changing class and methods name in the code of the app, while the latter is based on alteration of the execution flow of the applications.
The dataset used by the experts for the tests is composed of 848 Android malware apps collected from two different resources.
The researchers used VirusTotal and selected 17 anti-malware programs to detect the malware variants
generated by DroidMorph. They discovered that 8 out of 17 (LineSecurity, MaxSecurity, DUSecurityLabs, AntivirusPro, 360Security, SecuritySystems, GoSecurity, and LAAntivirusLab) commercial anti-malware programs did not detect any of the morphed APKs.

“The number of Android malware clones are on the rise and to stop this attack of clones we need to study how these clones are generated” concludes the report. “In DroidMorph, we have only implemented some basic trivial and non-trivial obfuscations (morphing). Implementation of other obfuscations is work in progress, which will further improve (reduce detection by anti-malware programs) the results. In future, we will further improve morphing at different levels, specifically class level morphing. We will also add morphing of meta information (permissions etc.) embedded in an APK which will further reduce the detection by anti-malware programs.“
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, Android)
[adrotate banner=”5″]
[adrotate banner=”13″]


