
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Tens of thousands of DVRs exposed on Internet with Hardcoded Passwords

According to a report published by Risk Based Security more than tens of thousands of DVRs are exposed on the Internet with a hardcoded password. According to a report published by Risk Based Security (RBS), the firmware of DVRs manufactured by China-based Zhuhai RaySharp contains hardcoded credentials that could be used by a remote hacker […]

Tens of thousands of DVRs exposed on Internet with Hardcoded Passwords

According to a report published by Risk Based Security more than tens of thousands of DVRs are exposed on the Internet with a hardcoded password.

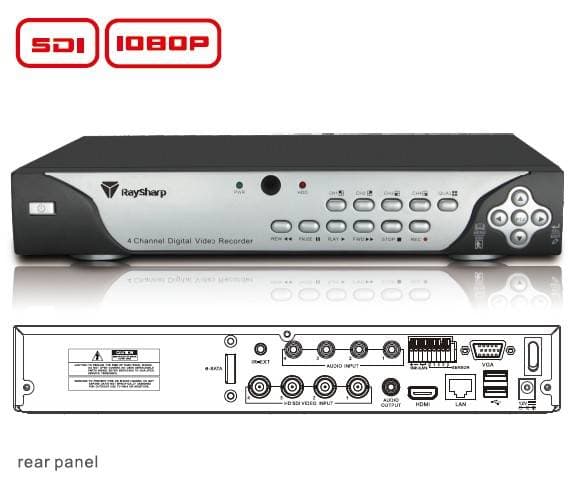
According to a report published by Risk Based Security (RBS), the firmware of DVRs manufactured by China-based Zhuhai RaySharp contains hardcoded credentials that could be used by a remote hacker to gain control of the devices.

“DVRs based on the Zhuhai RaySharp DVR firmware provide a web­based management interface for users to manage the device, view feeds from connected surveillance cameras, and use the PTZ (Pan­Tilt­Zoom) controls. It was found that the interface contains hardcoded credentials that allow anyone to easily access the device. ” states the report.

The digital video recorders include a web interface that allows users to manage the devices, access the recorded video, and control surveillance cameras.

The access to the devices is very simple, they are all configured with the same username “root” and the password “519070.”

There are more than tens of thousands of digital video recorders (DVRs) exposed on the Internet, security experts at Risk Based Security used Shodan revealed that there are between 36,000 and 46,000 DVRs accessible from the web, most of them located in the US.

Vulnerable Shodan DVR on Internet

The security issue is much more extended, according to the experts many other vendors worldwide (i.e. Defender, Lorex, KGuard Security, König, Swann, and COP USA) commercialize digital video recorders using firmware affected by this vulnerability (CVE-2015-8286).

Experts at Risk Based Security reported the vulnerability to the US-CERT in September 2015 that notified all affected vendors in October. Some vendors are working to their own patches but many of them still haven’t solved the problem and RaySharp has yet to release a fix.

The problem affecting DVRs is quite common for IoT devices, poorly configured devices expose them to cyber attacks.

Pierluigi Paganini

(Security Affairs – DVRs, IoT)


