
China-linked threat actor Earth Baku expanded its operations in Europe, the Middle East, and Africa starting in late 2022.
China-linked APT group Earth Baku (a threat actor associated with APT41) has expanded its operations beyond the Indo-Pacific region to Europe, the Middle East, and Africa. Trend Micro researchers observed the APT targeting countries like Italy, Germany, UAE, and Qatar, and the group is suspected to have targeted also entities in Georgia and Romania.
The group targeted multiple industries, including media and communications, telecoms, technology, healthcare, and education and government entities.
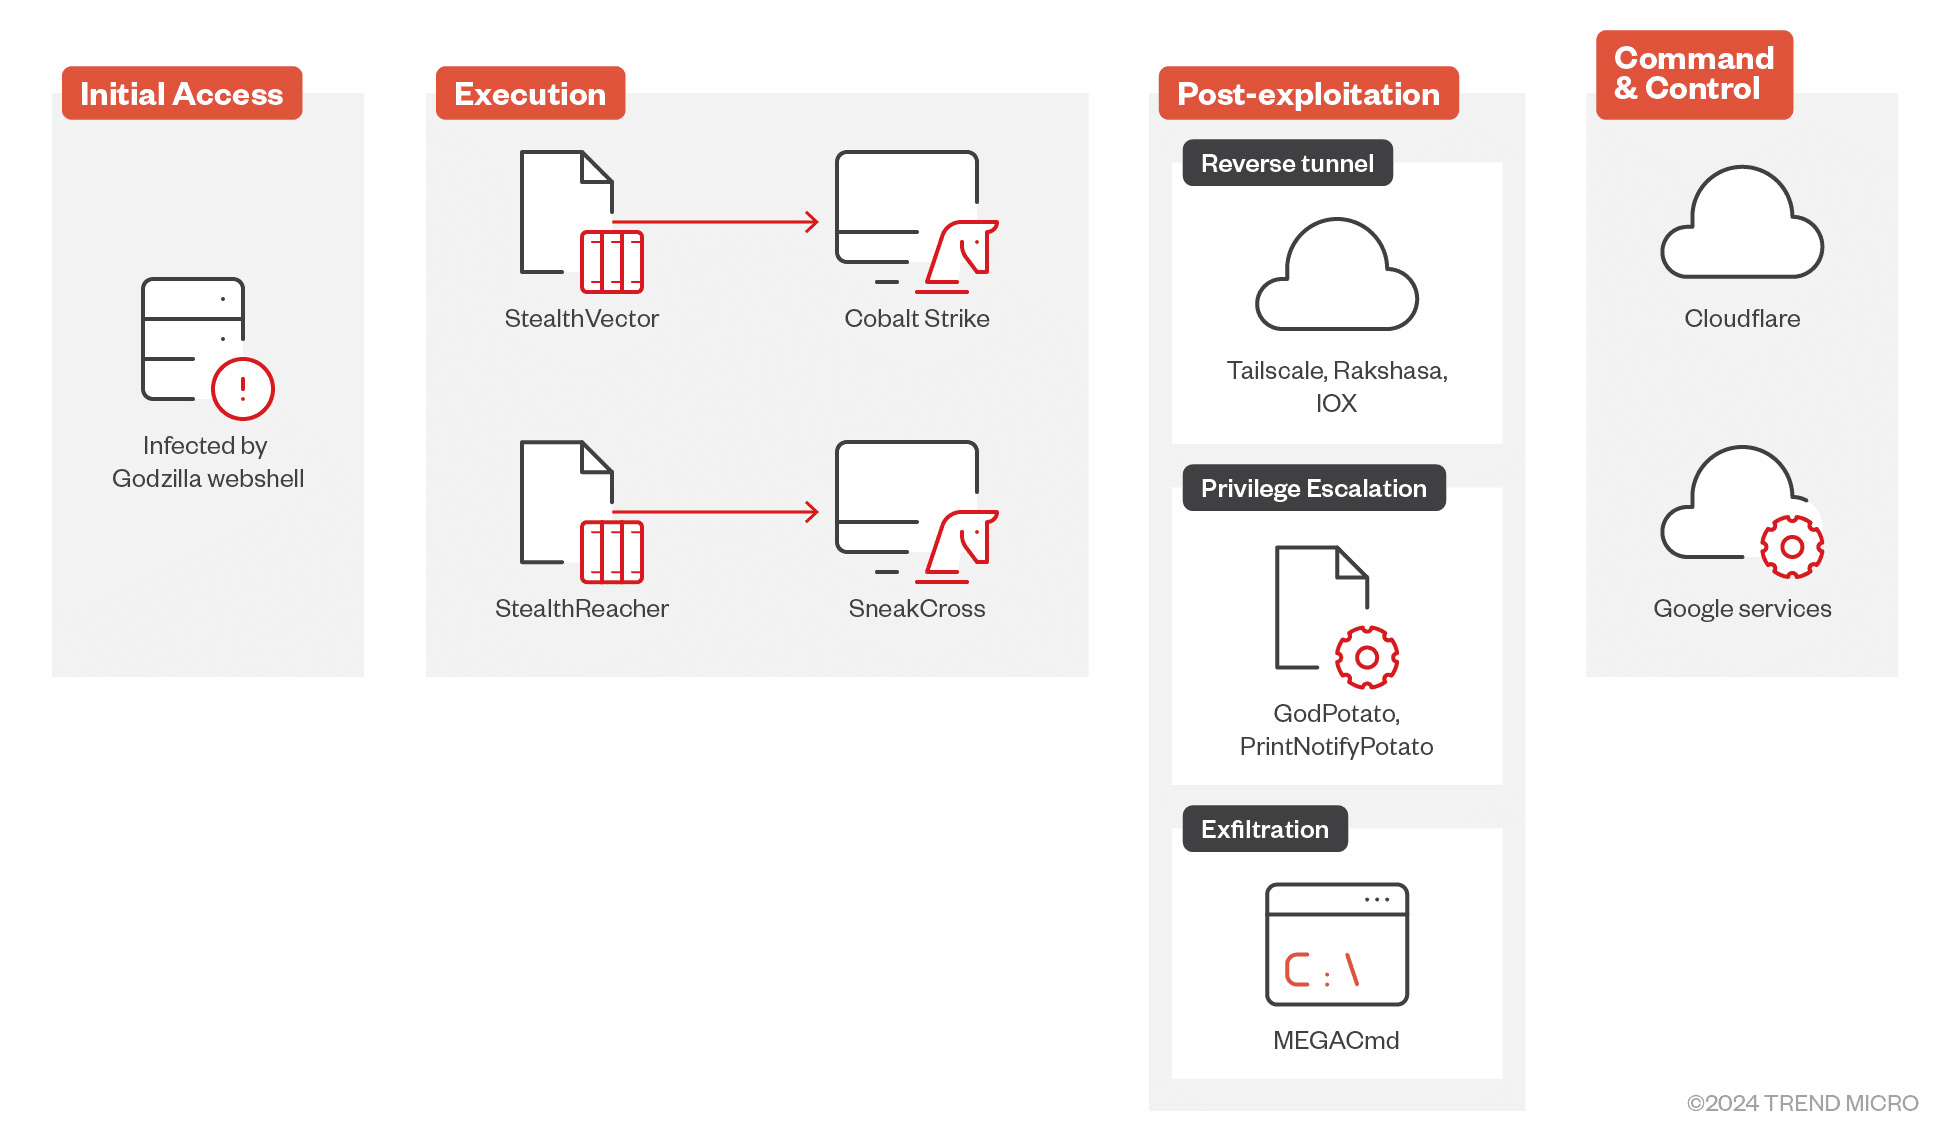
The APT group has updated its tactics, techniques, and procedures (TTPs) in recent campaigns. The group uses of public-facing applications such as IIS servers as entry points, then they deploy sophisticated malware on the victim’s environment, including the custom loaders StealthVector and StealthReacher, and a modular backdoor named SneakCross.
“Once the perpetrators gain access, they deploy the Godzilla webshell, which allows them to maintain control over the compromised server.” reads the report published by Trend Micro. “Through Godzilla, Earth Baku is then able to deploy the shellcode loader StealthVector and its backdoor components, Cobalt Strike, and a new backdoor named SneakCross.”
Earth Baku uses publicly available reverse tunneling tools to maintain control access in post-exploitation activities. The group deploys the MEGAcmd tool in the victim’s environment for data exfiltration.

StealthVector is a custom backdoor loader used to launch the components of the APT’s backdoor in stealth mode. In recent attacks, Earth Baku added two new loaders to its arsenal, CobaltStrike and SneakCross (aka MoonWalk).
The new variant of the StealthVector, while similar to the 2021 version, uses AES encryption instead of the customized ChaCha20. Some variants support code virtualization for obfuscation and employ additional techniques to avoid detection.
StealthReacher is an enhanced version of StealthVector, it incorporates advanced code obfuscation techniques like FNV1-a and additional defense evasion methods. The malware uses AES for encryption and MD5 for checksum, and serves as a loader for the new modular backdoor, SneakCross.
Both StealthVector and StealthReacher use XOR encryption for re-encryption, the researchers discovered that the key used is the victim’s computer name.
SneakCross is a new modular backdoor in the group’s arsenal, it uses Google services for C2. The backdoor relies on Windows Fibers to evade detection. The modular structure allows operators to extend the backdoor capabilities.
Earth Baku used several other tools for post-exploitation activities, including a customized iox tool, Rakshasa, and TailScale for persistence.
“These developments underscore Earth Baku’s evolving and increasingly sophisticated threat profile, which can potentially pose significant challenges for cybersecurity defenses.” concludes the report.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, APT)


