
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Eataly NYC confirms data breach, customers card data exposed

Eataly NYC confirmed that New York retail location has been victim of a security incident, hackers used a PoS malware to steal customers’s card data. The Italian food market Eataly has confirmed a data breach occurred earlier this year. According investigators the data breach could have exposed data related to payment cards over a four-month period. […]

Eataly NYC confirms data breach, customers card data exposed

Eataly NYC confirmed that New York retail location has been victim of a security incident, hackers used a PoS malware to steal customers’s card data.

The Italian food market Eataly has confirmed a data breach occurred earlier this year. According investigators the data breach could have exposed data related to payment cards over a four-month period.

Despite Eataly is a global food market, it seems that only the Eataly’s NYC Retail Marketplace was affected by the data breach.

“As many other retailers, our New York retail location has unfortunately been victim of a security incident. Based upon an extensive forensic investigation, it appears that criminals unscrupulously hacked our network system and installed a malware designed to capture payment card transaction data. We believe that the malware may have compromised the payment card transaction data of customers who made payment card purchases at the Eataly NYC Retail Marketplace, located at 200 5th Avenue, New York, NY 10010, between January 16, 2015 and April 2, 2015.” the Eataly company announced in a statement.

Unknown hackers compromised the company network by installing a PoS malware that was designed to steal customer credit card data, the malicious code was used to siphon data at Eataly location between January 16, 2015 and April 2, 2015.

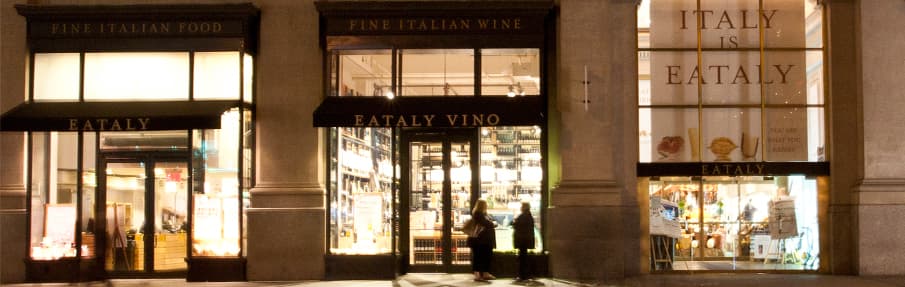
eataly

Eataly hired forensic experts to assist in the investigation and sanitize its systems. As of now, the incident seems to have been contained and the malware removed from the company PoS systems. The company is offering one year of fraud resolution and identity protection to its customers, they just need to sign the free service by sending an email to eataly@protectmyid.com.

“We are advising all potentially affected customers who made payment card purchases at the Eataly NYC Retail Marketplace during the relevant timeframe to check their bank accounts very carefully and immediately report any suspicious charges or activity to their banks and card issuers. In addition, we are offering one year of complimentary fraud resolution and identity protection services to each of our customers who were potentially affected by this incident.” continues the advisory.

Pierluigi Paganini

(Security Affairs – Eataly, data breach)


