
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

eBay promptly fixed a reflected file download vulnerability

EBay has recently fixed a reflected file download vulnerability discovered by the security researcher David Sopas at WebSegura. Ebay is among the web services most targeted by cyber criminals and phishers, over the years, security experts have spotted an impressive amount of attack exploiting techniques more or less sophisticated. Almost every attack relies on social engineering, attackers […]

eBay promptly fixed a reflected file download vulnerability

EBay has recently fixed a reflected file download vulnerability discovered by the security researcher David Sopas at WebSegura.

Ebay is among the web services most targeted by cyber criminals and phishers, over the years, security experts have spotted an impressive amount of attack exploiting techniques more or less sophisticated. Almost every attack relies on social engineering, attackers trick victims into clicking on malicious links or to visit websites hosting any kind of exploit kits used to steal victim’s credentials.

ebay RFD

Security researcher David Sopas at WebSegura discovered a reflected file download vulnerability and reported it to eBay in March. Sopas is a known expert that in the past discovered similar flaw affecting GitHub, Facebook and Instagram. The company promptly solved the problem and releases a fix a few days ago.

“What if malicious users could improve their phishing campaigns on eBay? What if malicious pages linked eBay to download malicious files and infect users?” Sopas wrote in an advisory that is temporary not available.

“When using eBay and inspecting it’s requests I noticed a call to a JSON file that made me wonder a bit about a security vulnerability – Reflected Filename Download.”

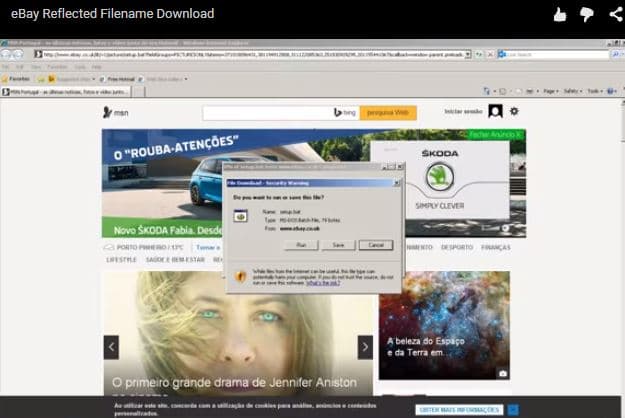
The company promptly solved the problem and released a fix a few days ago. The eBay website was affected by a reflected file download vulnerability that could be exploited by an attacker to trick victims into believing that they were downloading a file from the legitimate website. Sopas explained some browsers, including Internet Explorer 8 and 9, allow the attack by simply visiting a malicious URL, meanwhile other browsers make possible the exploitation of the flaw only by forcing the user to download the file.

The exploitation of the flaw in the eBay domain allow attackers to gain control of the victim’s PC, the user in fact, have no perception of the attack because from their perspective a harmless file is downloaded from the legitimate eBay website. 

“Pretty easy to implement but not easy to find. RFD attacks are still very common and many companies are not aware of it’s real danger,” said Sopas, which connfirmend also that the attack is quite easy to carry out. “The victim always thinks that the source file is on the trusted site.”

Pierluigi Paganini

(Security Affairs – eBay, reflected file download vulnerability)


