
The new strain of educational ransomware EDA2 is infecting systems in the wild, but experts discovered that it is quite easy to neutralize.
Do you remember the EDA2 ransomware?
It is one of the educational ransomware developed by the security expert Utku Sen, now a new variant of the EDA2 educational ransomware appeared in the wild and the good news is that this variant is quite easy to neutralize.
The EDA2 ransomware encrypts victims’ files using AES encryption, then it appends the .locked extension to them. In a way similar to other ransomware, EDA2 also drops notes on the infected machines and informs users that they need to pay .5 bitcoins to restore their files.
According to the experts at Bleeping Computer, the educational ransomware has already infected more than 650 machines and the analysis of the Bitcoin address associated with the ransom request revealed that only 3 victims have paid.
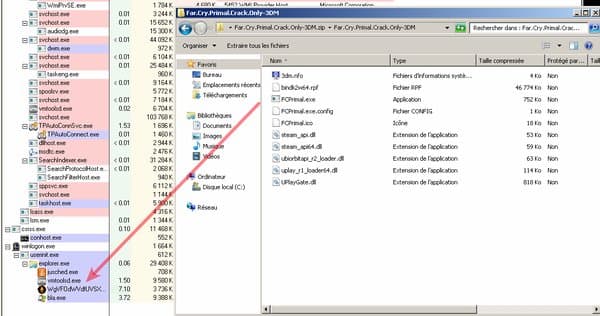
The crooks are targeting online gamers, the EDA2 educational ransomware spread via a link associated with a YouTube video that explains how to crack the Far Cry Primal videogame. When victims try to execute the file crack are infected by the ransomware that encrypts users’ files.

The new strain of educational ransomware EDA2 is infecting systems in the wild, but experts discovered that it is quite easy to neutralize.
Do you remember the EDA2 ransomware?
It is one of the educational ransomware developed by the security expert Utku Sen, now a new variant of the EDA2 educational ransomware appeared in the wild and the good news is that this variant is quite easy to neutralize.
The EDA2 ransomware encrypts victims’ files using AES encryption, then it appends the .locked extension to them. In a way similar to other ransomware, EDA2 also drops notes on the infected machines and informs users that they need to pay .5 bitcoins to restore their files.
According to the experts at Bleeping Computer, the educational ransomware has already infected more than 650 machines and the analysis of the Bitcoin address associated with the ransom request revealed that only 3 victims have paid.
The crooks are targeting online gamers, the EDA2 educational ransomware spread via a link associated with a YouTube video that explains how to crack the Far Cry Primal videogame. When victims try to execute the file crack are infected by the ransomware that encrypts users’ files.
The author of the malware in a bold manner writes in the note that he would never get caught by the authorities.
Utku Sen, the developer that created the educational ransomware, seems to have deliberately inserted security flaws in both the Hidden Tear and EDA2 to sabotage cyber criminals using the proof-of-concept ransomware.
The Sen’s plan worked with the Hidden Tear allowing the recovery of the file encrypted by the Linux.Encoder and Cryptear.B ransomware, meanwhile failed with EDA2.
The developer also inserted vulnerabilities in the EDA2’s control script in order to retrieve decryption keys allowing victims to restore their files.
The keys are then published online giving the opportunity to the victims to restore their files by using the Hidden Tear Decryptor.
Other educational ransomware developed by the Hidden Tear are Magic, Linux.Encoder, and Cryptear.B, all these threats were deliberately affected by a flaw that allows researchers easily to decrypt documents.
(Security Affairs – EDA2 educational ransomware, cybercrime)


