
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Researcher arrested and charged for hacking elections websites

The security expert David Levin was arrested and charged after discovering  serious security flaws on a couple of election websites in Florida. The security researcher David Levin, the owner of Vanguard Cybersecurity, was arrested and charged after discovering  serious security flaws on a couple of elections websites in Florida. In December Levin discovered that the elections website […]

Researcher arrested and charged for hacking elections websites

The security expert David Levin was arrested and charged after discovering  serious security flaws on a couple of election websites in Florida.

The security researcher David Levin, the owner of Vanguard Cybersecurity, was arrested and charged after discovering  serious security flaws on a couple of elections websites in Florida.

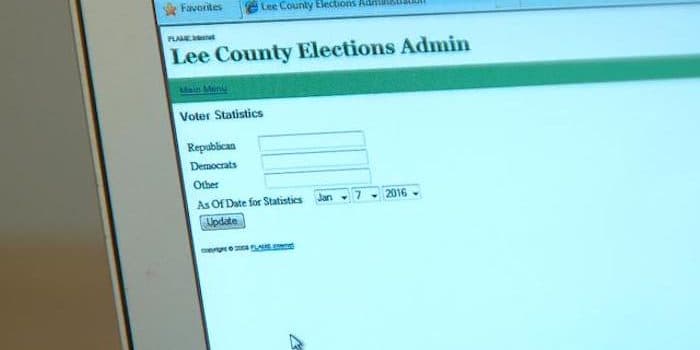
In December Levin discovered that the elections website of Lee County was affected by an SQL injection vulnerability that allowed access to credentials stored in plain text. The expert also analyzed the Florida Division of Elections website discovering security vulnerabilities.

elections websites hack Florida

At this point, the researcher reported the issue to a supervisor of elections candidate, in January he made a video PoC of the SQL injection flaw that allowed him to access the credentials stored in the back-end of the elections website and then reported the issue to the Supervisor of Elections Office.

https://youtu.be/38rsseDeFYQ

Unfortunately, the authorities arrested David Levin of Estero for unauthorized access of Lee County and state elections websites. He was released on a $15,000 bond after a few hours.

“The Florida Department of Law Enforcementaccused the 31-year-old Estero man of hacking into the state elections website Jan. 4 and Jan. 31. He hacked into the Lee County elections website Dec. 19.” reads the news-press.com website.

The Florida Department of Law Enforcement confirmed that the expert exploited on a SQL Injection flaw in order to compromise the election website.

He hacked into the state elections website two times in January and one into the Lee County elections site in December.

“An SQL (Structured Query Language) is a code injection technique used to attack data-driven applications. An SQL injection enables an individual to obtain secure information, such as usernames and passwords, from vulnerable sources.”

Levin was released by the police on a $15,000 bond after a few hours.

It is hilarious, Levin thought he was doing the right thing, but authorities had a different opinion about his activities.

[adrotate banner=”9″]

Pierluigi Paganini

(Security Affairs – elections websites, hacking)


