
Security Affairs
CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Netanyahu’s party Elector app exposes data on over 6.5M Israelis

A misconfiguration in the Elector election day app developed by Likud, the Netanyahu’s party might have exposed data on over 6.5 million Israelis. A misconfiguration in an election day app developed by the Netanyahu’s party Likud, might have exposed personal details of over 6.5 million Israelis. The incident was reported by the Verizon Media developer […]

Israeli voters elector app israel

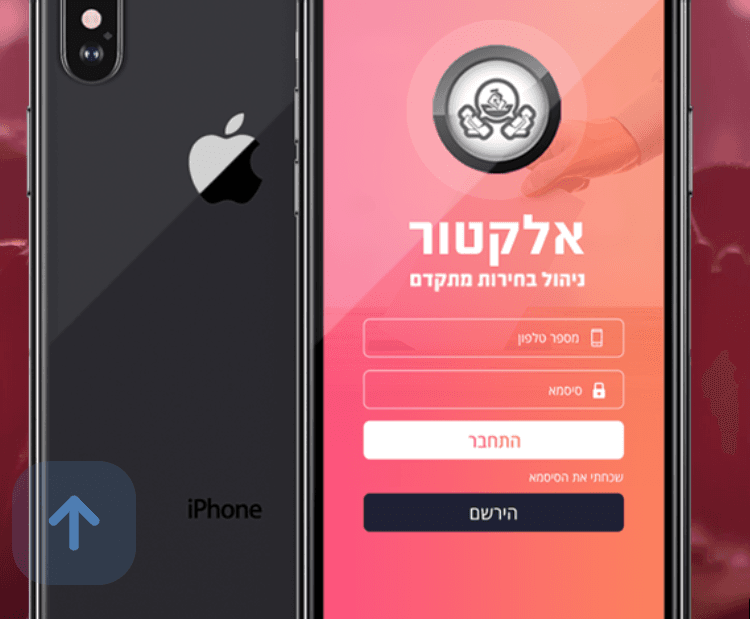
A misconfiguration in the Elector election day app developed by Likud, the Netanyahu’s party might have exposed data on over 6.5 million Israelis.

A misconfiguration in an election day app developed by the Netanyahu’s party Likud, might have exposed personal details of over 6.5 million Israelis.

The incident was reported by the Verizon Media developer Ran Bar-Zik, and Israeli media ([1], [2], [3], [4]) confirmed the data leak.

Bar-Zik explained that he discovered the huge trove of data while was performing a security audit of the Elector app developed by Elector Software for Likud, the Israeli political party led prime minister Benjamin Netanyahu.

elector app israel

“Netanyahu is actually sending Likud activists into a serious security breach, one of the most serious that has been exposed in recent years in Israel.” reads the post published by Calcalist. “Because a major security failure in Elector’s app and system revealed all the Likud’s voter data ahead of the upcoming elections: a huge database of voters and containing up-to-date personal information – ID, full name, address, and phone – of close to 6.5 million Israelis with voting rights.”

At the time it is not clear if the leaked information was accessed also by unauthorized parties before it was discovered.

Bar-Zik decided to assess the app after privacy critics raised by local media in recent weeks.

The Likud app was designed to allow the party’s political supporters to sign up for news and updates during the upcoming Israeli election, on March 2.

The party published the app on the elector.co.il website.

The analysis of the source code of the app revealed the presence of a link to an API endpoint that used to authenticate the site’s administrators.

elector app israel 2

The expert pointed out that the API doesn’t require any authentication to be used to query the application are receive the site’s administrators’s data in cleartext, including their passwords.

Once obtained the credentials, Bar-Zik used them access to the site’s backend, including a database that contained the personal details of 6,453,254 Israeli citizens.

The database was an official and up to date copy of Israel’s voter registration database, which each managed by any party before the election.

“The information includes the ID number, full name, full address, father’s name, ballot and voting address and voter ID – information that actually identifies all the senior citizens of Israel. This information was particularly up-to-date and comprehensive.” continues the post. “Bar Zick himself said that following an apartment move, he updated his address in the Interior Ministry just three weeks ago. His latest address appeared in the uncovered database.”

The records in the database included personal details such as full name, phone number, ID card numbers, home addresses, gender, age, and political preferences.

Following the discovery of the data leak, the official website of the Elector app has been taken down.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Elector app, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


