
Security Affairs
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|U.S. Charges Canadian Man in Alleged Hack of University Supercomputers|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

US Govn contractor Electronic Warfare Associates infected with Ryuk ransomware

The popular US government contractor Electronic Warfare Associates (EWA) has suffered a ransomware attack, the news was reported by ZDNet. Last week, the US government contractor Electronic Warfare Associates (EWA) has suffered a ransomware attack that also infected its web servers. Electronic Warfare Associates provides electronic equipment to the US government, the list of customers […]

Electronic Warfare Associates

The popular US government contractor Electronic Warfare Associates (EWA) has suffered a ransomware attack, the news was reported by ZDNet.

Last week, the US government contractor Electronic Warfare Associates (EWA) has suffered a ransomware attack that also infected its web servers.

Electronic Warfare Associates provides electronic equipment to the US government, the list of customers includes the Department of Defense (DOD), the Department of Homeland Security (DHS), and the Department of Justice (DOJ).

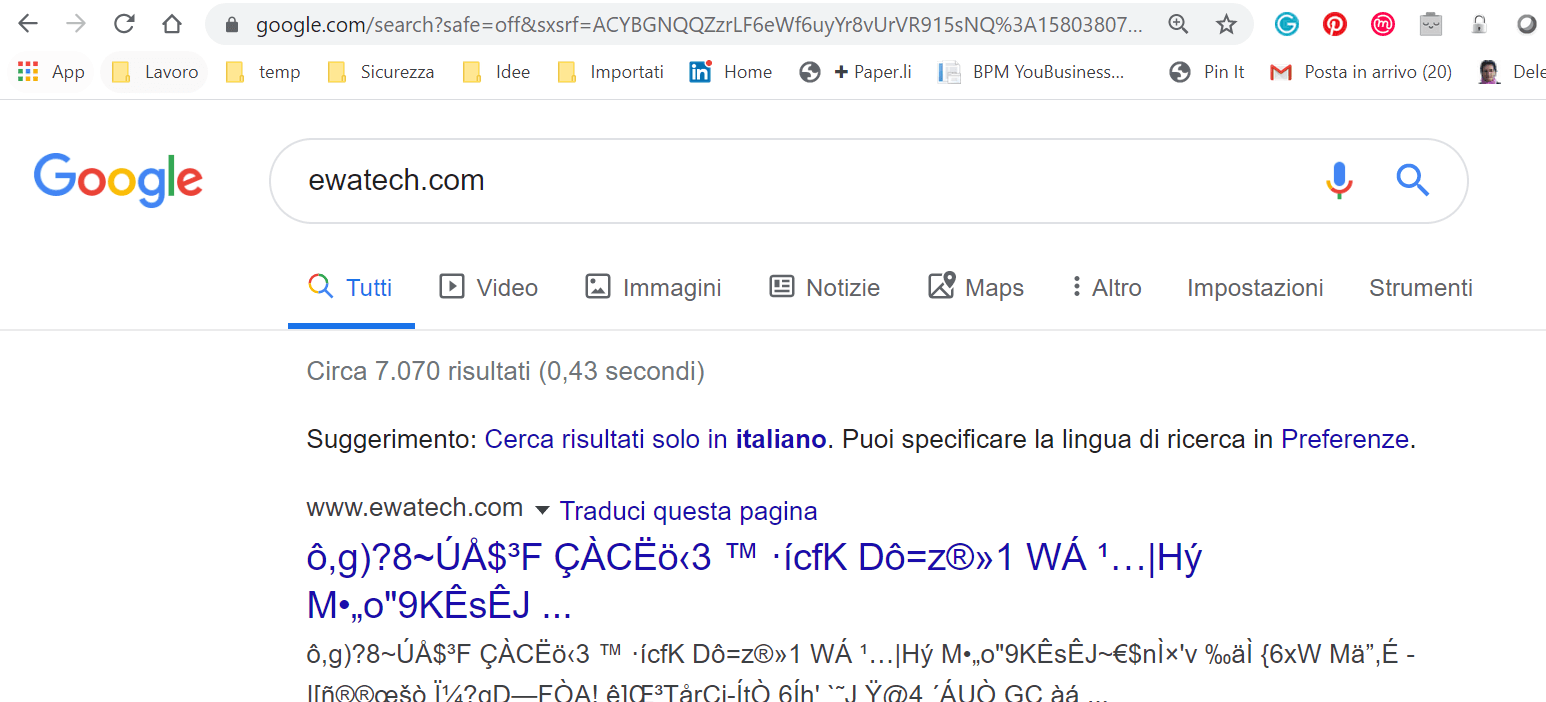
Evidence of the hack is still visible online because Google has cashed the ransom notes and encrypted files.

The encrypted files and ransom note are associated with a Ryuk ransomware infection.

In response to the incident, the company took down the infected web servers, but according to ZDNet other EWA websites have been impacted, including EWA Government Systems Inc., EWA Technologies Inc., Simplicikey, and Homeland Protection Institute.

At the time, Electronic Warfare Associates has yet to disclose the security breach and it is not clear if attackers have exfiltrated data from the company.

A few days ago, security experts from MalwareHunterTeam have discovered a new version of the Ryuk Stealer malware that has been enhanced to allow its operators to steal a greater amount of confidential files related to the military, government, financial statements, and banking.

The new variant of the Ryuk Stealer malware implements a new file content scanning feature and is able to search for additional keywords in the filenames for data exfiltration.

It is not clear if the malware was developed by the threat actors behind Ryuk Ransomware for data exfiltration.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – EWA, Ryuk)

[adrotate banner=”5″]

[adrotate banner=”13″]


