
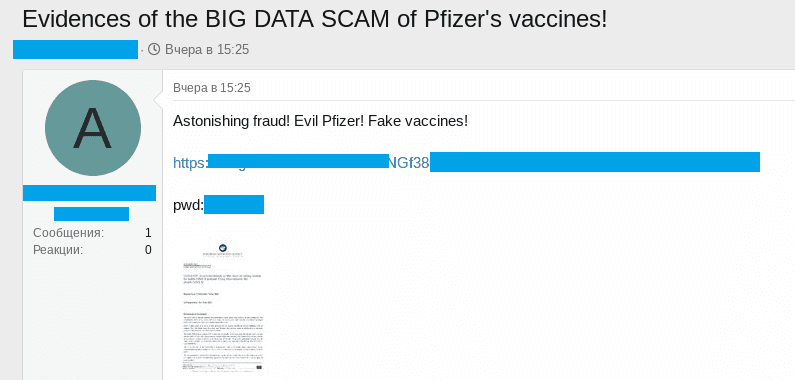
The European Medicines Agency (EMA) revealed Friday that COVID-19 vaccine documents stolen from its servers have been manipulated before the leak.
The European Medicines Agency (EMA) declared that COVID-19 vaccine documents stolen from its servers in a recent cyber attack have been manipulated.
In December, a cyber attack hit the European Medicines Agency (EMA). At the time of the disclosure of the hack, the EMA did not provide technical details about the attack, nor whether it will have an impact on its operations while it is evaluating and approving COVID-19 vaccines.

The European agency plays a crucial role in the evaluation of COVID-19 vaccines across the EU, it has access to sensitive and confidential information, including quality, safety, and effectivity data resulting from trials.
Nation-state actors consider organizations involved in the research of the vaccine a strategic target to gather intelligence on the ongoing response of the government to the pandemic. At the end of November, the Reuters agency revealed in an exclusive that the COVID vaccine maker AstraZeneca was targeted by alleged North Korea-linked hackers.
After the attack, Pfizer and BioNTech issued a joint statement that confirms that some documents related to their COVID-19 submissions were accessed by the threat actors.
Last week, the European Medicines Agency (EMA) revealed threat actors have stolen some of the Pfizer/BioNTech COVID-19 vaccine data and leaked it leaked online.
The agency added that the European medicines regulatory network is fully functional and that the cyber attack had no impact on COVID-19 evaluation and approval timelines.
The investigation conducted by the European Medicines Agency showed that threat actors manipulated emails and documents related to the evaluation of experimental COVID-19 vaccines before leaking them online.
The manipulation of the documents is part of a disinformation campaign aimed at raising doubts about the vaccine and the work of the EMA.
“Some of the correspondence has been manipulated by the perpetrators prior to publication in a way which could undermine trust in vaccines,” the Netherlands-based agency said.
“We have seen that some of the correspondence has been published not in its integrity and original form and, or with, comments or additions by the perpetrators.”
Multiple security firms, such as Cyble and Yarix, have found leaks on underground forums.
“During the assessment of data, our researchers noticed that multiple confidential files, including MoMs, assessment reports, confidential emails, login portal links and images of its internal pages were accessed and leaked.” reported the analysis published by Cyble.

The experts shared screenshots of the internal email where the portal link was shared, the login page for the portal to access the reports, and images of internal pages.

The documents also include the alleged assessment report of COVID-19 vaccine along with the summary report of drug release and stability.
Law enforcement authorities are still investigating the security incident.
If you want to receive the weekly Security Affairs Newsletter for free subscribe here.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, EMA)
[adrotate banner=”5″]
[adrotate banner=”13″]


