
Microsoft Threat Intelligence has observed North Korea-linked APT Emerald Sleet using a new tactic, tricking targets into running PowerShell.
Microsoft Threat Intelligence researchers spotted North Korea-linked threat actor Emerald Sleet (also known as Kimsuky and VELVET CHOLLIMA) using a new tactic. They are tricking targets into running PowerShell as an administrator and executing code provided by the attacker.

Kimsuky cyberespionage group (aka ARCHIPELAGO, Black Banshee, Thallium, Velvet Chollima, APT43) was first spotted by Kaspersky researchers in 2013. The group works under the control of the Reconnaissance General Bureau (RGB) foreign intelligence service. At the end of October 2020, the US-CERT published a report on Kimusky’s recent activities that provided information on their TTPs and infrastructure.
The APT group mainly targets think tanks and organizations in South Korea, other victims were in the United States, Europe, and Russia.
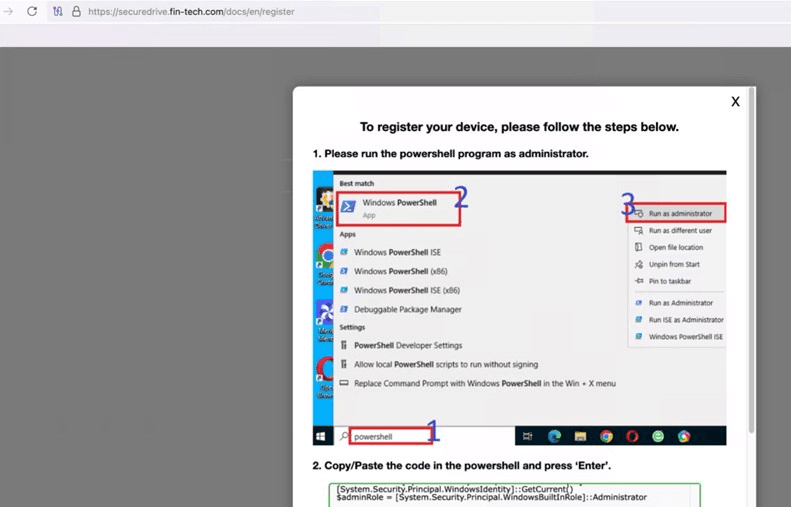
The threat actor impersonates a South Korean government official to build trust with the target before sending a spear-phishing email with a bait PDF attachment. The recipient is tricked into clicking a URL to register their device, which leads to instructions to open PowerShell as an administrator and paste code provided by Emerald Sleet to read the PDF attachment.
Upon running the code as an administrator, it downloads and installs a browser-based remote desktop tool and downloads a certificate file with a hardcoded PIN from a remote server.
Then the code sends a web request to a remote server to register the victim’s device using a downloaded certificate and PIN, enabling the attackers to access the device and exfiltrate data.
“While we have only observed the use of this tactic in limited attacks since January 2025, this shift is indicative of a new approach to compromising their traditional espionage targets.” states Microsoft Threat Intelligence.
Microsoft notifies its customers who have been targeted or compromised by the North Korea-linked APT group.
The IT giant recommends training users about phishing and employing attack surface reduction rules.
Recently, researchers from AhnLab Security Intelligence Center (ASEC) observed North Korea’s Kimsuky APT group conducting spear-phishing attacks to deliver forceCopy info-stealer malware.
According to the ASEC’s report, the state-sponsored hackers send spear-phishing messages to distribute malicious *.LNK shortcut files, disguised as Office documents. When opened, they execute PowerShell or Mshta to download malware like PebbleDash and RDP Wrapper, to control the infected systems.
The attackers use a custom-built RDP Wrapper to enable remote desktop access, likely modifying export functions to evade detection.
The researchers noticed that the threat actors also install proxy malware to achieve external access to the infected systems that are located in a private network.
The Kimsuky group uses keyloggers in multiple file formats, including PowerShell script.
Kimsuky also use the forceCopy stealer malware to capture keystrokes and extract files from browser directories.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Emerald Sleet)


