
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Emotet malware employed in fresh COVID19-themed spam campaign

The Emotet malware has begun to spam COVID19-themed emails to U.S. businesses after not being active for most of the USA pandemic. The infamous Emotet malware is back, operators have begun to spam COVID-19 themed emails to the U.S. businesses. Early this year, the Emotet malware was employed in spam COVID19-themed campaigns that targeted those countries that were […]

EMOTET malware COVID19

The Emotet malware has begun to spam COVID19-themed emails to U.S. businesses after not being active for most of the USA pandemic.

The infamous Emotet malware is back, operators have begun to spam COVID-19 themed emails to the U.S. businesses.

Early this year, the Emotet malware was employed in spam COVID19-themed campaigns that targeted those countries that were already affected by the pandemic.

Since the begin of the COVID19 pandemic in the US in March, the Emotet malware was never employed in Coronavirus-themed spam campaigns against U.S. businesses.

Not the operators behind the threat have started sending out COVID19-themed spam messages to users in the USA.

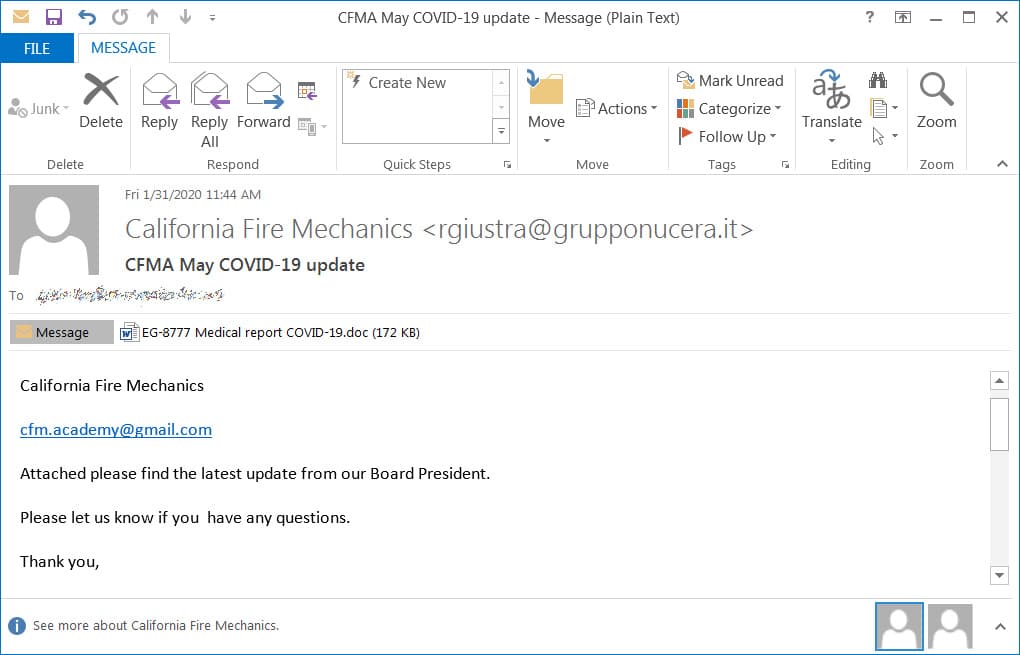
A security researcher that goes online with the Twitter handler Fate112, detected an email that pretends to be from the ‘California Fire Mechanics’ and is using the ‘May COVID-19 update’ subject.

EMOTET malware COVID19

The experts noticed that the template was not created by the Emotet operators, but rather the email was stolen from an existing victim and used in the spam campaigns.

The spam messages used a malicious attachment titled ‘EG-8777 Medical report COVID-19.doc’, which uses a generic document template that pretends to be created from an iOS device and asks the recipients to click on ‘Enable Content’ to view it properly.

Upon clicking on the ‘Enable Content’ button, a PowerShell command will be executed that downloads the Emotet malware from a site under the control of the attackers.

According to BleepingComputer, in the recent campaign Emotet is saved to the %UserProfile% folder and named as a three-digit number (i.e. 498.exe). 

Once infected a system, it will be used to send out further spam emails and to download additional payloads, like TrickBot or Qbot.

Let me suggest you to remain vigilant and double check the attachments of any COVID19-themed message you will receive.

[adrotate banner=”9″][adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – hacking, COVID19)

[adrotate banner=”5″]

[adrotate banner=”13″]


