
Security Affairs
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Retro video game website Emuparadise suffered a data breach

Retro video game website Emuparadise revealed to have suffered a data breach that exposed 1.1 Million accounts back in April 2018. Emuparadise is a website that offers tons of roms, isos and retro video games, users can download and play them with an emulator or play them with the web browser. The security breach occurred in […]

Emuparadise

Retro video game website Emuparadise revealed to have suffered a data breach that exposed 1.1 Million accounts back in April 2018.

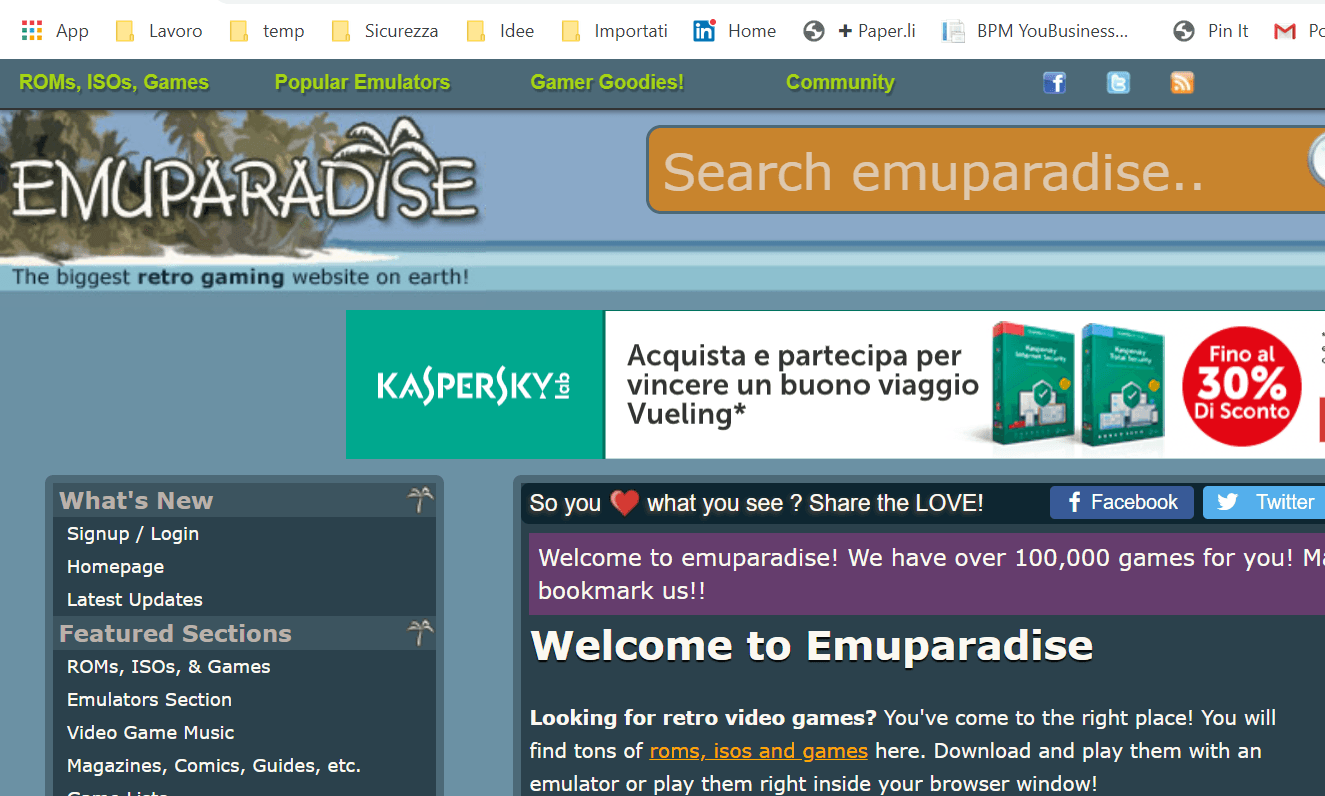
Emuparadise is a website that offers tons of roms, isos and retro video games, users can download and play them with an emulator or play them with the web browser.

The security breach occurred in April 2018 and exposed account information for approximately 1.1 million Emuparadise forum members.

Since August 2018, Emuparadise no longer host game ROMs, anyway it continued to offer any kind of info for retro video games and operated community forums.

Emuparadise hacki

Over the weekend, some Emuparadise forum members reported to have received data breach notification notices from the popular services Have I Been Pwned and HackNotice. The notices notify them of the security breach and inform them that their data were exposed as part of the data breach that occurred in April 2018.

The notice issued by the service Have I Been Pwned states that 1,131,229 accounts from Emuparadise forums were exposed in an incident occurred in April 2018. The forums run on a vBulletin CMS, a very popular platform, but older versions are known to be vulnerable to several issues.

HIBP received the data from dehashed.com on June 9th, 2019, exposed info includes mail addresses, IP address, usernames and passwords stored as salted MD5 hashes.

“In April 2018, the self-proclaimed “biggest retro gaming website on earth”, Emupardise, suffered a date breach.” states Have I Been Pwned. “The compromised vBulletin forum exposed 1.1 million email addresses, IP address, usernames and passwords stored as salted MD5 hashes.

At the time of writing, it is not known how DeHashed obtained the huge trove of data.

Experts pointed out that Emuparadise data are offered for sale in the cybercrime underground and on hacking forums since early 2019.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Emuparadise, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


