
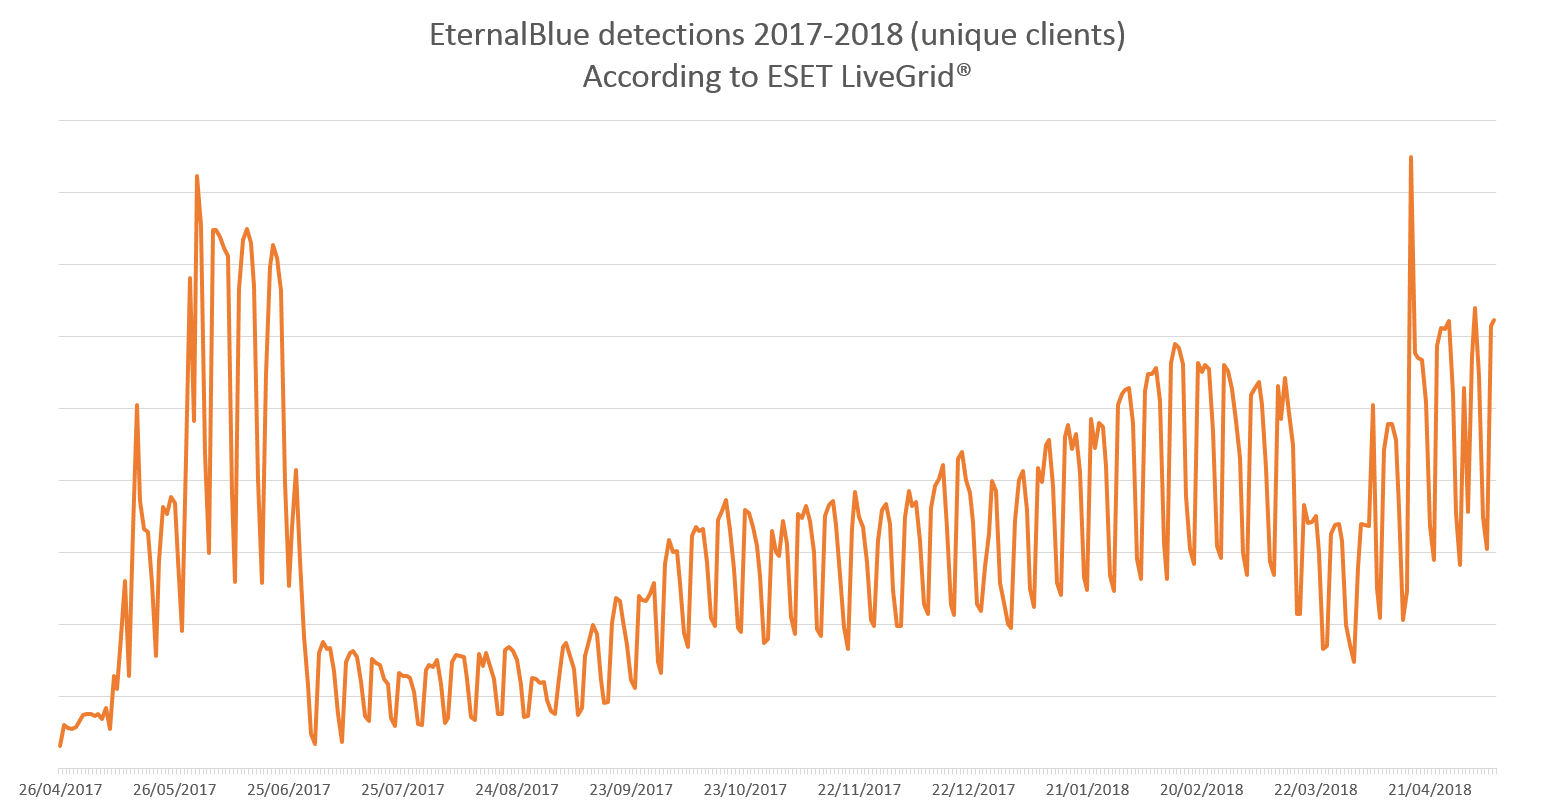
WannaCry ransomware outbreak anniversary – According to researchers from ESET, the popularity of EternalBlue increase significantly over the past months.
Exactly one year ago, on May 12, the WannaCry ransomware infected hundreds of thousands of computers worldwide.
The success of the malware was the use of the EternalBlue exploit that was stolen by Shadow Brokers from the arsenal of the US National Security Agency along with a large cache of tools and exploits.
The group released a 117.9 MB encrypted dump containing documents that suggest NSA hacker SWIFT system in the Middle East.
Some of the codenames for the hacking tools in the dump are OddJob, EasyBee, EternalRomance, FuzzBunch, EducatedScholar, EskimoRoll, EclipsedWing, EsteemAudit, EnglishMansDentist, MofConfig, ErraticGopher, EmphasisMine, EmeraldThread, EternalSynergy, EwokFrenzy, ZippyBeer, ExplodingCan, DoublePulsar.
The tools work against almost all versions of Windows, from Windows 2000 and XP to Windows 7 and 8, and Server 2000, 2003, 2008, 2008 R2 and 2012, except Windows 10 and Windows Server 2016.
In March 2017, a month before EternalBlue was released by Shadow Brokers, Microsoft released the MS17-010 security bulletin containing patches for SMB exploits including EternalBlue.
Just after the leakage online of ETERNALBLUE, security experts started observing a significant increase in the number of malware and hacking tools leveraging the NSA exploit to implement a self-spreading mechanism. Investigations on WannaCry revealed that at least other 3 different groups have been leveraging the NSA EternalBlue exploit.
A few weeks prior to the Wannacry ransomware outbreak, EternalBlue was used by the Adylkuzz botnet for mining activities and by the UIWIX ransomware family.
EternalBlue targets a vulnerability in Windows’ Server Message Block (SMB) on port 445, it only works against older operating system versions, mainly Windows XP and Windows 7.
EternalBlue was later used by other malware, including NotPetya and Bad Rabbit.
According to researchers from ESET, the popularity of EternalBlue increase significantly over the past months.
“And as ESET’s telemetry data shows, its popularity has been growing over the past few months and a recent spike even surpassed the greatest peaks from 2017.” reads the analysis published by ESET.
“EternalBlue had a calmer period immediately after the 2017 WannaCryptor campaign: over the following months, attempts to use the EternalBlue exploit dropped to “only” hundreds of detections daily. Since September last year, however, the use of the exploit has slowly started to gain pace again, continually growing and reaching new heights in mid-April 2018.”

Experts noticed a significant increase in the use of EternalBlue since September 2017 and reached a peak in mid-April 2018, experts believe that a Satan ransomware campaign observed in April contributed to the rapid spike.
“This exploit and all the attacks it has enabled so far highlight the importance of timely patching as well as the need for a reliable and multi-layered security solution that can block the underlying malicious tool,” continues ESET.
To mitigate the threat, disable SMBv1 and do not expose to the internet SMBv2, unfortunately currently millions of devices with SMBv1 are still exposed online most of them in the UAE, US, Russia, Taiwan, and Japan.
Almost a year after WannaCry and there's still over a million SMB servers without auth exposed to the world. At least it looks like "only" 66k of them are running Windows 🤦♂️🤦♂️ pic.twitter.com/ZBlPA0SJU2
— 🇺🇦 Nate Warfield | n0x08.bsky.social🌻 (@n0x08) May 11, 2018


