
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Everis and Spain’s radio network Cadena SER hit by ransomware

NTT DATA-owned firm Everis​ is one of Spain’s largest managed service providers (MSP), it has suffered a ransomware attack, and it was not the only case. Systems at Spain’s largest managed service providers (MSP) Everis have been infected by a ransomware, and it was not alone because the also Spain’s largest radio station Cadena SER […]

Everis ransom note

NTT DATA-owned firm Everis​ is one of Spain’s largest managed service providers (MSP), it has suffered a ransomware attack, and it was not the only case.

Systems at Spain’s largest managed service providers (MSP) Everis have been infected by a ransomware, and it was not alone because the also Spain’s largest radio station Cadena SER (Sociedad Española Radiodifusión) was a victim of a similar attack.

BleepingComputer, that first reported the news, revealed that systems at Everis were infected with the BitPaymer ransomware.

“After the attack began, Everis sent an internal notification saying that they “are suffering a massive virus attack on the Everis network. Please keep the PCs off.”” reported BleepingComputer.

“The network has been disconnected with clients and between offices. We will keep you updated. Please, send urgently the message directly to your teams and colleagues due to standard communication problems,” Everis added.

Files on the Everis systems were encrypted and the variant of BitPaymer ransomware involved in the attack added the .3v3r1s extension to their filenames, a circumstance that suggests it was a targeted attack.

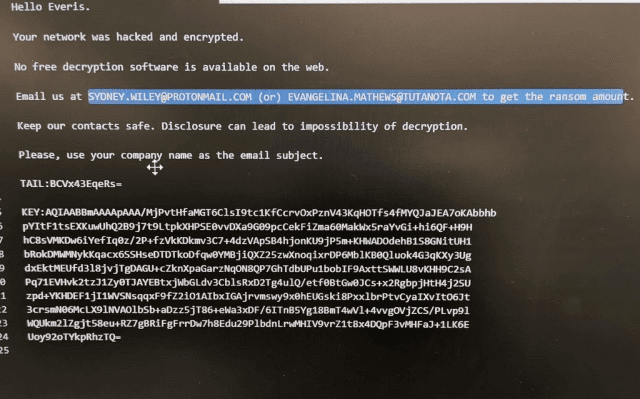
The ransom note dropped on the infected systems warns the company against disclosing the attack, it doesn’t include the ransom amount, instead, it urges the company to contact the operators at the email addressed sydney.wiley@protonmail.com and evangelina.mathews@tutanota.com.

Everis ransom note

According to the website bitcoin.es, crooks asked Everis to pay a €750,000 ($835,923) ransom to recover their files.

An anticipated, Cadena SER, the largest radio station network in Spain, was also infected with an unknown piece of ransomware. In response to the incident, the SER has disconnected all its computer systems from the network.

“The SER chain has suffered this morning an attack of computer virus of the ransomware type , file encrypter, which has had a serious and widespread affectation of all its computer systems.” reads the notice published by Cadena SER.

“The technicians are already working for the progressive recovery of the local programming of each of their stations.”

The news of the ransomware attack against the SER chain was also reported by Spain’s Department of Homeland Security (Departamento de Seguridad Nacional).

It is interesting to notice, that BleepingComputer speculates a possible involvement of the BlueKeep vulnerability in the attacks.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – Everis, ransomware)

[adrotate banner=”5″]

[adrotate banner=”13″]


