
Security Affairs
CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques|FBI Blames North Korea for $6 Billion Binance Crypto Theft|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Mac users using Exodus cryptocurrency wallet targeted by a small spam campaign

Security researchers at F-Secure have recently uncovered a small spam campaign aimed at delivering spyware to Mac users that use Exodus wallet. Security experts at F-Secure have recently spotted a small spam campaign aimed at Mac users that use Exodus cryptocurrency wallet. The campaign leverages Exodus-themed phishing messages using an attachment named “Exodus-MacOS-1.64.1-update.zip.”  The messages were […]

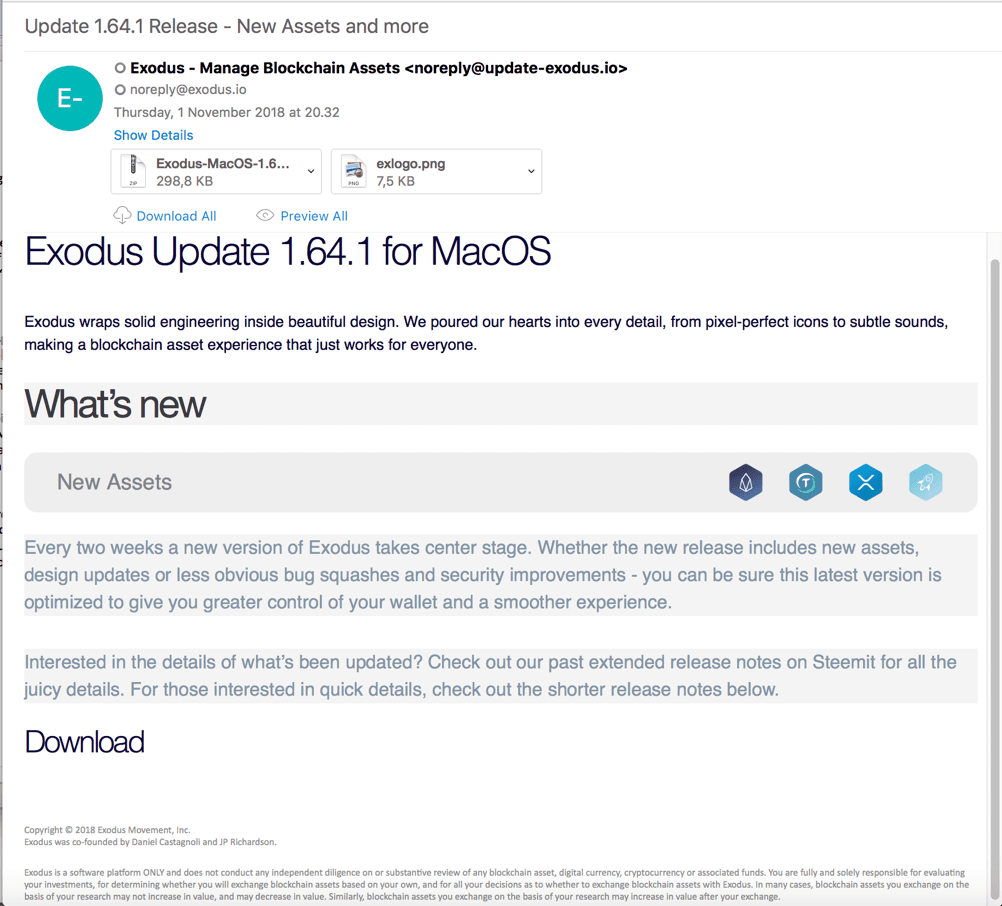
exodus update phishing message

Security researchers at F-Secure have recently uncovered a small spam campaign aimed at delivering spyware to Mac users that use Exodus wallet.

Security experts at F-Secure have recently spotted a small spam campaign aimed at Mac users that use Exodus cryptocurrency wallet.

The campaign leverages Exodus-themed phishing messages using an attachment named “Exodus-MacOS-1.64.1-update.zip.”  The messages were sent by accounts associated with the domain “update-exodus[.]io”, the attackers used it to trick victims into believing that it was a legitimate domain used by the Exodus organization.

The malware poses itself as a fake Exodus update, it is using the subject “Update 1.64.1 Release – New Assets and more”. Experts pointed out that the latest released version for Exodus is 1.63.1.

exodus update phishing message

The zip archive includes an application created earlier this month that contains a mach-O binary with the filename “rtcfg”.The researchers analyzed the code and found several strings and references to the “realtime-spy-mac[.]com” website, a cloud-based remote spy software for Mac systems.
“From the website, the developer described their software as a cloud-based surveillance and remote spy tool. Their standard offering costs $79.95 and comes with a cloud-based account where users can view the images and data that the tool uploaded from the target machine.” states the blog post published by F-Secure. “The strings that was extracted from the Mac binary from the mail spam coincides with the features mentioned in the realtime-spy-mac[.]com tool.”
Experts searching for similar instances of the Mac keylogger in the F-Secure repository and found other applications, including taxviewer.app, picupdater.app, macbook.app, and launchpad.app.

“Based on the spy tool’s website, it appears that it does not only support Mac, but Windows as well. ” concludes F-Secure. “It’s not the first time that we’ve seen Windows threats target Mac. As the crimeware threat actors in Windows take advantage of the cryptocurrency trend, they too seem to want to expand their reach, thus also ended up targeting Mac users.”

Further details about the campaign, including IoCs are reported in the analysis published by F-Secure.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – Exodus wallet, spam)

[adrotate banner=”5″]

[adrotate banner=”13″]


