
Sourc
According to the lawsuit filed by San Diego city attorney Mara Elliott the Experian credit agency never notified the 2013 security breach to the affected consumers as required under California law.
The City of San Diego, California is suing the Experian credit agency for the security breach that the company suffered in 2013.
“San Diego City Attorney Mara Elliott has filed a lawsuit against consumer credit giant Experian, contending the company suffered a massive data breach that affected 250,000 people in San Diego and millions more — but never told customers about it.” states a blog post published on The San Diego Union-Tribune.
“Elliott’s office cited the Internal Revenue Service in saying hackers filed more than 13,000 false returns using the hacked information, obtaining $65 million in fraudulent tax refunds.”
According to the lawsuit filed by San Diego city attorney Mara Elliott, the security breach that was first reported by the popular expert Brian Krebs, lasted for nine months ending in 2013. The company never notified it to the affected consumers as required under California law.
According to The San Diego Union-Tribune, the city attorney argued that data belonging to some 30 million consumers could have been stolen, including information for 250,000 people in San Diego.
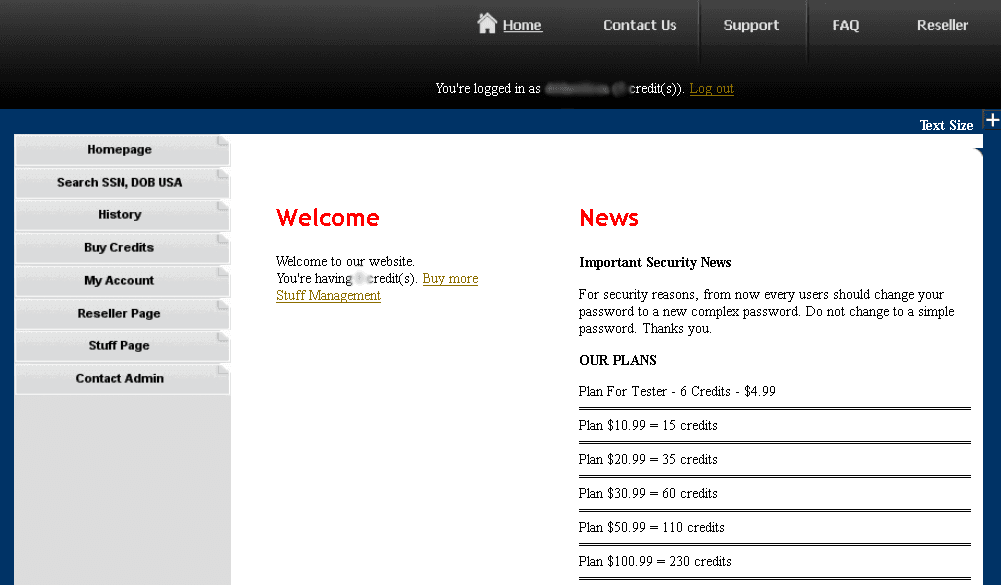
According to Krebs, the Vietnamese man Hieu Minh Ngo ran an identity theft service (Superget[dot]info and Findget[dot]me) and gained access to sensitive consumer information by posing himself as a licensed private investigator in the United States.
The Identity theft service superget[]info was based on data from consumer databases maintained by a company that Experian purchased in 2012.

Source: Krebsonsecurity.com
The man was paying Experian thousands of dollars in cash each month for access to 200 million consumer records, then he was reselling them to more than 1,300 users of his ID theft service.
The man was arrested by US authorities and pleaded guilty to identity fraud charges, he was sentenced in July 2014 to 13 years in jail.
In December 2013, an executive from Experian told Congress that the company was not aware of any consumers that were a victim of a scam-related to the stolen data.
The court order is asking the company to formally notify consumers whose personal information was involved in the security theft and to pay costs for identity protection services for those people.
“The law carries penalties up to $2,500 for each violation, meaning the company could be facing potentially millions in fines.” The San Diego Union-Tribune added.
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(Security Affairs – Experian security breach, tax refund frauds)
[adrotate banner=”5″]
[adrotate banner=”13″]


