Security Affairs
ShinyHunters claims FBI breach after alleged PeopleSoft zero-day attack|EvilTokens made phishing-as-a-service look easy. Then it got taken down|Fake LastPass on GitHub Led to an Infostealer That Killed 145 Security Tools|CVE-2026-87902: how close is your WordPress to remote code execution?|Check Point Fixes a New Actively Exploited Critical Security Flaw|Chaotic Eclipse Released BigDiskBuster, A PoC For Windows Defender Update DoS Zero-Day|Public PoC Exposes Critical Veeam Agent Privilege Escalation|U.S. CISA adds Zyxel flaw to its Known Exploited Vulnerabilities catalog|Contagious Interview: 30,000 devices infected by a fake job interview|Google Fined €403 Million Over Location Data Practices|Foreign Hackers Target Two Colorado Water Utilities|ChainScript: the RAT that hides its command server inside a blockchain contract|ShinyHunters claims FBI breach after alleged PeopleSoft zero-day attack|EvilTokens made phishing-as-a-service look easy. Then it got taken down|Fake LastPass on GitHub Led to an Infostealer That Killed 145 Security Tools|CVE-2026-87902: how close is your WordPress to remote code execution?|Check Point Fixes a New Actively Exploited Critical Security Flaw|Chaotic Eclipse Released BigDiskBuster, A PoC For Windows Defender Update DoS Zero-Day|Public PoC Exposes Critical Veeam Agent Privilege Escalation|U.S. CISA adds Zyxel flaw to its Known Exploited Vulnerabilities catalog|Contagious Interview: 30,000 devices infected by a fake job interview|Google Fined €403 Million Over Location Data Practices|Foreign Hackers Target Two Colorado Water Utilities|ChainScript: the RAT that hides its command server inside a blockchain contract|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Experts temporarily disrupted the RedLine Stealer operations

Security experts from ESET, have temporarily disrupted the operations of the RedLine Stealer with the help of GitHub. ESET researchers announced to have temporarily disrupted the operations of the RedLine Stealer with the help of GitHub. The two companies teamed up with Flare to curb the operations of the malware operators. The experts discovered that […]

RedLine stealer

Security experts from ESET, have temporarily disrupted the operations of the RedLine Stealer with the help of GitHub.

ESET researchers announced to have temporarily disrupted the operations of the RedLine Stealer with the help of GitHub.

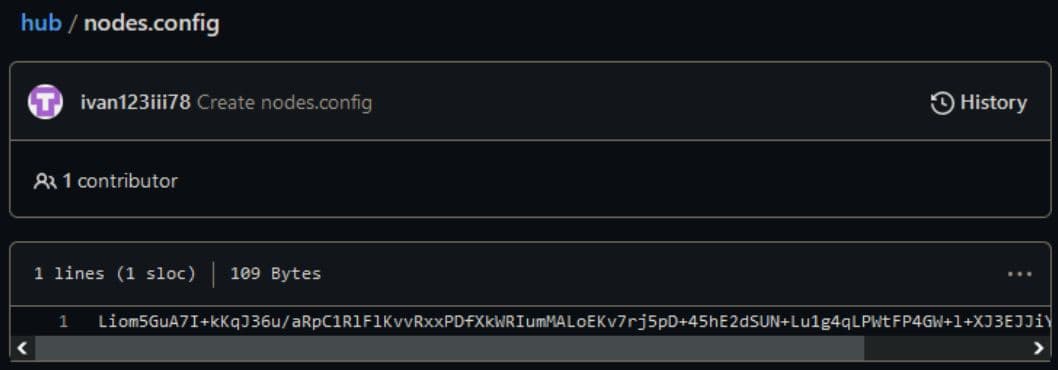
The two companies teamed up with Flare to curb the operations of the malware operators. The experts discovered that the malware control panels use GitHub repositories as dead-drop resolvers.

The RedLine is an info stealing malware written in .NET that is active since at least early 2020. The malware is able to steal sensitive information from the infected systems, including credentials, cookies, browser history, credit card data, and crypto wallets. The info-stealer is considered a commodity malware that is available through malware-as-a-service model.

By analyzing samples of the RedLine Stealer, the ESET researchers identified the following repositories:

  • github[.]com/lermontovainessa/Hub
  • github[.]com/arkadi20233/hub
  • github[.]com/ivan123iii78/hub
  • github[.]com/MTDSup/updateResolver
RedLine stealer

ESET shared its findings with GitHub, which immediately suspended the repositories.

The experts did not observe fallback channels, which means that the removal of these repositories made the control panels unusable. The operators behind the RedLine will be forced to set up new panels to recover their operations.

Please vote for Security Affairs (https://securityaffairs.com/) as the best European Cybersecurity Blogger Awards 2022 – VOTE FOR YOUR WINNERS
Vote for me in the sections:

  • The Teacher – Most Educational Blog
  • The Entertainer – Most Entertaining Blog
  • The Tech Whizz – Best Technical Blog
  • Best Social Media Account to Follow (@securityaffairs)

Please nominate Security Affairs as your favorite blog.

Nominate here: https://docs.google.com/forms/d/e/1FAIpQLSfaFMkrMlrLhOBsRPKdv56Y4HgC88Bcji4V7OCxCm_OmyPoLw/viewform

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, RedLine)