
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Poland and Lithuania fear that data collected via FaceApp could be misused

Poland and Lithuania are probing the potential privacy and security risks of using a Russian-made app FaceApp. Millions of people recently downloaded the FaceApp app and are taking part in the “#FaceApp Challenge” to show friends how they can look like when they will be old and grey. Many security experts are warning of the risks of […]

faceapp

Poland and Lithuania are probing the potential privacy and security risks of using a Russian-made app FaceApp.

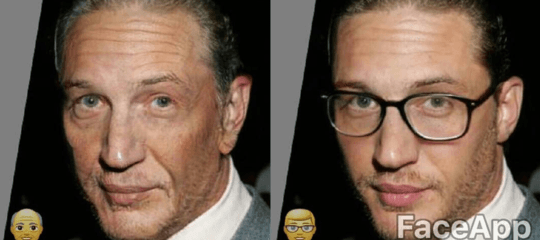
Millions of people recently downloaded the FaceApp app and are taking part in the “#FaceApp Challenge” to show friends how they can look like when they will be old and grey. Many security experts are warning of the risks of using the popular app, threat actors could be potentially interested in data collected by FaceApp.

FaceApp was developed in 2017 by Wireless Lab, when it was downloaded 80 million times, but now thanks to the challenge it is becoming viral. Wireless Lab is a Russian firm based in the Skolkovo hub that is located near Moscow and is considered Russia’s Silicon Valley created by the Kremlin.

The app leverages neural networks to simulate people aging, it adds wrinkles, it turns teeth yellow and colors the hair with gray.

faceapp
Source AGI

Poland’s digital affairs ministry is investigating into the app and it is evaluating the security risks posed by FaceApp to the personal data of its users.

“For several days in Poland and the world over, social media have been flooded by a wave of modified photos of ‘ageing’ users,” states Poland’s digital affairs ministry.

“Various experts point to possible risks related to inadequate protection of users’ privacy,”

Another EU country Lithuania is also investigating the potential risks posed by the use of the app on a large-scale.

According to deputy defense minister Edvinas Kerza the FaceApp authors had cooperated with other Russian internet companies which may not comply with European privacy and security regulations.

In the US, Senate Minority Leader Chuck Schumer called the FBI and the Federal Trade Commission to “look into the national security & privacy risks” associated with the use of FaceApp. 

FaceApp CEO Yaroslav Goncharov attempted to reassure privacy advocates by explaining that Russian authorities did not have access to any user data.

He pointed out that most of the photos collected by the users are deleted from its servers within 48 hours and that is not used for other purposes.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(SecurityAffairs – FaceApp, cybersecurity)

[adrotate banner=”5″]

[adrotate banner=”13″]


