
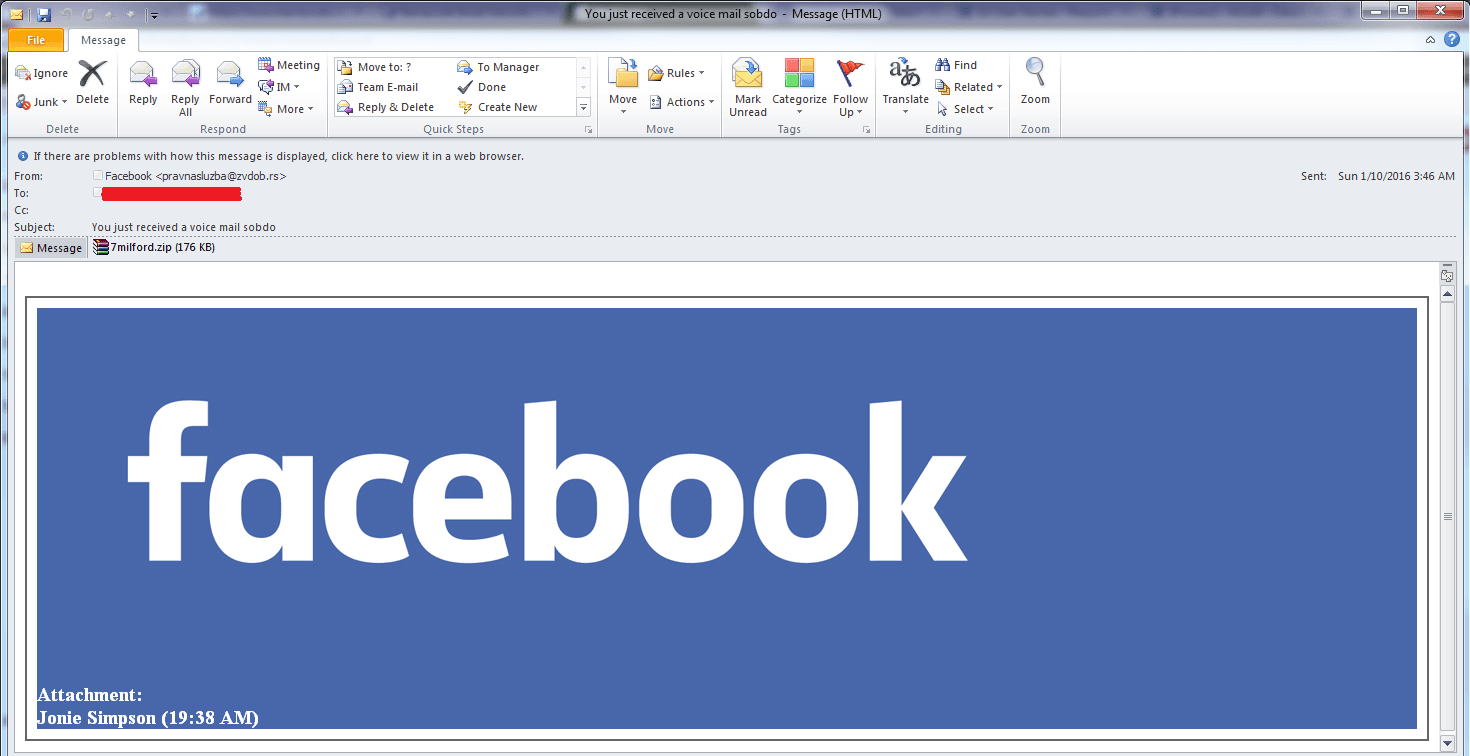
Facebook users are receiving malicious email delivering malware masquerading as audio message, a similar campaign also targeted WhatsApp users.
Social media and instant messaging application are a privileged vector for cyber threats, in many cases bad actors exploited them to spread malicious links and infect a large number of users. Now a new campaign is targeting Facebook users that are receiving emails pretending to be sent by the popular social network informing them of the reception of a voice message.
The fake emails appear as a legitimate communication from Facebook, the subject is composed of random characters (“You got a vocal memo! Fcqw”, “An audible warning has been missed. Yqr”, or “You recently missed a short audible notice. Rtn”) and include in attachment a .zip file containing a variant of the Nivdort information-stealer Trojan.
Experts at Comodo Threat Research Lab noticed many similarities between this campaign and another operation that targeted WhatsApp users recently, for this reason, they believe that the threat actors behind both campaigns are likely the same.
“Earlier this month, the Comodo Threat Research Lab team identified a new malware attack targeted specifically at businesses and consumers who might use WhatsApp. As part of a random phishing campaign, cybercriminals were sending fake emails representing the information as official WhatsApp content to spread malware when the attached “message” was clicked on.
Now, researchers at the Threat Research Lab have identified a very similar phishing campaign targeted at businesses and consumers who use Facebook – most likely designed by the same cyber criminals who developed the WhatsApp malware.” states a blog post published by the Comodo Threat Research Lab.

Both campaigns used the same subjects of the emails, according to the experts the set of random characters is appended to bypass antispam filters.
“These are most likely being used to bypass antispam products rather than identify the user,” the researchers posited.”
Once victims open the file and launch the malware, it will automatically replicate itself into “C:\” directory and add a Windows Registry to gain persistence on the infected system. The malware modifies the Windows Hosts in an attempt to prevent victims from accessing websites of AV vendors, it also attempts to disable Firewall notifications from the Windows Security Center by modifying a Registry entry.
Now you have all the necessary information to prevent such kind of cyber attacks … Take care, many people still fall into the trap!
(Security Affairs – Facebook, malware)


