
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

A new Facebook security feature reveals fraudulent Facebook-like mails

A new Facebook security feature protects users from identity theft, the tech giant is taking note of every email it has “recently” sent to its users. Facebook has rolled out a new security feature to protect users from identity theft, the tech giant is taking note of every email it has “recently” sent to its users. […]

Facebook security feature

A new Facebook security feature protects users from identity theft, the tech giant is taking note of every email it has “recently” sent to its users.

Facebook has rolled out a new security feature to protect users from identity theft, the tech giant is taking note of every email it has “recently” sent to its users.

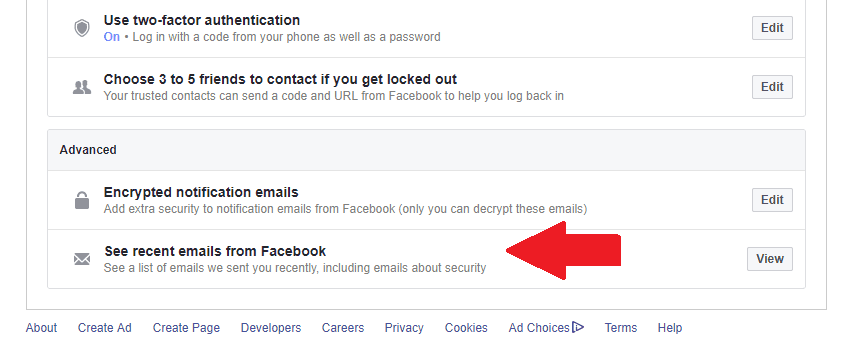
The full list of email sent by Facebook is available under the Settings menu on the social network platform.

Facebook users that will receive a message allegedly sent by the social network giant can check its authenticity by viewing the new “See recent emails from Facebook” section at the bottom of the Security and Login page.

Facebook security feature

If the message is not included in the list it is fraudulent and must be discarded.

“Facebookmail.com is a common domain that Facebook uses to send notifications when we detect an attempt to log in to your account or change a password. If you’re unsure if an email you received was from Facebook, you can check its legitimacy by visiting facebook.com/settings to view a list of security-related emails that have been recently sent.” states the announcement published by Facebook. 

Even if threat actors are able to disguise emails, to make them look like official messages sent by Facebook, the new Facebook security feature will help users to identify phishing attacks.

Crooks use phishing attacks to obtain victim’s credentials, access their profile, and perform a wide range of fraudulent activities.

Compromised accounts could be used to send out phishing messages or to spread malware.

Users that will discover email scam pretending to be sent from the Facebook platform can report it to phish@facebook.com.

If your account has been compromised due to a phishing attempt, visit facebook.com/hacked.

“If you’ve checked this tool and determined that an email you received is fake, we encourage you to report it to phish@facebook.com, and if you believe your account has been compromised due to a phishing attempt, you may attempt to regain access to your account at: facebook.com/hacked. ” concludes Facebook.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – Facebook security feature, phishing)

[adrotate banner=”5″]

[adrotate banner=”13″]


