
Researchers uncovered a malware campaign targeting the infoSec community with fake Proof Of Concept to deliver a Cobalt Strike beacon.
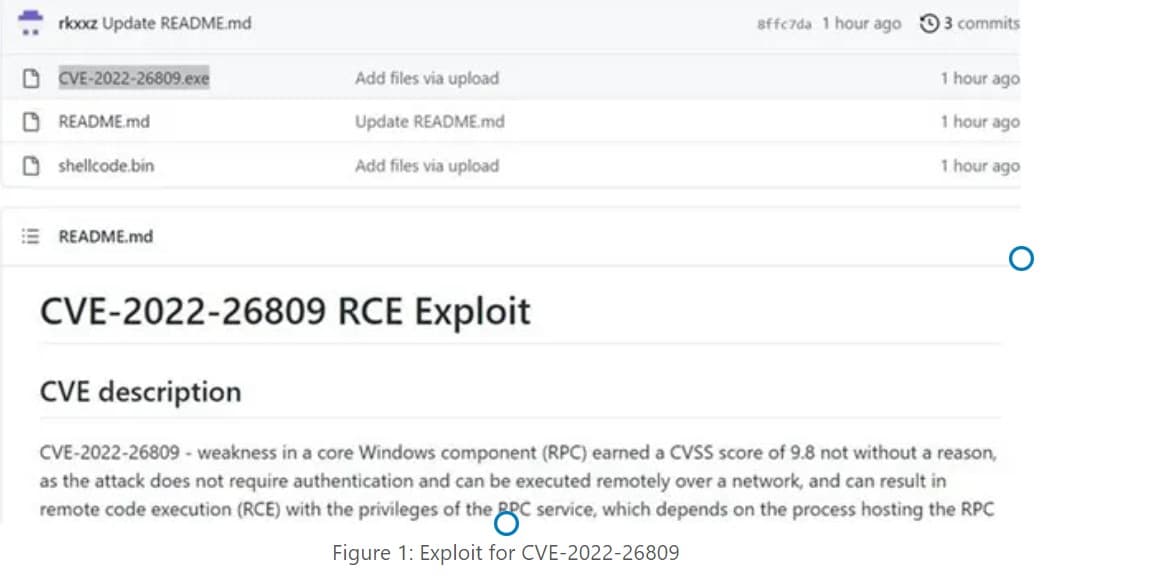
Researchers from threat intelligence firm Cyble uncovered a malware campaign targeting the infoSec community. The expert discovered a post where a researcher were sharing a fake Proof of Concept (POC) exploit code for an RPC Runtime Library Remote Code Execution flaw (CVE-2022-26809 CVSS 9.8). The malware, disguised as a fake PoC code, was available on GitHub.
“Upon further investigation, we discovered that it’s malware disguised as an Exploit. Similarly, we found a malicious sample that appears to be a fake POC of CVE-2022-24500.” reads the post published by Cyble. “Both the malicious samples were available on GitHub. Interestingly both repositories belong to the same profile, indicating the possibility that Threat Actor (TA) might be hosting a malware campaign targeting Infosec Community.”

The researchers also noticed that multiple TAs were also discussing these tainted exploits on the cybercrime forum.
The analysis of the malware revealed that it is a .Net binary packed with ConfuserEX, a free, open-source protector for .NET applications. The malicious code doesn’t include the exploits for the vulnerabilities mentioned on the fake PoC, it only prints a fake message showing that it is trying to exploit and executes shellcode.
The malware executes a PowerShell command using cmd.exe to deliver the actual payload which is a Cobalt-Strike Beacon. Then the threat actors could use the beacon to download additional payloads and perform lateral movements.
“Usually, people working in information security or TAs use exploits to check for vulnerabilities. Hence, this malware might only target people from this community. Therefore, it becomes essential for the Infosec Community members to check the credibility of sources before downloading any proof of concept.” concludes the expert that also shared recommendations along with indicators of compromise (IoCs).
Security Affairs is one of the finalists for the best European Cybersecurity Blogger Awards 2022 – VOTE FOR YOUR WINNERS. I ask you to vote for me again (even if you have already done it), because this vote is for the final.
Please vote for Security Affairs and Pierluigi Paganini in every category that includes them (e.g. sections “The Underdogs – Best Personal (non-commercial) Security Blog” and “The Tech Whizz – Best Technical Blog”)
To nominate, please visit:
https://docs.google.com/forms/d/e/1FAIpQLSdNDzjvToMSq36YkIHQWwhma90SR0E9rLndflZ3Cu_gVI2Axw/viewform
Follow me on Twitter: @securityaffairs and Facebook
| [adrotate banner=”9″] | [adrotate banner=”12″] |
(SecurityAffairs – hacking, fake PoC)
[adrotate banner=”5″]
[adrotate banner=”13″]


