
Security Affairs
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released|Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe|CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code|U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog|Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack|Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions|Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers|NIS2 Makes Board Members Personally Liable for Access Control Decisions|Apple’s spyware notifications reach the Bundestag: what the BSI says to do now|VOLTA, the infostealer that asks an AI which victims are worth the effort|New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia|Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens|
Advertisement

Ad Placeholder

Full Width × 90

Breaking News

Fake WhatsApp app in official Google Play Store downloaded by over a million Android users

A fake WhatsApp version deployed on the Play Store was downloaded by over a million users, a failure for the automated checks implemented by Google. Once again crooks exploited the official Google’s Play Store as a repository for malicious apps. This time a fake WhatsApp version was used to infect over a million users that […]

fake whatsapp

A fake WhatsApp version deployed on the Play Store was downloaded by over a million users, a failure for the automated checks implemented by Google.

Once again crooks exploited the official Google’s Play Store as a repository for malicious apps. This time a fake WhatsApp version was used to infect over a million users that downloaded it.

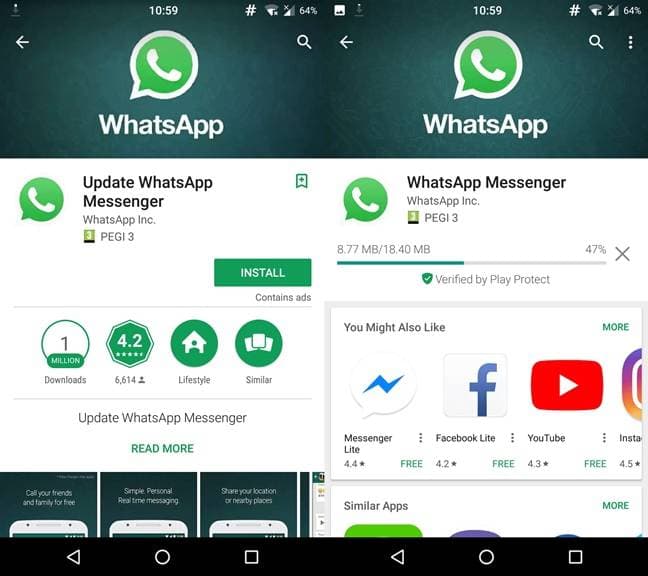
The fake WhatsApp version program first reported by Reddit users, it appears very similar to the original one.

The following image shows on the left the fake WhatsApp, while the legit one is on the right.

fake whatsapp

The Reddit user DexterGenius has decompiled the fake WhatsApp version and discovered it is an ad-loaded wrapper which included the code to download a second apk.

“Yep, also confirmed by long-pressing the link in a browser. I’ve also installed the app and decompiled it,” reported DexterGenius.

“The app itself has minimal permissions (internet access) but it’s basically an ad-loaded wrapper which has some code to download a second apk, also called ‘whatsapp.apk.’ The app also tries to hide itself by not having a title and having a blank icon.”

Fake WhatsApp 2

The malicious app has no title and is associated with a transparent icon.

Fake WhatsApp 3

The fake app appeared to be developed by legit WhatsApp Inc, but a close look at the developer’s name revealed that authors added a hidden space at end of the name. The developer used a trick, it added two bytes, 0xC2 0xA0, at the end forming an invisible space.

It is incredible, crooks that developed this app were able to bypass the Google security controls infecting more than a million devices.

The fake WhatsApp app was removed from the official Play Store and its author is going to be banned.

Experts believe that the automated checks implemented by Google for the apps to deploy in the Play Store are still ineffective, despite the efforts of Big G.

[adrotate banner=”9″] [adrotate banner=”12″]

Pierluigi Paganini

(Security Affairs – Mobile Pwn2Own 2017, hacking)

[adrotate banner=”5″]

[adrotate banner=”13″]


